You have a Microsoft 365 E5 subscription. The subscription contains 500 Windows devices that are onboarded to Microsoft Purview.
You need to prevent users from sharing sensitive information with third-party generative AI websites.
Which Microsoft Purview solution should you use?
A. Data Loss Prevention
B. Insider Risk Management
C. Information Protection
D. Information Barriers
Show Answer
Correct Answer: A
Explanation: Use Microsoft Purview Data Loss Prevention (DLP). Endpoint DLP can detect and restrict users from sharing sensitive information through browser and network activity, including with third-party generative AI websites.
Question 103
HOTSPOT
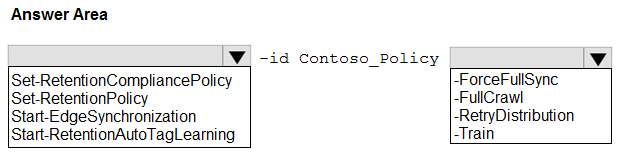
You create a retention label policy named Contoso Policy that contains the following labels:
10 years then delete
5 years then delete
Do not retain
Contoso_Policy is applied to content in Microsoft SharePoint Online sites.
After a couple of days, you discover the following messages on the Properties page of the label policy:
• Status: Off (Error)
• It’s taking longer than expected to deploy the policy
You need to reinitiate the policy.
How should you complete the command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation: The -RetryDistribution switch reinitiates deployment when a retention label policy shows a distribution error.
Question 104
You have a Microsoft 365 subscription linked to a Microsoft Entra tenant that contains a user named User1.
You need to grant User1 permission to search Microsoft 365 audit logs. The solution must use the principle of least privilege.
Which role should you assign to User?
A. the Compliance Management role in the Exchange admin center
B. the Security Reader role in the Microsoft Entra admin center
C. the View-Only Audit Logs role in the Exchange admin center
D. the Reviewer role in the Microsoft Purview portal
Show Answer
Correct Answer: C
Explanation: Assign the View-Only Audit Logs role. It allows User1 to search audit logs without the broader permissions granted by the Compliance Management role. The Security Reader and Reviewer roles do not provide the required audit-log search permission.
Question 105
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site1.
You need to deploy a Microsoft Purview insider risk management solution that will generate an alert when users share sensitive information on Site1 with external recipients.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct answer is worth one point.
A. Turn on analytics.
B. Turn on indicators.
C. Configure adaptive protection.
D. Create an insider risk policy.
E. Create a data loss prevention (DLP) policy.
Show Answer
Correct Answer: B, D
Explanation: Enable the relevant insider risk indicators so SharePoint external-sharing activity can be detected, then create an insider risk policy configured to monitor that activity and generate alerts. Analytics and adaptive protection are not required, and a DLP policy is not needed for this insider risk alert.
Question 106
HOTSPOT
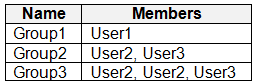
You have a Microsoft 365 E5 subscription that contains three users named User, User2, and User3. The subscription contains the groups shown in the following table.
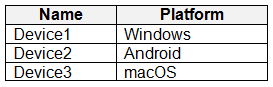
The subscription contains the devices shown in the following table.
All the devices are onboarded to Microsoft Purview.
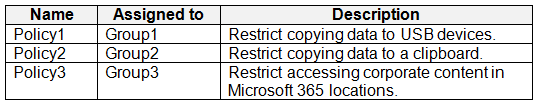
You have the data loss prevention (DLP) policies shown in the following table.
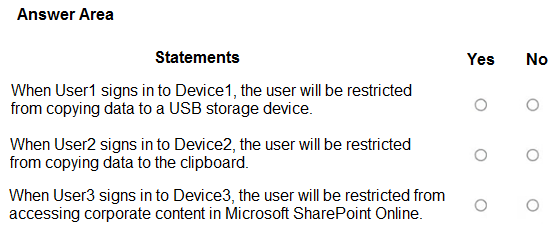
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: User1 on Device1: Yes
User2 on Device2: No
User3 on Device3: Yes
Explanation: User1 is in Group1, and Windows supports the USB restriction. Android does not support the endpoint clipboard restriction for User2. User3 is in Group3, and the Microsoft 365 content restriction applies when accessing SharePoint Online from macOS.
Question 107
HOTSPOT
You have a Microsoft 365 E5 subscription.
You plan to use the Microsoft Purview portal to map human resources (HR) data for use with insider risk management policies.
You need to add a data connector to import the HR data.
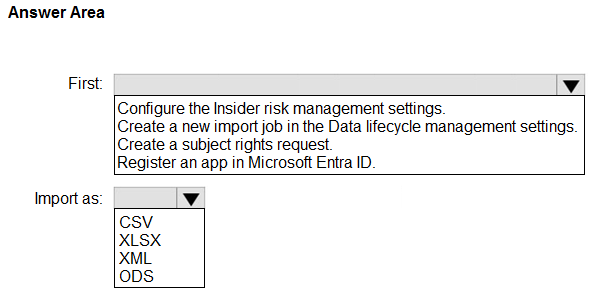
What should you do first, and in which format should you import the data? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: First: Register an app in Microsoft Entra ID.
Import as: CSV.
Explanation: The HR data connector requires an Entra ID app registration for authentication, and HR data is uploaded in CSV format.
Question 108
SIMULATION
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and select the username below.
To enter your password, place your cursor in the Enter password box and select the password below.
Microsoft 365 Username:
Microsoft 365 Password: XXXXXXXXX
If the Microsoft Edge browser or Microsoft 365 portal does not load successfully, select the Microsoft Edge browser icon from the task bar, type the URL “https://admin microsoft.com”, and press Enter.
The following information is for technical support purposes only:
Lab Instance: XXXXXXXX.
Task 7
You need to create a retention policy that meets the following requirements:
• Applies to Microsoft Teams chats and Teams channel messages.
• Retains items for five years from the date they are created, and then deletes them.
Show Answer
Correct Answer: Create a Microsoft Purview retention policy with a static scope.
Select Teams chats and Teams channel messages (including private channel messages, if listed separately).
Retain items for 5 years from when they were created, then delete them automatically.
Explanation: The selected locations cover Teams chats and channel messages. The retention settings use each item's creation date to start the five-year period.
Question 109
You have a Microsoft 365 E5 subscription that contains a user named User1.
You deploy Microsoft Purview insider risk management.
You need ensure that insider risk management events related to User1 are visible only to specific users.
What should you create?
A. a detection group
B. a global exclusion
C. an indicator variant
D. a priority user group
Show Answer
Correct Answer: D
Explanation: Create a priority user group and add User1 to it. When configuring the group, you can specify which users are allowed to view its insider risk management events.
Question 110
You plan to create a new data loss prevention (DLP) policy named DLP1.
DLP1 will be applied to the Exchange email location.
You need to exclude two users named User1 and User2 from DLP1.
What should you do first?
A. Create an organization sharing policy in Microsoft Exchange.
B. Create an advanced DLP rule.
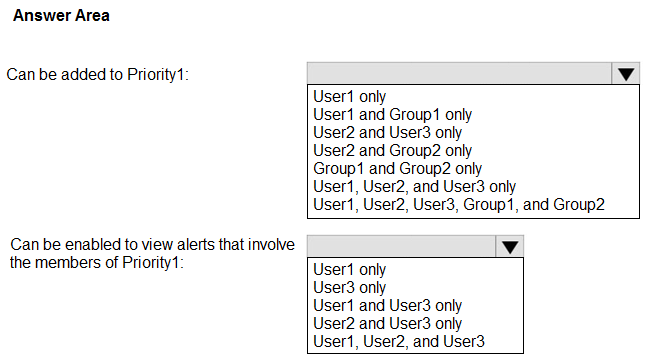
C. Create a mail flow rule in Microsoft Exchange.
D. Create a distribution list that contains User1 and User2.
Show Answer
Correct Answer: D
Explanation: Create a distribution list containing User1 and User2 first. You can then select that group as an exclusion when configuring DLP1 for the Exchange email location.
Question 111
HOTSPOT
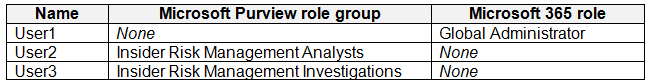
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
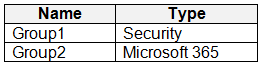
The subscription contains the groups shown in the following table.
You plan to create a priority user group named Priority1.
You need to identify the following:
• Which users and groups can be added to Priority1?
• Which users can be enabled to view alerts that involve the members of Priority1?
What should you identify? To answer, select the appropriate options in the answer area.
Show Answer
Correct Answer: Can be added to Priority1: User1, User2, and User3 only
Can be enabled to view alerts that involve members of Priority1: User2 and User3 only
Explanation: Priority user groups contain user accounts, not groups. Access to alerts involving their members can be granted to users in the Insider Risk Management Analysts or Investigations role groups.
$19
Get all 268 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.