This is the free Microsoft MD-102 practice question bank —
190 of 371 total questions, each with a full explanation, free to
read with no signup required. Updated 2026-10-13.
Every answer is verified against official Microsoft documentation —
see our methodology.
Question 1
You have a Microsoft 365 subscription that uses Microsoft Intune and contains a group named Group1.
You have a line-of-business (LOB) app named App1 that supports in-app notifications. App1 is assigned to all the users in the subscription.
You need to ensure that the users in Group1 receive a custom notification when they launch App1.
What should you do?
A. Create an app configuration policy and assign the policy to Group1.
B. Edit the assignment for App1.
C. Create a device configuration profile and assign the profile to Group1.
D. Create an app protection policy and assign the policy to Group1.
Show Answer
Correct Answer: A
Explanation: App configuration policies in Microsoft Intune are used to deliver configuration settings to managed apps, including vendor-specific settings that enable app features such as in-app notifications or custom behavior. Assigning an app configuration policy to Group1 ensures only those users receive the custom notification when they launch the LOB app. Editing the app assignment only changes deployment targeting, device configuration profiles manage device settings, and app protection policies control data protection rather than app-specific notification behavior.
Question 1
You have a Microsoft 365 subscription that contains 1,000 Windows devices enrolled in Microsoft Intune.
You have the apps shown in the following table.
You need to deploy App1 to the devices.
Which apps can you deploy by using Intune?
A. App1 only
B. App1 and App2 only
C. App1, App2, and App3 only
D. App1, App2, App3, and App4
Show Answer
Correct Answer: D
Explanation: Intune supports Win32 app packages up to 30 GB. The listed app sizes are all at or below that limit, so all four can be deployed.
Question 1
HOTSPOT
-
You have a Microsoft 365 E5 subscription that includes Microsoft Intune.
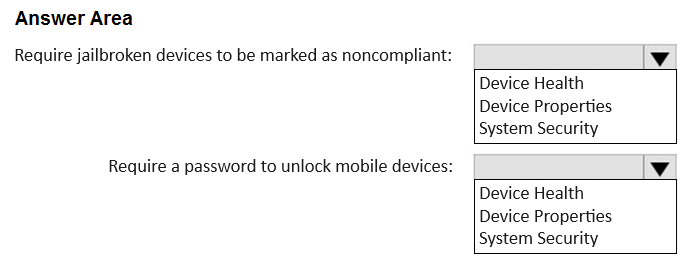
You need to configure a compliance policy for the iOS/iPadOS platform. The solution must meet the following requirements:
• Require jailbroken devices to be marked as noncompliant.
• Mark devices without a password lock as noncompliant.
Which compliance policy settings should you configure for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Jailbroken devices: Device Health
Password to unlock mobile devices: System Security
Explanation: Device Health includes the jailbreak detection setting. System Security includes the password requirement.
Question 1
Case study -
Overview -
ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
ADatum has a Microsoft 365 E5 subscription.
Environment -
Network Environment -
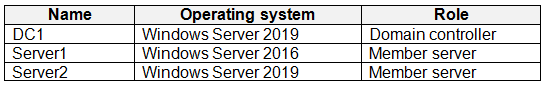
The network contains an on-premises Active Directory domain named adatum.com. The domain contains the servers shown in the following table.
ADatum has a hybrid Azure AD tenant named adatum.com.
Users and Groups -
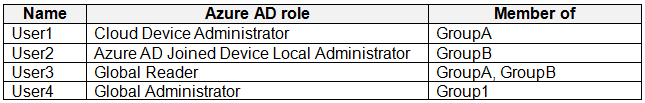
The adatum.com tenant contains the users shown in the following table.
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group1 and Group2 have a Membership type of Assigned.
Devices -
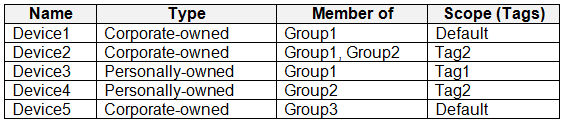
ADatum has the Windows 10 devices shown in the following table.
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune.
The Windows 10 devices are configured as shown in the following table.
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder1.
Microsoft Intune Configuration -
Microsoft Intune has the compliance policies shown in the following table.
The Automatic Enrollment settings have the following configurations:
• MDM user scope: GroupA
• MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
• Name: Protection1
• Folder protection: Enable
• List of apps that have access to protected folders: C:\*\AppA.exe
• List of additional folders that need to be protected: D:\Folder1
• Assignments:
- Included groups: Group2, GroupB
Windows Autopilot Configuration -
ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit.
Currently, there are no devices deployed by using Windows Autopilot.
The Intune connector for Active Directory is installed on Server1.
Requirements -
Planned Changes -
ADatum plans to implement the following changes:
• Purchase a new Windows 10 device named Device6 and enroll the device in Intune
• New computers will be deployed by using Windows Autopilot and will be hybrid Azure AD joined.
• Deployed a network boundary configuration profile that will have the following settings:
- Name: Boundary1
- Network boundary: 192.168.1.0/24
- Scope tags: Tag1
- Assignments:
- Included groups: Group1, Group2
• Deploy two VPN configuration profiles named Connection1 and Connection2 that will have the following settings:
- Name: Connection1
- Connection name: VPN1
- Connection type: L2TP
- Assignments:
- Included groups: Group1, Group2, GroupA
- Excluded groups: --
- Name: Connection2
- Connection name: VPN2
- Connection type: IKEv2
- Assignments:
- Included groups: GroupA
- Excluded groups: GroupB
Technical Requirements -
ADatum must meet the following technical requirements:
• Users in GroupA must be able to deploy new computers.
• Administrative effort must be minimized.
Which user can enroll Device6 in Intune?
A. User4 and User1 only
B. User4 and User2 only
C. User4, User1, and User2 only
D. User1, User2, User3, and User4
Show Answer
Correct Answer: A
Explanation: User1 is in GroupA, the MDM user scope, and has the Cloud Device Administrator role. User4 is a Global Administrator and can enroll the device. User2 is only in the MAM scope; being an Azure AD joined device local administrator does not grant Intune enrollment rights. User3’s Global Reader role is read-only.
Question 2
You have a Microsoft 365 E5 subscription and use the Microsoft Intune Suite. The subscription contains a Microsoft SharePoint Online site named Site1 and 500 Windows devices enrolled in Intune.
You have the apps shown in the following table.
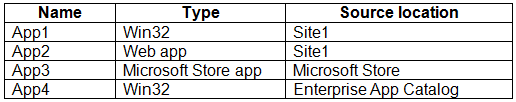
You need to deploy the apps to the devices by using Intune.
For which apps must you upload app package files before you can deploy them?
A. App1 only
B. App1 and App2 only
C. App1 and App4 only
D. App1, App2, and App4 only
E. App1, App2, App3, and App4
Show Answer
Correct Answer: A
Explanation: App1 is a Win32 app hosted on SharePoint, so its package must be uploaded to Intune. App2 is a web link and App3 is a Microsoft Store app, so neither requires an app package upload. App4 can be added from the Enterprise App Catalog, which provides the app package through Intune.
Question 2
HOTSPOT
-
You have a Microsoft 365 subscription that uses Microsoft Intune and contains a Microsoft Tunnel for Mobile Application.
You have the devices shown in the following table.
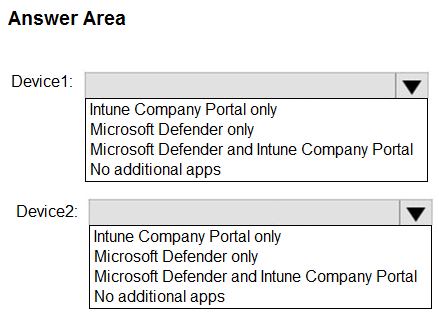
You need to ensure that you can use Tunnel for MAM on each device. The solution must minimize the number of apps required on each device.
Which apps should you install on each device? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Device1: Microsoft Defender and Intune Company Portal
Device2: No additional apps
Explanation: For Microsoft Tunnel for MAM, Android requires both Microsoft Defender and the Intune Company Portal to support the tunnel. On iOS, Tunnel for MAM is built into supported Microsoft apps, so no additional app is required.
Question 2
HOTSPOT
-
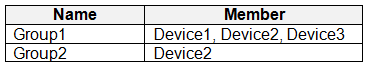
You have an Azure AD tenant named contoso.com that contains the devices shown in the following table.
The tenant contains the Azure AD groups shown in the following table.
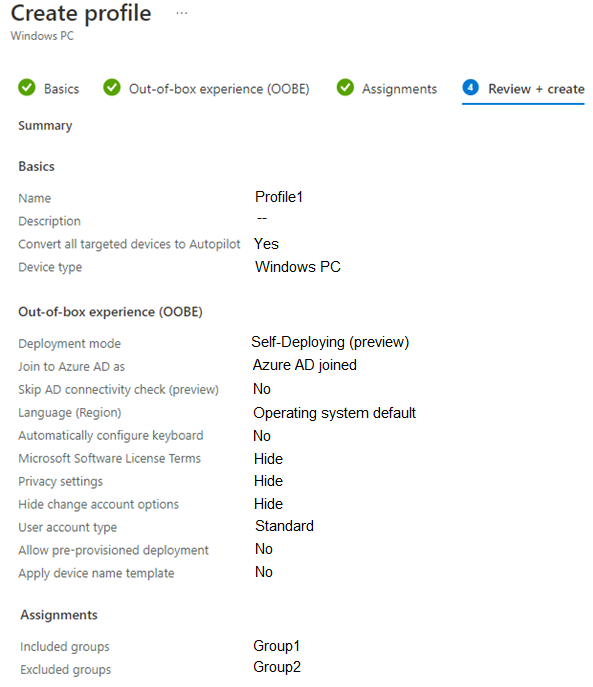
You add an Autopilot deployment profile as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Device1: No
Device2: No
Device3: No
Explanation: Device1 is not enrolled in Intune, so automatic conversion to Autopilot does not apply. Device2 is excluded from the profile. Restarting Device3 does not start an Autopilot deployment.
Question 3
You have a Microsoft 365 E5 subscription.
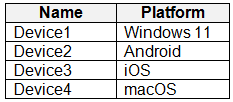
You purchase the devices shown in the following table.
Which devices can be enrolled in Microsoft Intune by using automatic enrollment?
A. Device1 only
B. Device1 and Device2 only
C. Device1 and Device3 only
D. Device1, Device2, and Device3 only
E. Device1, Device2, Device3, and Device4
Show Answer
Correct Answer: A
Explanation: Intune automatic MDM enrollment through Microsoft Entra ID applies to supported Windows devices, including Windows 11. Android, iOS, and macOS use separate platform-specific enrollment methods, so only Device1 qualifies.
Question 3
You have a Microsoft 365 subscription that uses Microsoft Intune and has the following advanced analytics reports enabled:
• Endpoint analytics
• Application reliability
• Work from anywhere
You purchase a new device named Device1 that is enrolled in Intune.
You need to ensure that advanced analytics reports can be generated for Device1.
Which telemetry should you enable for Device1?
A. hardware specifications
B. device cloud-only identity information
C. endpoint performance and user experience data
D. remote wipe status
Show Answer
Correct Answer: C
Explanation: Advanced analytics features in Microsoft Intune, including Endpoint analytics, Application reliability, and Work from anywhere, rely on Windows diagnostic telemetry for endpoint performance and user experience. Enabling endpoint performance and user experience data (required diagnostic data) allows Device1 to contribute data for these reports. The other options do not provide the telemetry used by advanced analytics.
Question 4
You have an Android Enterprise fully managed device named Device1 that is enrolled in Microsoft Intune. Devicel is assigned a device profile.
You plan to manage software updates for Device1 by using Android firmware over-the-air (FOTA). You discover that FOTA is unavailable for Device1.
You need to manage software updates for Device1 by using Intune instead.
What should you use?
A. an app configuration policy
B. an update ring
C. a device configuration profile
D. a device compliance policy
Show Answer
Correct Answer: C
Explanation: For Android Enterprise fully managed devices, if Android FOTA is unavailable, software update behavior can be managed through an Intune device configuration profile (Device restrictions), which includes system update settings. Update rings are for Windows, app configuration policies do not manage OS updates, and compliance policies only evaluate/report compliance rather than configure update behavior.
$19
Get all 371 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.