DRAG DROP -
You have a Microsoft 365 E5 subscription and a computer that runs Windows 11.
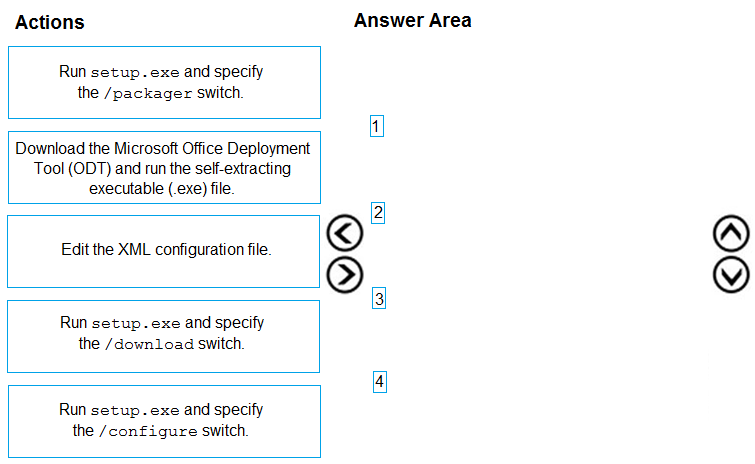
You need to create a customized installation of Microsoft 365 Apps for enterprise.
Which four actions should you perform in sequence? To answer, move the appropriate cmdlets from the list of cmdlets to the answer area and arrange them in the correct order.
Show Answer
Correct Answer: 1. Download the Microsoft Office Deployment Tool (ODT) and run the self-extracting executable.
2. Edit the XML configuration file.
3. Run setup.exe with the /download switch.
4. Run setup.exe with the /configure switch.
Explanation: The XML defines the customized installation. The /download switch retrieves the installation files, and /configure installs Microsoft 365 Apps using those settings.
Question 25
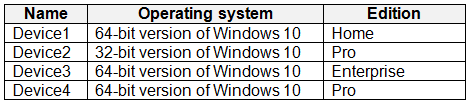
You have the Windows 10 devices shown in the following table.
You plan to upgrade the devices to Windows 11 Enterprise.
On which devices can you perform a direct in-place upgrade to Windows 11 Enterprise?
A. Device3 only
B. Device3 and Device 4 only
C. Device2, Device3, and Device4 only
D. Device1, Device3, and Device4 only
E. Device1, Device2, Device3, and Device4 only
Show Answer
Correct Answer: B
Explanation: Device3 and Device4 run 64-bit Windows 10 Enterprise and Pro, respectively, and can be upgraded in place to Windows 11 Enterprise with appropriate licensing. Device1 runs Home, which requires an edition change, and Device2 runs 32-bit Windows, which cannot be upgraded in place to Windows 11.
Question 26
You have a Microsoft 365 subscription and use Microsoft Intune.
You need to implement Microsoft Tunnel for Mobile Application Management (MAM) for personal Android devices.
You perform the following actions:
• Configure Microsoft Tunnel for managed devices.
• Validate that user devices meet the prerequisites for Tunnel for MAM.
• Create app configuration policies for Microsoft Defender and Microsoft Edge.
What should you configure next?
A. an app protection policy
B. a custom profile for Android Enterprise devices
C. a Conditional Access policy
D. a VPN profile for Android Enterprise devices
Show Answer
Correct Answer: A
Explanation: For Microsoft Tunnel for MAM on personal Android devices, after configuring Microsoft Tunnel, validating prerequisites, and creating the required app configuration policies for Microsoft Defender and Microsoft Edge, the next step is to create and assign an Intune app protection policy (MAM). The app protection policy enables protected apps to use Tunnel for MAM and applies the required mobile application management settings.
Question 26
You have a Microsoft 365 Subscription that uses Microsoft Intune.
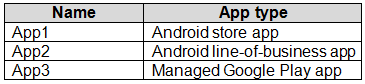
You add apps to Intune as shown in the following table.
You need to create an app configuration policy named Policy1 for the Android Enterprise platform.
Which apps can you manage by using Policy1?
A. App2 only
B. App3 only
C. App1 and App3 only
D. App2 and App3 only
E. App1, App2, and App3
Show Answer
Correct Answer: B
Explanation: Policy1 targets Android Enterprise apps. Of the listed types, only App3 is a Managed Google Play app and can be targeted by this policy. App1 is a regular Android store app, and App2 is an Android line-of-business app; neither is a Managed Google Play app as listed.
Question 27
HOTSPOT
-
You have a Microsoft 365 subscription that includes Microsoft Intune.
Users have iOS devices that use Microsoft Outlook.
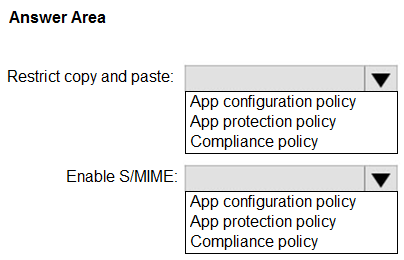
You need to configure Outlook. The solution must meet the following requirements:
• Restrict copy and paste actions from Outlook other apps.
• Enable S/MIME for Outlook.
Which type of policy should you configure for each requirement? To answer, select the appropriate options in the answer area
NOTE: Each correct selection is worth one point.
Explanation: Copy/paste restrictions are controlled by Intune App Protection (MAM) policies. Outlook S/MIME settings for iOS are deployed using an App Configuration policy.
Question 27
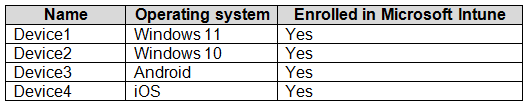
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.
All devices have Microsoft Edge installed.
From the Microsoft Intune admin center, you create a Microsoft Edge Baseline profile named Edge1.
You need to apply Edge1 to all the supported devices.
To which devices should you apply Edge1?
A. Device1 only
B. Device1 and Device2 only
C. Device1, Device2, and Device3 only
D. Device1, Device2, and Device4 only
E. Device1, Device2, Device3, and Device4
Show Answer
Correct Answer: B
Explanation: The Microsoft Edge security baseline in Intune applies to supported Windows devices, not Android or iOS devices. Apply Edge1 to Device1 (Windows 11) and Device2 (Windows 10) only.
Question 28
HOTSPOT
-
You have a hybrid environment that contains a Microsoft Entra tenant and an on-premises Active Directory Domain Services (AD DS) domain.
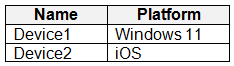
You purchase the devices shown in the following table.
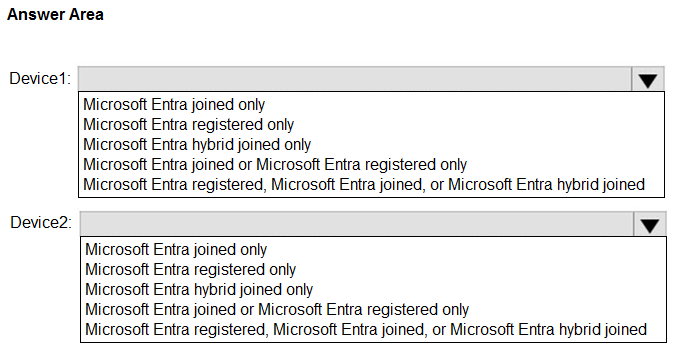
Which Microsoft Entra join type can each device use? To answer, select the appropriate options in the answer area
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Device1: Microsoft Entra registered, Microsoft Entra joined, or Microsoft Entra hybrid joined
Device2: Microsoft Entra registered only
Explanation: Windows 11 supports Microsoft Entra registration, Microsoft Entra join, and Microsoft Entra hybrid join. iOS devices support Microsoft Entra registration (workplace join) but not Microsoft Entra join or hybrid join.
Question 28
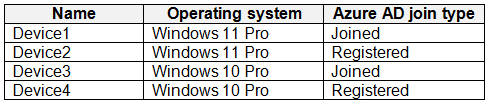
You have an Azure AD tenant that contains the devices shown in the following table.
You purchase Windows 11 Enterprise E5 licenses.
Which devices can use Subscription Activation to upgrade to Windows 11 Enterprise?
A. Device1 only
B. Device1 and Device2 only
C. Device1 and Device3 only
D. Device1, Device2, Device3, and Device4
Show Answer
Correct Answer: A
Explanation: Subscription Activation requires a supported Pro device that is Microsoft Entra joined or hybrid joined, and it changes the Windows edition—it does not upgrade the device to a newer Windows version. Device1 is Windows 11 Pro and joined. Device2 and Device4 are only registered, while Device3 runs Windows 10 Pro and would need a separate OS upgrade to Windows 11.
Question 29
Case study -
Overview -
Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
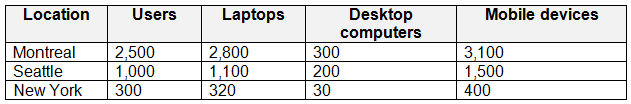
Contoso has the users and computers shown in the following table.
The company has IT, human resources (HR), legal (LEG), marketing (MKG), and finance (FIN) departments.
Contoso recently purchased a Microsoft 365 subscription.
The company is opening a new branch office in Phoenix. Most of the users in the Phoenix office will work from home.
Existing Environment -
The network contains an Active Directory domain named contoso.com that is synced to Azure AD.
All member servers run Windows Server 2016. All laptops and desktop computers run Windows 10 Enterprise.
The computers are managed by using Microsoft Configuration Manager. The mobile devices are managed by using Microsoft Intune.
The naming convention for the computers is the department acronym, followed by a hyphen, and then four numbers, for example FIN-6785. All the computers are joined to the on-premises Active Directory domain.
Each department has an organizational unit (OU) that contains a child OU named Computers. Each computer account is in the Computers OU of its respective department.
Intune Configuration -
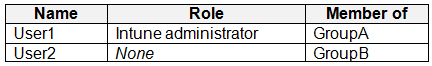
The domain has the users shown in the following table.
User2 is a device enrollment manager (DEM) in Intune.
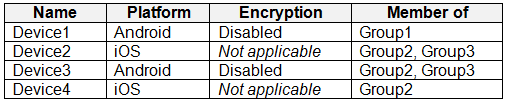
The devices enrolled in Intune are shown in the following table.
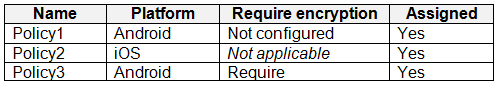
The device compliance policies in Intune are configured as shown in the following table.
The device compliance policies have the assignments shown in the following table.
The device limit restrictions in Intune are configured as shown in the following table.
Requirements -
Planned changes -
Contoso plans to implement the following changes:
• Provide new computers to the Phoenix office users. The new computers have Windows 10 Pro preinstalled and were purchased already.
• Implement co-management for the computers.
Technical Requirements -
Contoso must meet the following technical requirements:
• Ensure that the users in a group named Group4 can only access Microsoft Exchange Online from devices that are enrolled in Intune.
• Deploy Windows 10 Enterprise to the computers of the Phoenix office users by using Windows Autopilot.
• Create a provisioning package for new computers in the HR department.
• Block iOS devices from sending diagnostic and usage telemetry data.
• Use the principle of least privilege whenever possible.
• Enable the users in the MKG department to use App1.
• Pilot co-management for the IT department.
You need to prepare for the deployment of the Phoenix office computers.
What should you do first?
A. Generalize the computers and configure the Device settings from the Microsoft Entra admin center.
B. Extract the serial number of each computer to an XML file and upload the file from the Microsoft Intune admin center.
C. Extract the hardware ID information of each computer to a CSV file and upload the file from the Microsoft Intune admin center.
D. Generalize the computers and configure the Mobility (MDM and MAM) settings from the Microsoft Entra admin center.
E. Extract the serial number information of each computer to a CSV file and upload the file from the Microsoft Intune admin center.
Show Answer
Correct Answer: C
Explanation: Before Windows Autopilot can deploy a profile to the Phoenix computers, their hardware hashes must be registered with the Windows Autopilot service. Export each computer’s hardware ID information to a CSV file, then upload that file through the Intune admin center. Serial numbers alone are not sufficient.
Question 30
HOTSPOT
-
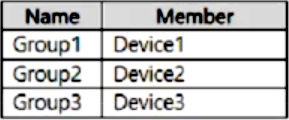
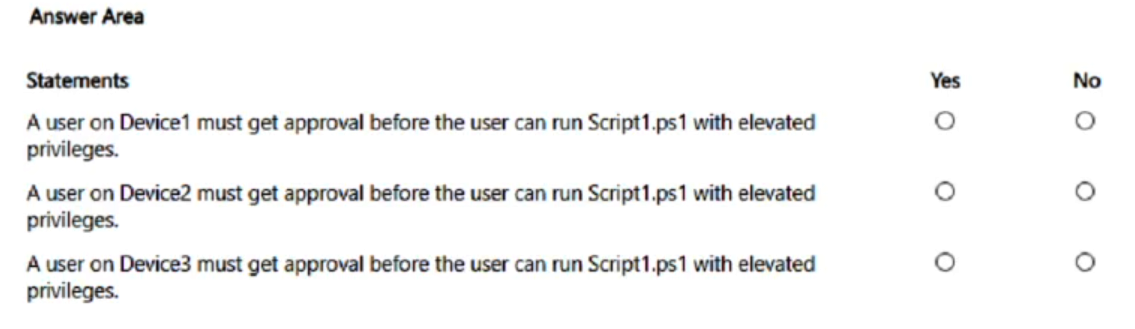
You have a Microsoft 365 E5 subscription that contains three Windows devices named Device1, Device2, and Device3. The devices are managed by using Microsoft Intune. Each device contains a file named Script1.ps1.
Users do NOT have local administrator permissions for the devices.
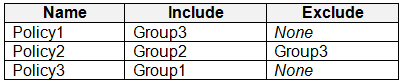
The subscription contains the groups shown in the following table.
You create two Endpoint Privilege Management (EPM) elevation settings policies that have the following settings:
• Name: Policy1
• Endpoint Privilege Management: Enabled
o Default elevation response: Deny all requests
o Allow Elevation Detection: No
o Send elevation data for reporting: No
• Assignments:
o Included groups: Group1
• Name: Policy2
• Endpoint Privilege Management: Require support approval
o Allow Elevation Detection: No
o Send elevation data for reporting: No
• Assignments:
o Included groups: Group3
You create an EPM elevation rules policy named RulesPolicy1 that has the following settings:
• Rule name: Rule1
o Elevation type: Automatic
o Child process behavior: Deny all
o File name: Script1.ps1
o File hash:
Show Answer
Correct Answer: No
No
Yes
Explanation: Device1 receives an EPM settings policy with default 'Deny all requests'; approval is not used. Device2 has no EPM settings policy, so support approval is not required. Device3 receives an EPM settings policy with default 'Require support approval'; without a matching automatic elevation rule for that device, the default behavior is to require approval.
$19
Get all 371 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.