HOTSPOT -
You have an Azure subscription named Sub1 that is linked to a Microsoft Entra tenant named Tenant1. Sub1 contains an Azure VPN gateway named VNetGW1.
You manually register the Azure VPN Client in Tenant1.
You need to configure VNetGW1 to support the Microsoft Entra authentication of Point-to-Site (P2S) VPN connections. The solution must ensure that users can establish P2S VPN connections by using the Azure VPN Client.
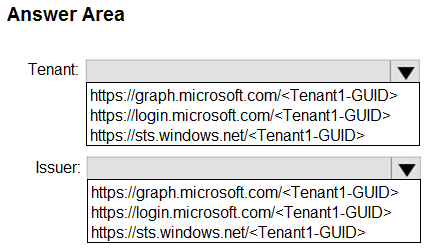
To what should you set Tenant and Issuer in the Point-to-site configuration settings of VNetGW1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation: For Microsoft Entra authentication with the Azure VPN Client, the Tenant field uses the Microsoft identity platform authority endpoint (login.microsoftonline.com), while the Issuer must match the Entra token issuer (sts.windows.net for the tenant GUID).
Question 34
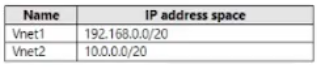
You have two Azure virtual networks in the East US Azure region as shown in the following table.
The virtual networks are peered to one another. Each virtual network contains four subnets.
You plan to deploy a virtual machine named VM1 that will inspect and route traffic between all the subnets on both the virtual networks.
What is the minimum number of IP addresses that you must assign to VM1?
A. 1
B. 2
C. 4
D. 8
Show Answer
Correct Answer: A
Explanation: One private IP address is sufficient. Deploy VM1 as a network virtual appliance in one VNet, enable IP forwarding, and use user-defined routes to direct the relevant subnet traffic in both peered VNets to that IP. The VM does not need a separate IP for each subnet or a NIC in each VNet.
Question 35
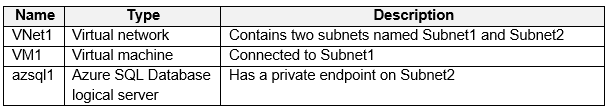
You have an Azure subscription that contains the resources shown in the following table.
You need to ensure that the apps hosted on VM1 can resolve the IP address of the private endpoint for azsql1.database.windows.net.
What should you create first?
A. a public DNS zone named database.windows.net
B. a private DNS zone named database.windows.net
C. a public DNS zone named privatelink.database.windows.net
D. a private DNS zone named privatelink.database.windows.net
Show Answer
Correct Answer: D
Explanation: Create a private DNS zone named privatelink.database.windows.net. Azure SQL Database private endpoints use this zone for resolving the private endpoint IP; the zone must then be linked to the virtual network containing VM1.
Question 36
HOTSPOT -
Case Study -
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study -
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Question button to return to the question.
Overview -
Proseware, Inc. is a financial services company that has a main office in New York City and a branch office in San Francisco.
Existing Environment. Hybrid Environment
Proseware has an on-premises Active Directory Domain Services (AD DS) forest named corp.proseware.com that syncs with a Microsoft Entra tenant named proseware.com.
Proseware has an Azure subscription that is linked to proseware.com.
Proseware has an internal certification authority (CA).
Existing Environment. Network Infrastructure
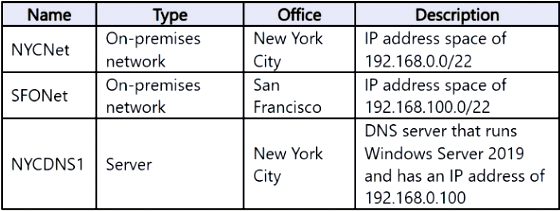
The offices contain the resources shown in the following table.
NYCNet connects to Azure by using an ExpressRoute circuit.
SFONet connects to Azure by using a Site-to-Site (S2S) VPN.
Existing Environment. Azure Resources
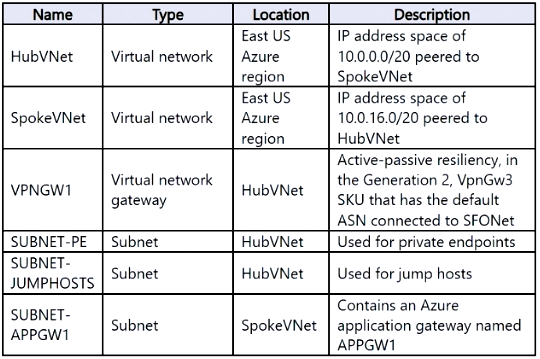
The Azure subscription contains the virtual networks and subnets shown in the following table.
The subscription contains four virtual machines named VM1, VM2, VM3, and VM4. VM1 and VM2 host an app named App1.
VM3 and VM4 host a web app named App2 that is accessed by using a FQDN of app2.proseware.com. Users access app2.proseware.com by using HTTP or HTTPS.
VM1, VM2, and VM4 are connected to SpokeVNet.
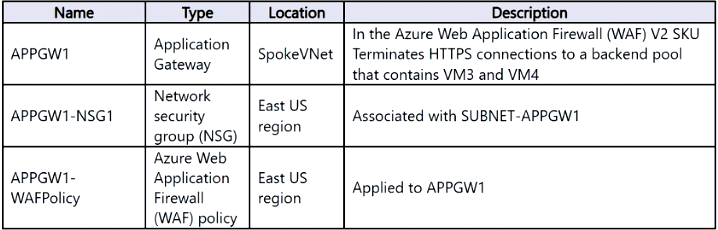
The subscription contains Application Gateway resources shown in the following table.
The subscription contains an Azure Front Door Standard profile named FD1. FD1 contains a single origin group that targets APPGW1 by using the default endpoint name.
HubVNet connects to NYCNet by using an ExpressRoute gateway named ERGW1.
Planned Changes and Requirements. Planned Changes
Proseware plans to implement the following changes:
• Deploy an Azure Private DNS Resolver named PRDNS1 to HubVNet and link PRDNS1 to SpokeVNet.
• Create a DNS forwarding ruleset named DNSRS1 and associate DNSRS1 with PRDNS1.
• Deploy Azure Virtual Network Manager and implement the following rules:
- Allow inbound connections on TCP port 3389 from the on-premises networks to SUBNET-JUMPHOSTS.
- Block inbound connections on TCP port 80 from the internet to SpokeVNet.
• Ensure that Azure Virtual Network Manager rules take precedence over conflicting NSG rules.
• Deploy two network virtual appliances (NVAs) named NVA1 and NVA2 to HubVNet.
• Deploy a gateway load balancer named LBGW1 to HubVNet.
• Configure LBGW1 to inspect traffic on TCP ports 443, 1433, and 1434 from LBS1 by using NVA1 and NVA2.
• Ensure that all the traffic to App2 is processed by using FD1.
Planned Changes and Requirements. Connectivity requirements
Proseware identifies the following connectivity requirements:
• Minimize the complexity of the Azure Virtual Network Manager deployment.
• Route traffic between NYCNet and SFONet via the ExpressRoute circuit and the S2S VPN.
• Ensure that remote users on Windows 11 devices can connect to HubVNet by using a Point-to-Site (P2S) VPN and their proseware.com credentials.
Planned Changes and Requirements. Security requirements
Proseware identifies the following security requirements:
• Whenever possible, use the internal CA.
• Ensure that all connections routed via APPGW1 use end-to-end encryption.
• Ensure that user connections to Azure-hosted apps use end-to-end encryption.
• Ensure that all inbound internet traffic to app2.proseware.com is routed via FD1.
• Prevent devices that connect to NYCNet from accessing Azure services that use private endpoints.
• Enable the virtual machines that connect to HubVNet and SpokeVNet to access Azure services that use private endpoints.
Planned Changes and Requirements. General requirements
Proseware identifies the following general requirements:
• Minimize the IP address space required to deploy platform-managed resources to the virtual networks.
• From SpokeVNet, resolve name resolution requests for the azure.proseware.com namespace and the corp.proseware.com namespace by using PRDNS1.
• Whenever possible, minimize administrative effort.
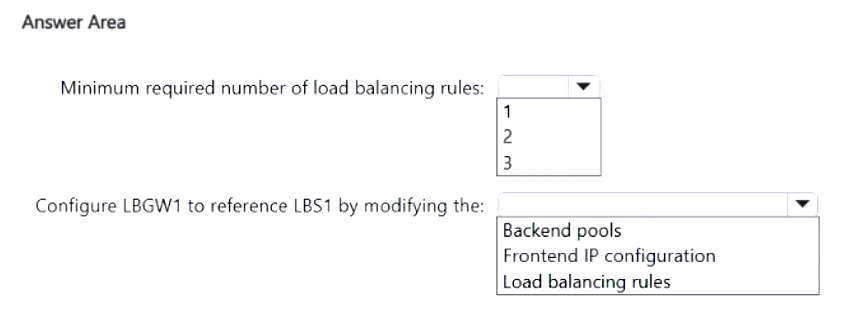
You need to plan the deployment of LBGW1. The solution must support the planned changes.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Minimum required number of load-balancing rules: 1
Configure LBGW1 to reference LBS1 by modifying the: Frontend IP configuration
Explanation: A Gateway Load Balancer uses a single HA Ports load-balancing rule to inspect multiple TCP ports. The consumer load balancer associates with the Gateway Load Balancer through its frontend IP configuration (service chaining).
Question 36
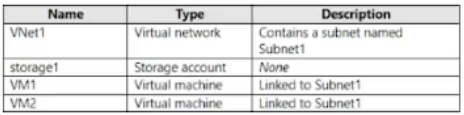
You have an Azure subscription that contains the resources shown in the following table.
You need to ensure that VM1 and VM2 can connect only to storage1. The solution must meet the following requirements:
• Prevent VM1 and VM2 from accessing any other storage accounts
• Ensure that storage1 is accessible from the internet.
What should you use?
A. a network security group (NSG)
B. a service endpoint policy
C. a private link
D. a private endpoint
Show Answer
Correct Answer: B
Explanation: Use a service endpoint policy on Subnet1 to allow access to storage1 and deny access to other Azure Storage accounts. Storage1 can remain accessible through its public endpoint, including from the internet. An NSG cannot distinguish individual storage accounts using the Storage service tag.
Question 37
HOTSPOT
-
Case Study
-
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
-
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Question button to return to the question.
Overview
-
Proseware, Inc. is a financial services company that has a main office in New York City and a branch office in San Francisco.
Existing Environment. Hybrid Environment
Proseware has an on-premises Active Directory Domain Services (AD DS) forest named corp.proseware.com that syncs with a Microsoft Entra tenant named proseware.com.
Proseware has an Azure subscription that is linked to proseware.com.
Proseware has an internal certification authority (CA).
Existing Environment. Network Infrastructure
The offices contain the resources shown in the following table.
NYCNet connects to Azure by using an ExpressRoute circuit.
SFONet connects to Azure by using a Site-to-Site (S2S) VPN.
Existing Environment. Azure Resources
The Azure subscription contains the virtual networks and subnets shown in the following table.
The subscription contains four virtual machines named VM1, VM2, VM3, and VM4. VM1 and VM2 host an app named App1.
VM3 and VM4 host a web app named App2 that is accessed by using a FQDN of app2.proseware.com. Users access app2.proseware.com by using HTTP or HTTPS.
VM1, VM2, and VM4 are connected to SpokeVNet.
The subscription contains Application Gateway resources shown in the following table.
The subscription contains an Azure Front Door Standard profile named FD1. FD1 contains a single origin group that targets APPGW1 by using the default endpoint name.
HubVNet connects to NYCNet by using an ExpressRoute gateway named ERGW1.
Planned Changes and Requirements. Planned Changes
Proseware plans to implement the following changes:
• Deploy an Azure Private DNS Resolver named PRDNS1 to HubVNet and link PRDNS1 to SpokeVNet.
• Create a DNS forwarding ruleset named DNSRS1 and associate DNSRS1 with PRDNS1.
• Deploy Azure Virtual Network Manager and implement the following rules:
- Allow inbound connections on TCP port 3389 from the on-premises networks to SUBNET-JUMPHOSTS.
- Block inbound connections on TCP port 80 from the internet to SpokeVNet.
• Ensure that Azure Virtual Network Manager rules take precedence over conflicting NSG rules.
• Deploy two network virtual appliances (NVAs) named NVA1 and NVA2 to HubVNet.
• Deploy a gateway load balancer named LBGW1 to HubVNet.
• Configure LBGW1 to inspect traffic on TCP ports 443, 1433, and 1434 from LBS1 by using NVA1 and NVA2.
• Ensure that all the traffic to App2 is processed by using FD1.
Planned Changes and Requirements. Connectivity requirements
Proseware identifies the following connectivity requirements:
• Minimize the complexity of the Azure Virtual Network Manager deployment.
• Route traffic between NYCNet and SFONet via the ExpressRoute circuit and the S2S VPN.
• Ensure that remote users on Windows 11 devices can connect to HubVNet by using a Point-to-Site (P2S) VPN and their proseware.com credentials.
Planned Changes and Requirements. Security requirements
Proseware identifies the following security requirements:
• Whenever possible, use the internal CA.
• Ensure that all connections routed via APPGW1 use end-to-end encryption.
• Ensure that user connections to Azure-hosted apps use end-to-end encryption.
• Ensure that all inbound internet traffic to app2.proseware.com is routed via FD1.
• Prevent devices that connect to NYCNet from accessing Azure services that use private endpoints.
• Enable the virtual machines that connect to HubVNet and SpokeVNet to access Azure services that use private endpoints.
Planned Changes and Requirements. General requirements
Proseware identifies the following general requirements:
• Minimize the IP address space required to deploy platform-managed resources to the virtual networks.
• From SpokeVNet, resolve name resolution requests for the azure.proseware.com namespace and the corp.proseware.com namespace by using PRDNS1.
• Whenever possible, minimize administrative effort.
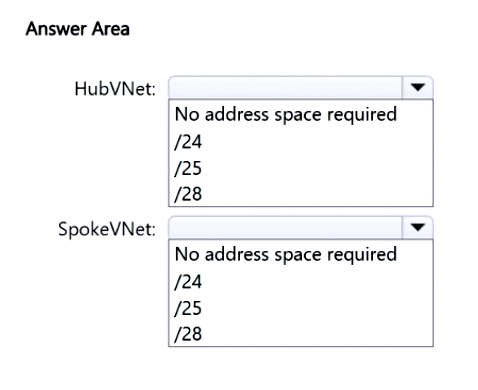
You need to identify which IP address space to allocate for the planned deployment of PRDNS1 to HubVNet and SpokeVNet. The solution must meet the general requirements.
What should you identify for each virtual network? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: HubVNet: /28
SpokeVNet: No address space required
Explanation: Azure Private DNS Resolver requires a dedicated inbound/outbound endpoint subnet in the VNet where it is deployed, with a minimum subnet size of /28. Linking the resolver/ruleset to another VNet (SpokeVNet) does not require allocating a dedicated subnet there.
Question 37
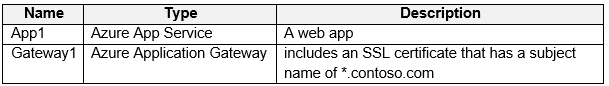
You have an Azure subscription that contains the resources shown in the following table.
Gateway1 provides access to App1 by using a URL of https://app1.contoso.com.
You create a new web app named App2.
You need to configure Gateway1 to enable access to App2 by using a URL of https://app2.contoso.com. The solution must minimize administrative effort.
What should you configure on Gateway1?
A. a backend pool and a routing rule
B. a listener and a routing rule
C. a listener, a backend pool, and a routing rule
D. a listener and a backend pool
Show Answer
Correct Answer: C
Explanation: Configure a backend pool for App2, a listener that accepts requests for app2.contoso.com, and a routing rule that sends those requests to the App2 backend pool. Gateway1’s wildcard certificate can be reused for HTTPS, but it does not by itself configure the listener or route traffic to App2.
Question 38
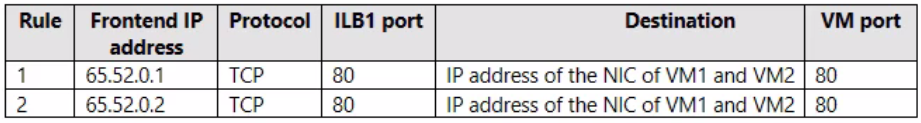
You have an internal Basic Azure Load Balancer named LB1 that has two frontend IP addresses. The backend pool of LB1 contains two Azure virtual machines named VM1 and VM2.
You need to configure the rules on LB1 as shown in the following table.
What should you do for each rule?
A. Enable Floating IP.
B. Disable Floating IP.
C. Set Session persistence to Enabled.
D. Set Session persistence to Disabled.
Show Answer
Correct Answer: A
Explanation: Enable Floating IP for both rules. Both rules use TCP port 80 and map to backend port 80 on the same VMs; Floating IP enables reuse of the same backend port across multiple frontend IP configurations.
Question 38
HOTSPOT -
Case Study -
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study -
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Question button to return to the question.
Overview -
Proseware, Inc. is a financial services company that has a main office in New York City and a branch office in San Francisco.
Existing Environment. Hybrid Environment
Proseware has an on-premises Active Directory Domain Services (AD DS) forest named corp.proseware.com that syncs with a Microsoft Entra tenant named proseware.com.
Proseware has an Azure subscription that is linked to proseware.com.
Proseware has an internal certification authority (CA).
Existing Environment. Network Infrastructure
The offices contain the resources shown in the following table.
NYCNet connects to Azure by using an ExpressRoute circuit.
SFONet connects to Azure by using a Site-to-Site (S2S) VPN.
Existing Environment. Azure Resources
The Azure subscription contains the virtual networks and subnets shown in the following table.
The subscription contains four virtual machines named VM1, VM2, VM3, and VM4. VM1 and VM2 host an app named App1.
VM3 and VM4 host a web app named App2 that is accessed by using a FQDN of app2.proseware.com. Users access app2.proseware.com by using HTTP or HTTPS.
VM1, VM2, and VM4 are connected to SpokeVNet.
The subscription contains Application Gateway resources shown in the following table.
The subscription contains an Azure Front Door Standard profile named FD1. FD1 contains a single origin group that targets APPGW1 by using the default endpoint name.
HubVNet connects to NYCNet by using an ExpressRoute gateway named ERGW1.
Planned Changes and Requirements. Planned Changes
Proseware plans to implement the following changes:
• Deploy an Azure Private DNS Resolver named PRDNS1 to HubVNet and link PRDNS1 to SpokeVNet.
• Create a DNS forwarding ruleset named DNSRS1 and associate DNSRS1 with PRDNS1.
• Deploy Azure Virtual Network Manager and implement the following rules:
- Allow inbound connections on TCP port 3389 from the on-premises networks to SUBNET-JUMPHOSTS.
- Block inbound connections on TCP port 80 from the internet to SpokeVNet.
• Ensure that Azure Virtual Network Manager rules take precedence over conflicting NSG rules.
• Deploy two network virtual appliances (NVAs) named NVA1 and NVA2 to HubVNet.
• Deploy a gateway load balancer named LBGW1 to HubVNet.
• Configure LBGW1 to inspect traffic on TCP ports 443, 1433, and 1434 from LBS1 by using NVA1 and NVA2.
• Ensure that all the traffic to App2 is processed by using FD1.
Planned Changes and Requirements. Connectivity requirements
Proseware identifies the following connectivity requirements:
• Minimize the complexity of the Azure Virtual Network Manager deployment.
• Route traffic between NYCNet and SFONet via the ExpressRoute circuit and the S2S VPN.
• Ensure that remote users on Windows 11 devices can connect to HubVNet by using a Point-to-Site (P2S) VPN and their proseware.com credentials.
Planned Changes and Requirements. Security requirements
Proseware identifies the following security requirements:
• Whenever possible, use the internal CA.
• Ensure that all connections routed via APPGW1 use end-to-end encryption.
• Ensure that user connections to Azure-hosted apps use end-to-end encryption.
• Ensure that all inbound internet traffic to app2.proseware.com is routed via FD1.
• Prevent devices that connect to NYCNet from accessing Azure services that use private endpoints.
• Enable the virtual machines that connect to HubVNet and SpokeVNet to access Azure services that use private endpoints.
Planned Changes and Requirements. General requirements
Proseware identifies the following general requirements:
• Minimize the IP address space required to deploy platform-managed resources to the virtual networks.
• From SpokeVNet, resolve name resolution requests for the azure.proseware.com namespace and the corp.proseware.com namespace by using PRDNS1.
• Whenever possible, minimize administrative effort.
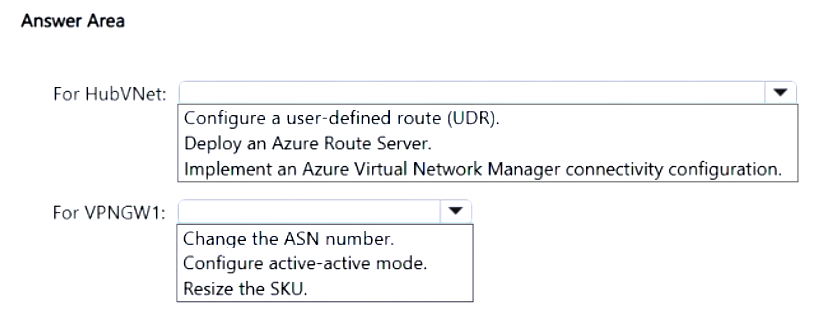
You need to configure connectivity between NYCNet and SFONet. The solution must meet the connectivity requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: For HubVNet: Deploy an Azure Route Server.
For VPNGW1: Configure active-active mode.
Explanation: Transit routing between ExpressRoute and an S2S VPN requires Azure Route Server with the VPN gateway in active-active mode to exchange routes. UDRs or Virtual Network Manager connectivity do not provide this ExpressRoute-to-VPN transit capability.
Question 39
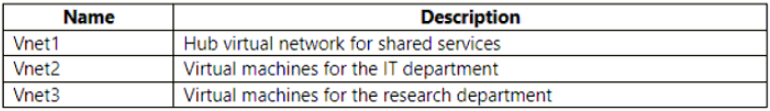
You are planning an Azure deployment that will contain three virtual networks in the East US Azure region as shown in the following table.
A Site-to-Site VPN will connect Vnet1 to your company’s on-premises network.
You need to recommend a solution that ensures that the virtual machines on all the virtual networks can communicate with the on-premises network. The solution must minimize costs.
What should you recommend for Vnet2 and Vnet3?
A. VNet-to-VNet VPN connections
B. peering
C. service endpoints
D. route tables
Show Answer
Correct Answer: B
Explanation: Use VNet peering between Vnet1 and each of Vnet2 and Vnet3. Configure Vnet1 to allow gateway transit, and configure the peered VNets to use Vnet1’s remote gateway. This lets their VMs reach the on-premises network through Vnet1’s existing Site-to-Site VPN, avoiding separate VPN gateways and connections for each VNet.
$19
Get all 347 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.