You have a Microsoft 365 subscription that contains a user named User1.
You need to ensure that User1 can gather and summarize a custom set of data from signals in the Microsoft Defender XDR environment. The solution must NOT require that User1 have KQL knowledge.
What should you do in Microsoft Defender XDR?
A. From Advanced hunting, create a new query in the query editor.
B. From Cloud Discovery, create a report.
C. From API Explorer, create a query.
D. From Advanced hunting, create a new query in the query builder.
Show Answer
Correct Answer: D
Explanation: Advanced hunting includes a guided query builder mode that allows users to gather and summarize custom data from Microsoft Defender XDR signals without writing KQL. The query editor is intended for KQL-based advanced hunting, while Cloud Discovery reports and API Explorer do not satisfy the requirement for custom hunting without KQL knowledge.
Question 14
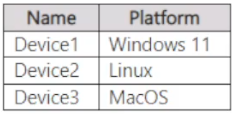
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.
You plan to create an Endpoint security policy by using the Defender Update controls template.
To which devices can you apply the policy?
A. Device1 only
B. Device1 and Device2 only
C. Device1 and Device3 only
D. Device1, Device2, and Device3
Show Answer
Correct Answer: A
Explanation: The Defender Update controls template applies to Windows devices. Device1 runs Windows 11; Device2 runs Linux and Device3 runs macOS, so only Device1 is eligible.
Question 14
Overview -
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment -
Active Directory Environment -
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of
.
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure -
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements -
Planned Changes -
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
• Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
• Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements -
Fabrikam identifies the following technical requirements:
• All users must be able to exchange email messages successfully during Project1 by using their current email address.
• Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
• A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
• Microsoft 365 Apps for enterprise applications must be installed from a network share only.
• Disruptions to email access must be minimized.
Application Requirements -
Fabrikam identifies the following application requirements:
• An on-premises web application named App1 must allow users to complete their expense reports online. App1 must be available to users from the My Apps portal.
• The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements -
Fabrikam identifies the following security requirements:
• After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
• The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
• After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
• The principle of least privilege must be used.
You are evaluating the required processes for Project1.
You need to recommend which DNS record must be created while adding a domain name to the tenant for the project.
Which DNS record should you recommend?
A. name server (NS)
B. host (A)
C. mail exchanger (MX)
D. host information (HINFO)
Show Answer
Correct Answer: C
Explanation: For an Exchange hybrid migration (moving a pilot group of mailboxes to Microsoft 365 while keeping mail flow working), the Microsoft 365 tenant domain setup requires creating DNS records. Among the provided options, the required record is the MX record, which is used for mail routing. TXT is commonly used for domain verification, but it is not an available option. NS, A, and HINFO are not the appropriate choice for this requirement.
Question 15
You have a Microsoft 365 tenant.
You plan to manage incidents in the tenant by using the Microsoft Defender XDR.
Which Microsoft service source will appear on the Incidents page of the Microsoft Defender portal?
A. Azure Web Application Firewall
B. Microsoft Sentinel
C. Microsoft Defender for Cloud Apps
D. Microsoft Purview
Show Answer
Correct Answer: C
Explanation: The Microsoft Defender XDR Incidents page aggregates incidents from integrated Microsoft security products, including Microsoft Defender for Cloud Apps. Azure Web Application Firewall and Microsoft Purview are not incident sources in Defender XDR, and Microsoft Sentinel is a separate SIEM that can consume Defender incidents rather than appearing as a Defender XDR incident source.
Question 15
Overview -
Litware, Inc. is a consulting company that has a main office in Montreal and a branch office in Seattle.
Litware collaborates with a third-party company named A. Datum Corporation.
Environment -
On-Premises Environment -
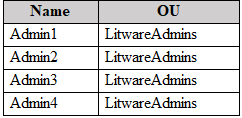
The network of Litware contains an Active Directory domain named litware.com. The domain contains three organizational units (OUs) named LitwareAdmins, Montreal Users, and Seattle Users and the users shown in the following table.
The domain contains 2,000 Windows 10 Pro devices and 100 servers that run Windows Server 2019.
Cloud Environment -
Litware has a pilot Microsoft 365 subscription that includes Microsoft Office 365 Enterprise E3 licenses and Azure AD Premium P2 licenses.
The subscription contains a verified DNS domain named litware.com.
Azure AD Connect is installed and has the following configurations:
• Password hash synchronization is enabled.
• Synchronization is enabled for the LitwareAdmins OU only.
Users are assigned the roles shown in the following table.
Self-service password reset (SSPR) is enabled.
The Azure AD tenant has Security defaults enabled.
Problem Statements -
Litware identifies the following issues:
• Admin1 cannot create conditional access policies.
• Admin4 receives an error when attempting to use SSPR.
• Users access new Office 365 service and feature updates before the updates are reviewed by Admin2.
Requirements -
Planned Changes -
Litware plans to implement the following changes:
• Implement Microsoft Intune.
• Implement Microsoft Teams.
• Implement Microsoft Defender for Office 365.
• Ensure that users can install Office 365 apps on their device.
• Convert all the Windows 10 Pro devices to Windows 10 Enterprise ES.
• Configure Azure AD Connect to sync the Montreal Users OU and the Seattle Users OU.
Technical Requirements -
Litware identifies the following technical requirements:
• Administrators must be able to specify which version of an Office 365 desktop app will be available to users and to roll back to previous versions.
• Only Admin2 must have access to new Office 365 service and feature updates before they are released to the company.
• Litware users must be able to invite A. Datum users to participate in the following activities:
• Join Microsoft Teams channels.
• Join Microsoft Teams chats.
• Access shared files.
• Just in time access to critical administrative roles must be required.
• Microsoft 365 incidents and advisories must be reviewed monthly.
• Office 365 service status notifications must be sent to Admin2.
• The principle of least privilege must be used.
You need to configure just in time access to meet the technical requirements.
What should you use?
A. entitlement management
B. Azure AD Privileged Identity Management (PIM)
C. access reviews
D. Azure AD Identity Protection
Show Answer
Correct Answer: B
Explanation: Use Azure AD Privileged Identity Management (PIM) to provide just-in-time, time-limited activation of privileged administrative roles, supporting least privilege.
Question 16
You have a Microsoft 365 subscription.
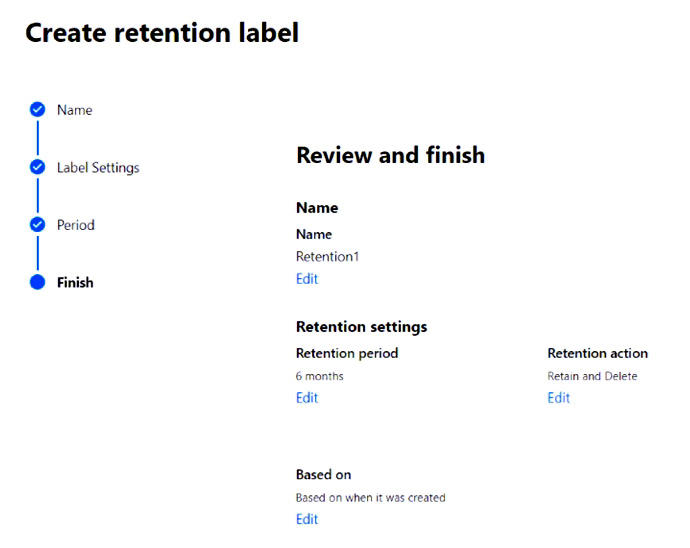
You create a retention label named Retention1 as shown in the following exhibit.
You apply Retention1 to all the Microsoft OneDrive content.
On January 1, 2020, a user stores a file named File1 in OneDrive.
On January 10, 2020, the user modifies File1.
On February 1, 2020, the user deletes File1.
When will File1 be removed permanently and unrecoverable from OneDrive?
A. February 1, 2020
B. July 1, 2020
C. July 10, 2020
D. August 1, 2020
Show Answer
Correct Answer: B
Explanation: Retention1 retains the file for six months based on its creation date, January 1, 2020, and then deletes it. Deleting the file on February 1 does not bypass the retention period, so it becomes permanently unrecoverable on July 1, 2020.
Question 16
You have a Microsoft 365 subscription that contains a Microsoft Entra tenant named contoso.com. The tenant includes a user named User1.
You plan to use Microsoft Entra ID Protection.
You need to ensure that User1 can review the list in Microsoft Entra ID Protection of users flagged for risk. The solution must use the principle of least privilege.
To which role should you add User1?
A. Compliance Administrator
B. User Administrator
C. Security Administrator
D. Global Administrator
Show Answer
Correct Answer: C
Explanation: The Security Administrator role can access and manage Microsoft Entra ID Protection, including reviewing risky users. Global Administrator also has access but grants broader permissions than necessary, violating least privilege. User Administrator and Compliance Administrator do not have the required Identity Protection access.
Question 17
You have a Microsoft 365 E5 tenant.
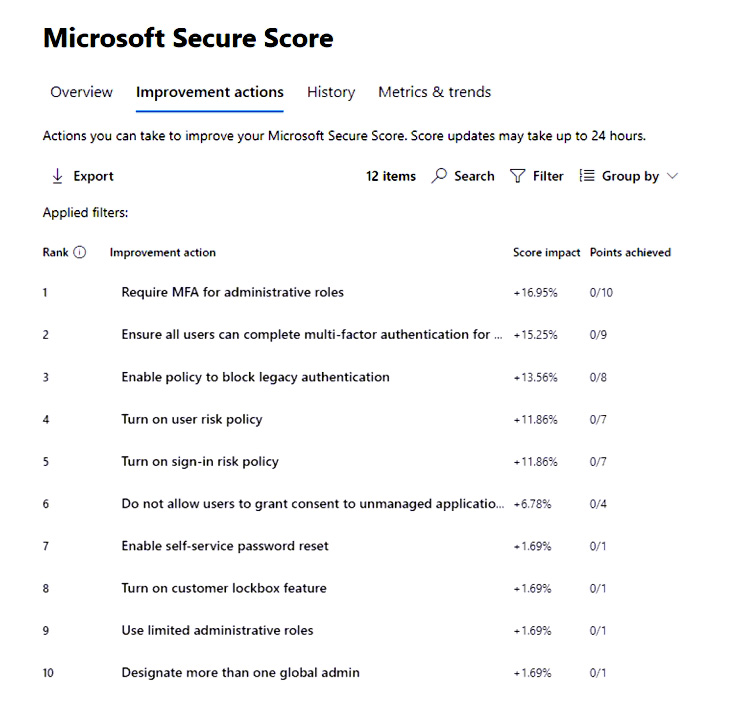
The Microsoft Secure Score for the tenant is shown in the following exhibit.
You plan to enable Security defaults for Azure AD.
Which three improvement actions will this affect?
NOTE: Each correct selection is worth one point.
A. Require MFA for administrative roles
B. Ensure all users can complete multi-factor authentication for secure access
C. Enable policy to block legacy authentication
D. Enable self-service password reset
E. Use limited administrative roles
Show Answer
Correct Answer: A, B, C
Explanation: Security defaults require MFA for administrative roles, ensure users can register and use MFA, and block legacy authentication. They do not enable self-service password reset or limit administrative roles.
Question 17
Your network contains an Active Directory domain named adatum.com that is synced to a Microsoft Entra tenant.
The domain contains 100 user accounts.
The city attribute for all the users is set to the city where the user resides.
You need to modify the value of the city attribute to the three-letter airport code of each city.
What should you do?
A. From Azure Cloud Shell, run the Get-ADUser and Set-ADUser cmdlets.
B. From Azure Cloud Shell, run the Get-MsolUser and Set-Msoluser cmdlets.
C. From Windows PowerShell on a domain controller, run the Get-MgUser and Update-MgUser cmdlets.
D. From Active Directory Administrative Center, select the Active Directory users, and then modify the Properties settings.
Show Answer
Correct Answer: D
Explanation: Because the users are synchronized from on-premises Active Directory, the city attribute is authoritative on-premises and must be changed there. Azure Cloud Shell cannot run the on-premises Active Directory cmdlets, MSOnline cmdlets cannot modify synchronized attributes, and Microsoft Graph cannot update on-premises mastered synchronized attributes. Active Directory Administrative Center allows bulk editing of the on-premises user properties.
Question 18
You have a Microsoft 365 tenant -
You plan to manage incidents in the tenant by using the Microsoft Defender XDR.
Which Microsoft service source will appear on the Incidents page of the Microsoft Defender portal?
A. Azure Information Protection
B. Microsoft Defender for Identity
C. Azure Web Application Firewall
D. Microsoft Sentinel
Show Answer
Correct Answer: B
Explanation: The Microsoft Defender portal (Microsoft Defender XDR) aggregates incidents from integrated Defender products, including Microsoft Defender for Identity. Azure Information Protection and Azure Web Application Firewall are not incident sources on the Defender XDR Incidents page, and Microsoft Sentinel is a separate SIEM that can integrate with Defender rather than appearing as a Defender XDR service source.
$19
Get all 431 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.