This is the free Microsoft AZ-104 practice question bank —
280 of 558 total questions, each with a full explanation, free to
read with no signup required. Updated 2026-10-13.
Every answer is verified against official Microsoft documentation —
see our methodology.
Question 1
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure virtual machine named VM1. VM1 was deployed by using a custom Azure Resource Manager template named ARM1.json.
You receive a notification that VM1 will be affected by maintenance.
You need to move VM1 to a different host immediately.
Solution: From the VM1 Updates blade, select One-time update.
Does this meet the goal?
A. Yes
B. No
Show Answer
Correct Answer: B
Explanation: Selecting 'One-time update' from the VM Updates blade initiates installation of available updates, not migration to a different physical host. To immediately move a VM to a new Azure host in response to planned maintenance, you use the Redeploy operation, which moves the VM to a new node while preserving its configuration. Therefore, the proposed solution does not meet the goal.
Question 1
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure container registry named Registry1 that contains an image named image1.
You receive an error message when you attempt to deploy a container instance by using image1.
You need to be able to deploy a container instance by using image1.
Solution: You create a private endpoint connection for Registry1.
Does this meet the goal?
A. Yes
B. No
Show Answer
Correct Answer: B
Explanation: No. Creating a private endpoint provides private network access to Registry1, but it does not by itself configure the authentication needed for Azure Container Instances to pull image1. The registry credentials or another supported authentication method must also be configured.
Question 1
Your on-premises network contains a VPN gateway.
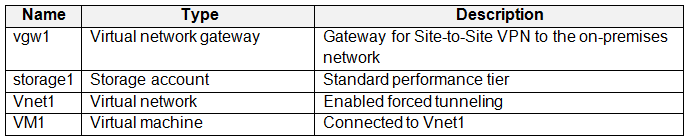
You have an Azure subscription that contains the resources shown in the following table.
You need to ensure that all the traffic from VM1 to storage1 travels across the Microsoft backbone network.
What should you configure?
A. a network security group (NSG)
B. private endpoints
C. Microsoft Entra Application Proxy
D. Azure Virtual WAN
Show Answer
Correct Answer: B
Explanation: Configure a private endpoint for the storage account. It gives storage1 a private IP address in VNet1, so VM1’s traffic to it uses the Microsoft backbone rather than being sent through the VPN gateway by forced tunneling.
Question 1
You have an Azure subscription that contains the storage accounts shown in the following table.
Which storage account can be converted to zone-redundant storage (ZRS) replication?
A. storage1 only
B. storage2 only
C. storage3 only
D. storage2 and storage3
E. storage1, storage2, and storage3
Show Answer
Correct Answer: A
Explanation: Storage1 is a standard general-purpose v2 account using LRS, which can be migrated directly to ZRS. Storage2 uses RA-GRS and cannot be changed directly to ZRS; it would need an intermediate change to LRS. Storage3’s premium BlobStorage account type isn’t eligible for this ZRS migration.
Question 2
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure virtual machine named VM1. VM1 was deployed by using a custom Azure Resource Manager template named ARM1.json.
You receive a notification that VM1 will be affected by maintenance.
You need to move VM1 to a different host immediately.
Solution: From the VM1 Redeploy + reapply blade, you select Redeploy.
Does this meet the goal?
A. Yes
B. No
Show Answer
Correct Answer: A
Explanation: Selecting Redeploy from the VM's 'Redeploy + reapply' blade deallocates the VM, moves it to a new Azure host (node), and starts it again while preserving its managed disks and configuration. This is the correct action to immediately move the VM to different underlying hardware in response to planned maintenance.
Question 2
Case study -
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study -
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview -
ADatum Corporation is consulting firm that has a main office in Montreal and branch offices in Seattle and New York.
Existing Environment -
Azure Environment -
ADatum has an Azure subscription that contains three resource groups named RG1, RG2, and RG3.
The subscription contains the storage accounts shown in the following table.
The subscription contains the virtual machines shown in the following table.
The subscription has an Azure container registry that contains the images shown in the following table.
The subscription contains the resources shown in the following table.
Azure Key Vault -
The subscription contains an Azure key vault named Vault1.
Vault1 contains the certificates shown in the following table.
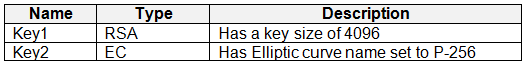
Vault1 contains the keys shown in the following table.
Microsoft Entra Environment -
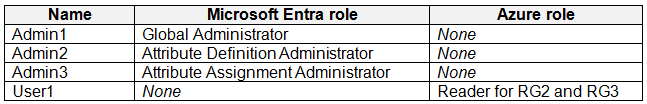
ADatum has a Microsoft Entra tenant named adatum.com that is linked to the Azure subscription and contains the users shown in the following table.
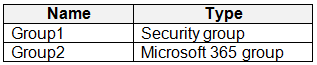
The tenant contains the groups shown in the following table.
The adatum.com tenant has a custom security attribute named Attribute1.
Planned Changes -
ADatum plans to implement the following changes:
• Configure a data collection rule (DCR) named DCR1 to collect only system events that have an event ID of 4648 from VM2 and VM4.
• In storage1, create a new container named cont2 that has the following access policies: o Three stored access policies named Stored1, Stored2, and Stored3 o A legal hold for immutable blob storage
• Whenever possible, use directories to organize storage account content.
• Grant User1 the permissions required to link Zone1 to VNet1.
• Assign Attribute1 to supported adatum.com resources.
• In storage2, create an encryption scope named Scope1.
• Deploy new containers by using Image1 or Image2.
Technical Requirements -
ADatum must meet the following technical requirements:
• Use TLS for WebApp1.
• Follow the principle of least privilege.
• Grant permissions at the required scope only.
• Ensure that Scope1 is used to encrypt storage services.
• Use Azure Backup to back up cont1 and share1 as frequently as possible.
• Whenever possible, use Azure Disk Encryption and a key encryption key (KEK) to encrypt the virtual machines.
You need to configure encryption for the virtual machines. The solution must meet the technical requirements.
Which virtual machines can you encrypt?
A. VM1 and VM3
B. VM4 and VM5
C. VM2 and VM3
D. VM2 and VM4
Show Answer
Correct Answer: C
Explanation: Azure Disk Encryption with a key encryption key can be used for VM2 and VM3. VM1 uses ephemeral OS disks, which ADE does not support; VM4 uses Write Accelerator disks, which are incompatible with ADE; and VM5 has a dynamic volume, which ADE does not support. A basic volume on VM2 is not the same as a basic-tier VM and does not disqualify it.
Question 2
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that contains the virtual machines shown in the following table.
You deploy a load balancer that has the following configurations:
✑ Name: LB1
✑ Type: Internal
✑ SKU: Standard
✑ Virtual network: VNET1
You need to ensure that you can add VM1 and VM2 to the backend pool of LB1.
Solution: You create two Standard SKU public IP addresses and associate a Standard SKU public IP address to the network interface of each virtual machine.
Does this meet the goal?
A. Yes
B. No
Show Answer
Correct Answer: A
Explanation: Yes. Both VMs are in VNET1, and assigning them Standard SKU public IP addresses makes their IP SKU compatible with the Standard Load Balancer. A VM can be added to the backend pool while stopped; it does not need to be running.
Question 3
Case study -
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study -
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview -
ADatum Corporation is consulting firm that has a main office in Montreal and branch offices in Seattle and New York.
Existing Environment -
Azure Environment -
ADatum has an Azure subscription that contains three resource groups named RG1, RG2, and RG3.
The subscription contains the storage accounts shown in the following table.
The subscription contains the virtual machines shown in the following table.
The subscription has an Azure container registry that contains the images shown in the following table.
The subscription contains the resources shown in the following table.
Azure Key Vault -
The subscription contains an Azure key vault named Vault1.
Vault1 contains the certificates shown in the following table.
Vault1 contains the keys shown in the following table.
Microsoft Entra Environment -
ADatum has a Microsoft Entra tenant named adatum.com that is linked to the Azure subscription and contains the users shown in the following table.
The tenant contains the groups shown in the following table.
The adatum.com tenant has a custom security attribute named Attribute1.
Planned Changes -
ADatum plans to implement the following changes:
• Configure a data collection rule (DCR) named DCR1 to collect only system events that have an event ID of 4648 from VM2 and VM4.
• In storage1, create a new container named cont2 that has the following access policies: o Three stored access policies named Stored1, Stored2, and Stored3 o A legal hold for immutable blob storage
• Whenever possible, use directories to organize storage account content.
• Grant User1 the permissions required to link Zone1 to VNet1.
• Assign Attribute1 to supported adatum.com resources.
• In storage2, create an encryption scope named Scope1.
• Deploy new containers by using Image1 or Image2.
Technical Requirements -
ADatum must meet the following technical requirements:
• Use TLS for WebApp1.
• Follow the principle of least privilege.
• Grant permissions at the required scope only.
• Ensure that Scope1 is used to encrypt storage services.
• Use Azure Backup to back up cont1 and share1 as frequently as possible.
• Whenever possible, use Azure Disk Encryption and a key encryption key (KEK) to encrypt the virtual machines.
You need to implement the planned changes for the storage account content.
Which containers and file shares can you use to organize the content?
A. share1 only
B. cont1 and share1 only
C. share1 and share2 only
D. cont1, share1, and share2 only
E. cont1, cont2, share1, and share2
Show Answer
Correct Answer: D
Explanation: cont1 supports directories because it is in storage1, which has hierarchical namespace enabled. Azure Files shares support directories regardless of the account’s hierarchical namespace setting, so both share1 and share2 qualify. cont2 is a blob container in a non-HNS account; its apparent folders are only name prefixes, not actual directories.
Question 4
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure container registry named Registry1 that contains an image named image1.
You receive an error message when you attempt to deploy a container instance by using image1.
You need to be able to deploy a container instance by using image1.
Solution: You select Use dedicated data endpoint for Registry1.
Does this meet the goal?
A. Yes
B. No
Show Answer
Correct Answer: B
Explanation: Selecting 'Use dedicated data endpoint' configures a dedicated endpoint for data-plane operations but does not resolve the typical causes of Azure Container Instances failing to pull images from Azure Container Registry, such as authentication, permissions, or network/firewall access. Therefore, this change alone does not meet the goal.
Question 4
Case study -
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study -
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview -
ADatum Corporation is consulting firm that has a main office in Montreal and branch offices in Seattle and New York.
Existing Environment -
Azure Environment -
ADatum has an Azure subscription that contains three resource groups named RG1, RG2, and RG3.
The subscription contains the storage accounts shown in the following table.
The subscription contains the virtual machines shown in the following table.
The subscription has an Azure container registry that contains the images shown in the following table.
The subscription contains the resources shown in the following table.
Azure Key Vault -
The subscription contains an Azure key vault named Vault1.
Vault1 contains the certificates shown in the following table.
Vault1 contains the keys shown in the following table.
Microsoft Entra Environment -
ADatum has a Microsoft Entra tenant named adatum.com that is linked to the Azure subscription and contains the users shown in the following table.
The tenant contains the groups shown in the following table.
The adatum.com tenant has a custom security attribute named Attribute1.
Planned Changes -
ADatum plans to implement the following changes:
• Configure a data collection rule (DCR) named DCR1 to collect only system events that have an event ID of 4648 from VM2 and VM4.
• In storage1, create a new container named cont2 that has the following access policies: o Three stored access policies named Stored1, Stored2, and Stored3 o A legal hold for immutable blob storage
• Whenever possible, use directories to organize storage account content.
• Grant User1 the permissions required to link Zone1 to VNet1.
• Assign Attribute1 to supported adatum.com resources.
• In storage2, create an encryption scope named Scope1.
• Deploy new containers by using Image1 or Image2.
Technical Requirements -
ADatum must meet the following technical requirements:
• Use TLS for WebApp1.
• Follow the principle of least privilege.
• Grant permissions at the required scope only.
• Ensure that Scope1 is used to encrypt storage services.
• Use Azure Backup to back up cont1 and share1 as frequently as possible.
• Whenever possible, use Azure Disk Encryption and a key encryption key (KEK) to encrypt the virtual machines.
You need to configure WebApp1 to meet the technical requirements.
Which certificate can you use from Vault1?
A. Cert1 only
B. Cert1 or Cert2 only
C. Cert1 or Cert3 only
D. Cert3 or Cert4 only
E. Cert1, Cert2 Cert3, or Cert4
Show Answer
Correct Answer: B
Explanation: Use Cert1 or Cert2. Azure App Service requires a certificate with a private key in PKCS#12 (PFX) format for TLS. Both certificates are PKCS#12 and use acceptable RSA key sizes; Cert3 and Cert4 are PEM format.
$19
Get all 558 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.