You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You configure Microsoft Entra Internet Access.
Which users can manage Microsoft Entra Internet Access?
A. User1 only
B. User2 only
C. User3 only
D. User1 and User2 only
E. User1, User2, and User3
Show Answer
Correct Answer: D
Explanation: User1, as a Global Administrator, can manage Microsoft Entra Internet Access. User2 has the Global Secure Access Administrator role, which can manage it as well. User3’s Privileged Role Administrator role does not include those management permissions.
Question 9
You have a Microsoft Entra tenant.
You need to use Microsoft Entra workbooks to monitor identity activity.
To what should you set Destination details in the Diagnostic settings?
A. Archive to a storage account
B. Send to partner solution
C. Stream to an event hub
D. Send to Log Analytics workspace
Show Answer
Correct Answer: D
Explanation: Microsoft Entra workbooks visualize identity data by querying logs stored in an Azure Log Analytics workspace using Kusto Query Language (KQL). Therefore, Microsoft Entra diagnostic settings must be configured to send the relevant logs (such as sign-in and audit logs) to a Log Analytics workspace.
Question 9
HOTSPOT
-
You have a Microsoft Entra tenant that contains the users shown in the following table.
The tenant contains the administrative units shown in the following table.
The tenant contains the groups shown in the following table.
You perform the following actions:
• Assign User1 the User Administrator role for AU2.
• Assign User3 the Groups Administrator role for AU1.
• Assign User5 the Authentication Administrator role for AU3.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Yes
No
No
Explanation: User1 can reset User3’s password because User3 is in AU2. User3’s Groups Administrator role is limited to AU1, so it does not cover Group2 in AU2. User5’s Authentication Administrator role does not grant permission to configure authentication method policies.
Question 10
You have 2,500 users who are assigned Microsoft 365 E3 licenses. The licenses are assigned to individual users.
You assign Microsoft 365 E5 licenses to a group that includes all users.
You need to remove the Microsoft 365 E3 licenses from the users by using the least amount of administrative effort.
What should you use?
A. the Update-MgGroup cmdlet
B. the Set-WindowsProductKey cmdlet
C. the Set-MgUserLicense cmdlet
D. the Licenses blade in the Microsoft Entra admin center
Show Answer
Correct Answer: C
Explanation: Set-MgUserLicense is the Microsoft Graph PowerShell cmdlet used to add or remove licenses from users. Since the existing Microsoft 365 E3 licenses were assigned directly to individual users, moving to a group-based E5 assignment does not automatically remove the direct E3 assignments. The appropriate way to remove those direct licenses in bulk via PowerShell is Set-MgUserLicense. Update-MgGroup does not manage license removal from users, Set-WindowsProductKey is unrelated, and the Entra admin center does not provide the required bulk removal workflow for individually assigned licenses.
Question 10
HOTSPOT
Your network contains an on-premises Active Directory Domain Services (AD DS) domain. The domain contains 500 Windows 11 devices.
You have a Microsoft 365 subscription that syncs with the domain.
You create a Conditional Access policy named Policy1.
You need to meet the following requirements:
• Apply Policy1 to all the Windows devices.
• Assess the compliance of the Windows devices with Policy1.
What should you do for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Apply Policy1: Microsoft Entra hybrid join the devices to the subscription.
Assess compliance: Enroll the devices in Microsoft Intune.
Explanation: Hybrid join connects the existing AD DS–joined devices to Microsoft Entra ID so Conditional Access can identify them. Intune evaluates and reports device compliance.
Question 11
You have a Microsoft Entra tenant that contains the users shown in the following table.
You add an enterprise application named App1 and configure the following Self-service settings:
• Allow users to request access to this application: Yes
• To which group should assigned users be added: Group1
• Require approval before granting access to this application: Yes
• Who is allowed to approve access to this application: User2
Which users can request access to App1?
A. User3 only
B. User2 and User3 only
C. User1 and User3 only
D. User1, User2, and User3
Show Answer
Correct Answer: B
Explanation: User1 is already in Group1, the group used to grant access to App1, so User1 does not need to request access. User2 and User3 are not in Group1 and can request access. Being the designated approver does not itself give User2 access.
Sources:
https://learn.microsoft.com/en-us/entra/identity/enterprise-apps/manage-self-service-access
Question 11
You have a Microsoft Entra tenant.
You need to ensure that users are prevented from consenting to high-privilege permission requests for enterprise applications. The solution must ensure that the users can consent to low-risk permission requests.
What should you modify first?
A. Admin consent settings
B. Permission classifications
C. User consent settings
D. App registrations
Show Answer
Correct Answer: B
Explanation: First classify the permissions users may safely consent to as low impact. Then configure user consent settings to allow consent only for selected (low-impact) permissions; high-privilege permissions will require admin consent.
Question 12
You have a Microsoft 365 tenant that uses the domain name fabrikam.com.
The External collaboration settings are configured as shown in the Collaboration exhibit. (Click the Collaboration tab.)
The Email one-time passcode for guests setting is enabled for the tenant.
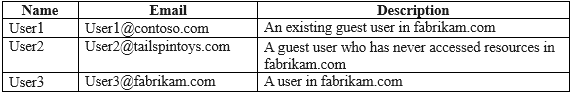
A user named
shares a Microsoft SharePoint Online document library to the users shown in the following table.
Which users will be emailed a passcode?
A. User1 only
B. User2 only
C. User1 and User2 only
D. User1, User2, and User3
Show Answer
Correct Answer: B
Explanation: User2 is the guest who has not yet accessed resources in the tenant, so their first redemption/sign-in can use email one-time passcode authentication. User1 is already an existing guest and is not affected by enabling the setting for future redemptions; User3 is an internal user, not a guest.
Question 12
You have a Microsoft Entra tenant.
You create an enterprise application collection named HR Apps that has the following settings:
• Applications: App1, App2, App3
• Owners: Admin1
• Users and groups: HRUsers
All three apps have the following Properties settings:
• Enabled for users to sign in: Yes
• User assignment required: Yes
• Visible to users: Yes
Users report that they only see App1 and App2 in the My Apps portal.
You need to ensure that the users can also see App3.
What should you do from App3?
A. From Single sign-on, configure a sign-on method.
B. From Permissions, review the User consent permissions.
C. From Users and groups, add HRUsers.
D. From Properties, change User assignment required to No.
Show Answer
Correct Answer: C
Explanation: Enterprise application collections do not automatically grant app assignment. Because App3 has 'User assignment required' set to Yes, the HRUsers group must also be assigned directly to App3 under Users and groups for it to appear in My Apps. Configuring SSO or reviewing permissions does not affect My Apps visibility, and disabling user assignment is unnecessary.
Question 13
You have a Microsoft Entra tenant that contains the groups shown in the following table.
You need to implement Privileged Identity Management (PIM) for the groups.
Which groups can be managed by using PIM?
A. Group1 only
B. Group1 and Group2 only
C. Group1 and Group3 only
D. Group3 and Group4 only
E. Group1, Group2, Group3, and Group4
Show Answer
Correct Answer: C
Explanation: PIM can manage assigned-membership security groups and Microsoft 365 groups. Dynamic-membership groups cannot be managed with PIM. Therefore, Group1 and Group3 qualify; Group2 and Group4 do not.
$19
Get all 410 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.