HOTSPOT
-
Your company has offices in New York City and London. The London office contains an on-premises app named App1.
You have a Microsoft Entra tenant named contoso.com that is hosted in North America.
You plan to manage access to App1 for the users in the London office by using Microsoft Entra Private Access. You will deploy Private Access by performing the following actions in the London office:
• Deploy Microsoft Entra application proxy connectors.
• Provision an ExpressRoute circuit to the closest peering location.
You need to optimize the network for the planned deployment. The solution must meet the following requirements:
• Maximize redundancy for connectivity to App1.
• Minimize network latency when accessing App1.
• Maximize security.
• Minimize costs.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
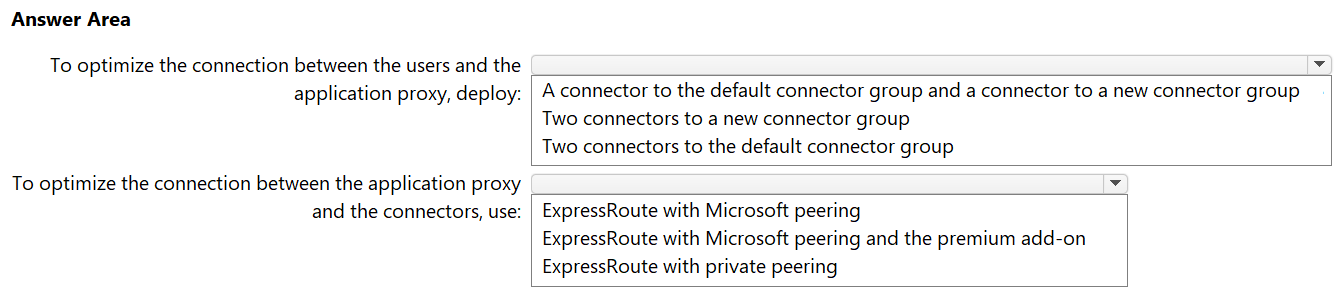
Correct Answer: Two connectors to a new connector group
ExpressRoute with Microsoft peering
Explanation: Deploy two connectors in the same dedicated connector group for redundancy and load balancing for App1. Microsoft Entra Private Access/Application Proxy traffic to Microsoft services uses ExpressRoute Microsoft peering; the premium add-on is unnecessary here and private peering is for Azure VNets, not Microsoft SaaS endpoints.
Question 18
HOTSPOT
-
You have a Microsoft 365 subscription.
Microsoft Purview is configured to protect data in only Microsoft Exchange Online and SharePoint Online. Custom sensitive information types (SITs) have been created to identify confidential data.
You discover that users access third-party generative AI websites from their Windows devices. You need to recommend a solution to block AI prompts that contain confidential data and scan the AI prompts submitted to the third-party websites.
What should you recommend for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
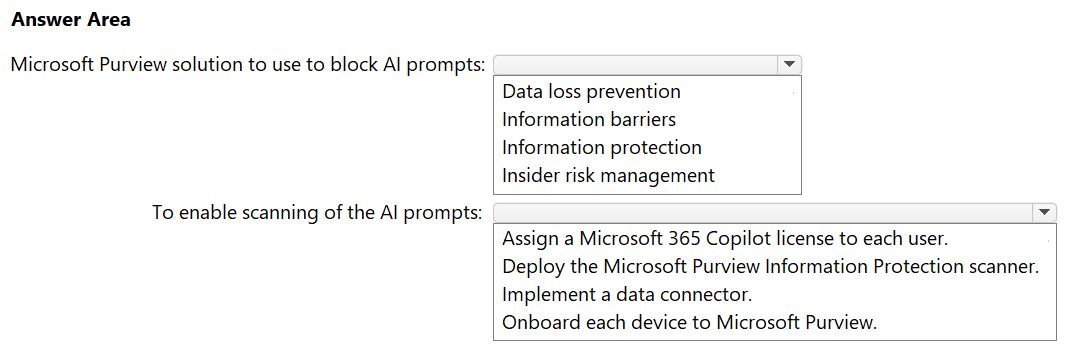
Correct Answer: Block AI prompts: Data loss prevention
Enable scanning of AI prompts: Onboard each device to Microsoft Purview
Explanation: Purview DLP can detect sensitive information types and block confidential data from being submitted to supported generative AI sites. Scanning prompts entered into third-party AI websites requires endpoint capabilities, so Windows devices must be onboarded to Microsoft Purview (Endpoint DLP).
Question 19
HOTSPOT
-
You are designing new Azure applications based on security best practices from the Microsoft Cloud Adoption Framework for Azure. Each application will be deployed to a dedicated and secure environment that will contain isolated instances of the following key Azure security resources:
• Azure Key Vault
• Virtual networks
• An Azure subscription
• Azure Policy assignments
• Network security groups (NSGs)
• Role-based access control (RBAC) assignments
You need to recommend which type of environment and which module to use to deploy the applications. The solution must use infrastructure as code (IaC) to deploy each application environment.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
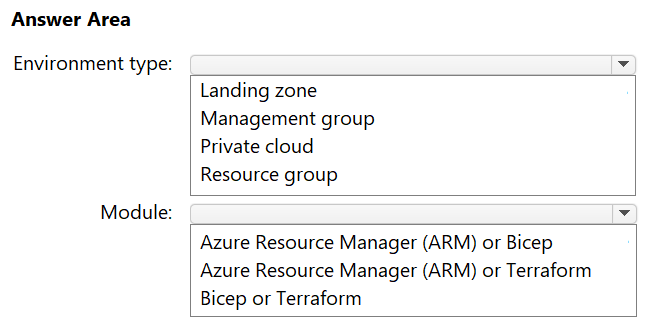
Correct Answer: Environment type: Landing zone
Module: Bicep or Terraform
Explanation: The Cloud Adoption Framework recommends application landing zones as isolated environments. Enterprise-scale landing zones are deployed using IaC, with Bicep or Terraform as the recommended implementation modules.
Question 20
You have a Microsoft 365 subscription that contains 500 users. Each user is assigned a Microsoft 365 E5 license and uses a Windows device.
Microsoft Purview data loss prevention (DLP) policies are applied to Microsoft Exchange Online email and SharePoint Online sites.
You plan to monitor the usage of third-party generative AI apps by using Microsoft Purview Data Security Posture Management for AI (DSPM for AI).
What should you do first?
A. Enable Microsoft Purview insider risk management for all the users.
B. Onboard all endpoint devices to Microsoft Purview.
C. Configure Microsoft Purview data connectors for the generative AI apps.
D. License all the users for Microsoft 365 Copilot.
Show Answer
Correct Answer: B
Explanation: To monitor the use of third-party generative AI apps with Microsoft Purview DSPM for AI, the prerequisite is onboarding endpoint devices so endpoint activity can be discovered and monitored. Insider Risk Management, AI app connectors, or Microsoft 365 Copilot licenses are not the initial prerequisite for monitoring third-party AI app usage. The provided Microsoft documentation lists endpoint onboarding as a prerequisite.
Question 21
HOTSPOT
-
You have a Microsoft 365 E5 subscription.
You need to recommend a security solution that meets the following requirements:
• Automatically identifies and stops external, brute force attacks against accounts in the subscription
• Automatically identifies and stops external attacks that use an internal account to exfiltrate data from Microsoft SharePoint Online sites in the subscription
What should you include in the recommendation for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
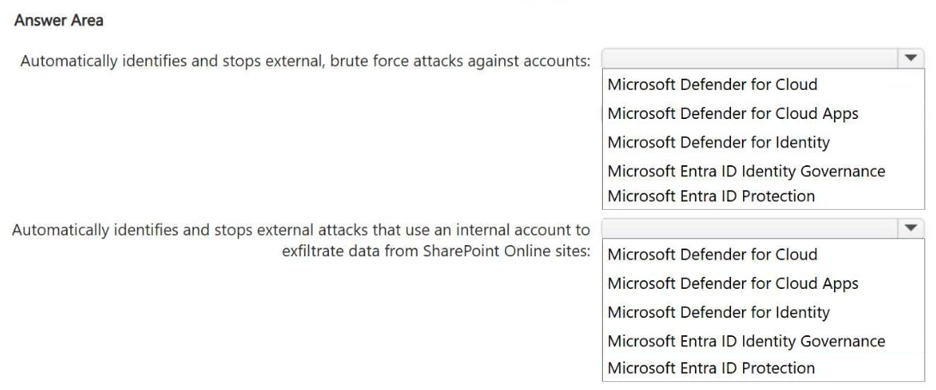
Correct Answer: Microsoft Entra ID Protection
Microsoft Defender for Cloud Apps
Explanation: Entra ID Protection detects and mitigates identity-based risks such as brute-force/password spray attacks. Defender for Cloud Apps detects and can automatically respond to anomalous cloud activity, including insider-account-based data exfiltration from SharePoint Online.
Question 22
HOTSPOT
-
Your company has offices in 10 countries.
You have a Microsoft 365 subscription that contains 1,000 users. Each user is assigned a Microsoft 365 E5 license.
You plan to deploy a compliance assessment solution. The solution must meet the following requirements:
• Ensure that compliance is assessed based on the regulations of the country of each office.
• Provide improvement action guidance to ensure compliance of the subscription.
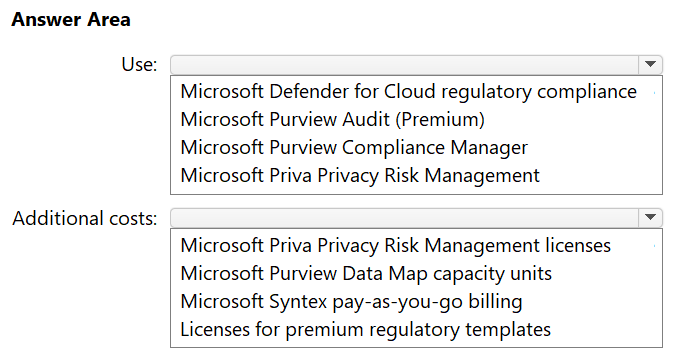
You need to recommend the service that should be used to perform the assessments, and identify additional costs that will be incurred.
What should you recommend and what should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Use: Microsoft Purview Compliance Manager
Additional costs: Licenses for premium regulatory templates
Explanation: Microsoft Purview Compliance Manager assesses compliance against regulatory standards for different regions and provides improvement actions. Microsoft 365 E5 includes Compliance Manager, but many country/industry-specific assessment templates are premium and require additional licensing.
Question 23
You have a Microsoft 365 subscription that uses Microsoft Purview.
You need to recommend a solution that will provide guidance on how to ensure that Personally Identifiable Information (PII) in the subscription adheres to local privacy regulations. The solution must minimize administrative effort.
Which Microsoft Purview solution should you include in the recommendation?
A. Data Loss Prevention
B. Information Protection
C. Insider Risk Management
D. Compliance Manager
Show Answer
Correct Answer: D
Explanation: Compliance Manager provides assessments, compliance scores, and recommended improvement actions to help organizations meet regulatory requirements, including privacy regulations, with built-in guidance and templates. This directly addresses providing guidance while minimizing administrative effort. Data Loss Prevention, Information Protection, and Insider Risk Management serve different purposes and do not provide regulatory compliance guidance.
Question 24
HOTSPOT
-
You have an Azure subscription.
You enable the Defender Cloud Security Posture Management (CSPM) plan.
You need to optimize the security posture of the subscription by implementing Microsoft Defender for Cloud secure score recommendations.
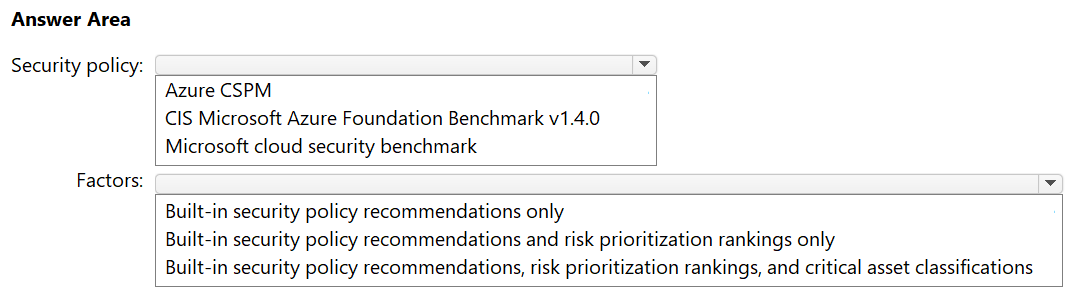
Which security policy should you enable, and which factors will have a direct impact on the secure score? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Security policy: Microsoft cloud security benchmark
Factors: Built-in security policy recommendations, risk prioritization rankings, and critical asset classifications
Explanation: Defender CSPM extends secure score beyond built-in recommendations by incorporating attack-path/risk prioritization and critical asset context. The Microsoft cloud security benchmark is the recommended security policy baseline.
Question 25
HOTSPOT
-
You have an Azure subscription.
You plan to deploy an Azure App Service app named App1 that will access an external web service by using a username and password.
You need to recommend a password storage solution for App1 that meets the following requirements:
• Ensures that the password is stored securely
• Ensures that App1 can authenticate to the service that will store the password
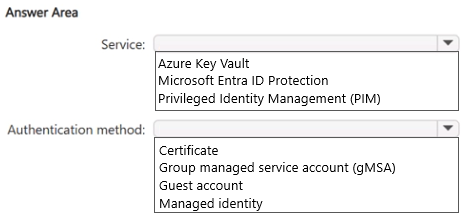
Which service should you use to store the password, and which authentication method should App1 use to access the service? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation: Azure Key Vault is the Azure service designed to securely store secrets such as passwords. An Azure App Service can use its managed identity to authenticate to Key Vault without storing credentials in the application.
Question 26
You have an Azure subscription that contains a web app named App1. App1 uses a Microsoft Entra user account named SRV1 as a service account to authenticate to an Azure SQL database named DB1.
You discover that a developer accessed DB1 directly by using SRV1.
You need to recommend a secure authentication method that will prevent credential misuse outside of App1. The solution must minimize administrative effort.
What should you recommend?
A. a managed identity
B. a group managed service account (gMSA)
C. a delegated managed service account (dMSA)
D. a federated identity credential
Show Answer
Correct Answer: A
Explanation: A managed identity is the recommended authentication method for an Azure App Service accessing Azure SQL. It eliminates stored user credentials, binds authentication to the application resource, and prevents developers from reusing a shared Entra user account outside the app while requiring minimal administration. gMSA and dMSA are for Windows/Active Directory scenarios, and a federated identity credential is used to establish workload identity federation, not as the primary authentication mechanism for an App Service to Azure SQL.
$19
Get all 314 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.