This is the free Amazon SCS-C03 practice question bank —
50 of 87 total questions, each with a full explanation, free to
read with no signup required. Updated 2026-10-13.
Every answer is verified against official Amazon documentation —
see our methodology.
Question 1
A company is running an application on Amazon EC2 instances in an Auto Scaling group. The application stores logs locally. A security engineer noticed that logs were lost after a scale-in event. The security engineer needs to recommend a solution to ensure the durability and availability of log data. All logs must be kept for a minimum of 1 year for auditing purposes.
What should the security engineer recommend?
A. Within the Auto Scaling lifecycle, add a hook to create and attach an Amazon Elastic Block Store (Amazon EBS) log volume each time an EC2 instance is created. When the instance is terminated, the EBS volume can be reattached to another instance for log review.
B. Create an Amazon Elastic File System (Amazon EFS) file system and add a command in the user data section of the Auto Scaling launch template to mount the EFS file system during EC2 instance creation. Configure a process on the instance to copy the logs once a day from an instance Amazon Elastic Block Store (Amazon EBS) volume to a directory in the EFS file system.
C. Add an Amazon CloudWatch agent into the AMI used in the Auto Scaling group. Configure the CloudWatch agent to send the logs to Amazon CloudWatch Logs for review.
D. Within the Auto Scaling lifecycle, add a lifecycle hook at the terminating state transition and alert the engineering team by using a lifecycle notification to Amazon Simple Notification Service (Amazon SNS). Configure the hook to remain in the Terminating:Wait state for 1 hour to allow manual review of the security logs prior to instance termination.
Show Answer
Correct Answer: C
Explanation: Configure the CloudWatch agent to continuously send logs to Amazon CloudWatch Logs, so they remain available even after an EC2 instance is scaled in. Set the log group’s retention period to at least 1 year to meet the auditing requirement.
Question 1
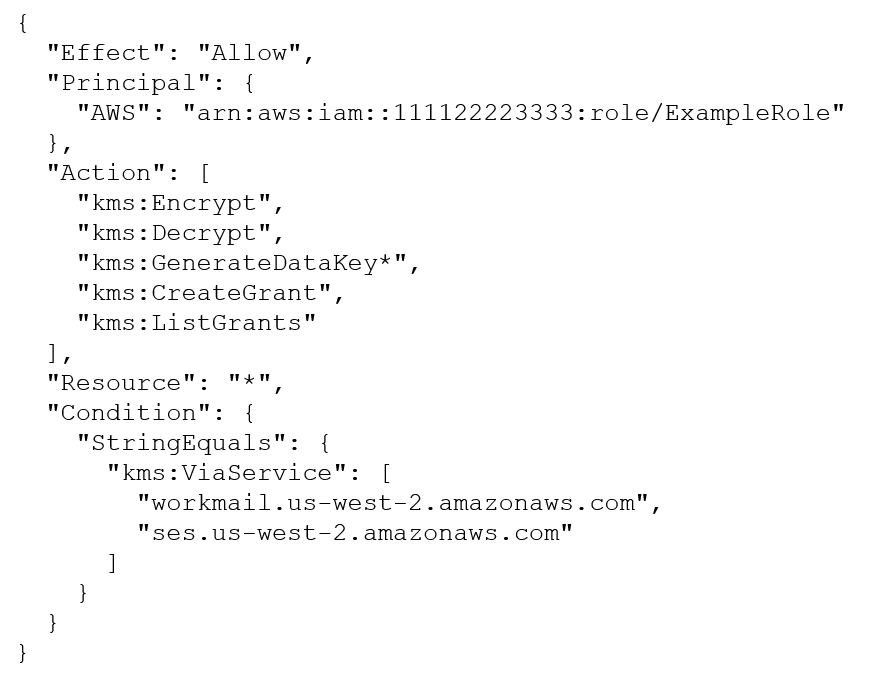
What is the effect of the following AWS Key Management Service (AWS KMS} key policy that is attached to a customer managed key?
A. Amazon WorkMail and Amazon Simple Email Service (Amazon SES) have delegated KMS encrypt and decrypt permissions to the ExampleRole principal in the 111122223333 account.
B. The ExampleRole principal can transparently encrypt and decrypt email exchanges specifically between ExampleRole and AWS.
C. The customer managed key can be used for encrypting and decrypting only when the principal is ExampleRole and when the request comes from Amazon WorkMail or Amazon Simple Email Service (Amazon SES) in the specified AWS Region.
D. The key policy allows Amazon WorkMail or Amazon Simple Email Service (Amazon SES) to encrypt or decrypt on behalf of the ExampleRole for any customer managed key in the account.
Show Answer
Correct Answer: C
Explanation: The policy grants the ExampleRole permissions on this customer managed key, but only when KMS is called through Amazon WorkMail or Amazon SES in us-west-2, as enforced by the `kms:ViaService` condition. The policy also includes grant-related permissions, so it is not limited to encrypt and decrypt operations.
Question 1
A company runs an application on a fleet of Amazon EC2 instances. The application is accessible to users around the world. The company associates an AWS WAF web ACL with an Application Load Balancer (ALB) that routes traffic to the EC2 instances.
A security engineer is investigating a sudden increase in traffic to the application. The security engineer discovers a significant amount of potentially malicious requests coming from hundreds of IP addresses in two countries. The security engineer wants to quickly limit the potentially malicious requests. The security engineer does not want to prevent legitimate users from accessing the application.
Which solution will meet these requirements?
A. Use AWS WAF to implement a rate-based rule for all incoming requests.
B. Use AWS WAF to implement a geographical match rule to block all incoming traffic from the two countries.
C. Edit the ALB security group to include a geographical match rule to block all incoming traffic from the two countries
D. Add deny rules to the ALB security group that prohibit incoming requests from the IP addresses.
Show Answer
Correct Answer: A
Explanation: A rate-based AWS WAF rule is designed to quickly mitigate spikes of requests by tracking request rates per source IP and applying actions such as block or challenge when a threshold is exceeded. This limits abusive traffic while still allowing legitimate users that stay below the threshold. Blocking entire countries (B) would likely prevent legitimate users from those countries from accessing the application. ALB security groups do not support geographic match rules (C), and security groups cannot practically maintain hundreds of dynamic IP deny rules (D).
Question 1
A company purchased a third-party managed rule group from AWS Marketplace to use with AWS WAF. The company uses AWS Organizations to manage multiple AWS accounts in a single organization. Application Load Balancers (ALBs) are present in multiple accounts and multiple AWS Regions.
The company needs a solution to ensure that the rule group is used with every web ACL that is attached to every ALB.
Which solution will meet this requirement with the LEAST operational overhead?
A. Create an AWS CloudFormation template. Deploy the template as a stack set in the management account. Configure the template to add the third-party managed rule group to each web ACL in each account and Region.
B. Configure an SCP to insert the AWS WAF rule group ARN in every new or existing web ACL in each account and Region.
C. Create an AWS WAF policy in AWS Firewall Manager. Specify the third-party managed rule group. Set the scope of the policy to all accounts and Regions.
D. Enable AWS Security Hub CSPM in the organization. Configure Security Hub CSPM to automatically generate a finding if the third-party managed rule group is missing from any web ACL.
Show Answer
Correct Answer: C
Explanation: AWS Firewall Manager centrally enforces AWS WAF policies across an AWS Organizations organization. A policy that includes the third-party managed rule group and targets ALBs provides ongoing enforcement with less operational overhead than updating web ACLs through StackSets. Firewall Manager policies are regional, so the policy must be configured in each applicable Region.
Question 2
A public subnet contains two Amazon EC2 instances. The subnet has a custom network ACL. A security engineer is designing a solution to improve the subnet security.
The solution must allow outbound traffic to an internet service that uses TLS through port 443. The solution also must deny inbound traffic that is destined for MySQL port 3306.
Which network ACL rule set meets these requirements?
A. Use inbound rule 100 to allow traffic on TCP port 443. Use inbound rule 200 to deny traffic on TCP port 3306. Use outbound rule 100 to allow traffic on TCP port 443.
B. Use inbound rule 100 to deny traffic on TCP port 3306. Use inbound rule 200 to allow traffic on TCP port range 1024-65535. Use outbound rule 100 to allow traffic on TCP port 443.
C. Use inbound rule 100 to allow traffic on TCP port range 1024-65535. Use inbound rule 200 to deny traffic on TCP port 3306. Use outbound rule 100 to allow traffic on TCP port 443.
D. Use inbound rule 100 to deny traffic on TCP port 3306. Use inbound rule 200 to allow traffic on TCP port 443. Use outbound rule 100 to allow traffic on TCP port 443.
Show Answer
Correct Answer: B
Explanation: Network ACLs are stateless, so the inbound response traffic for an outbound TLS connection must be allowed on ephemeral ports (typically TCP 1024–65535). Rule 100 denies inbound TCP 3306 before the broader ephemeral-port allow rule, and the outbound rule allows TCP 443.
Question 2
A company needs to develop a code-signing application that will use a certificate authority (CA) to sign a code-signing certificate. The solution must use an AWS Key Management Service (AWS KMS) asymmetric key. The solution needs to collect and store immutable evidence about the creation, origin, and use of the KMS key for compliance purposes. This information must be made available to internal auditors.
Which solution meets these requirements?
A. Create an Amazon S3 bucket with S3 Object Lock enabled. Create an AWS CloudTrail trail with an event selector and log file validation enabled for all kms.amazonaws.com CreateKey events. Configure the event selector to send the CreateKey events to the S3 bucket. Create the KMS key. Update the event selector to filter for API calls that reference the KMS key ARN. Provide the auditors with access to the S3 bucket.
B. Implement logging for application operations that reference the KMS key. Ensure that the logs contain all associated metadata. Store the logs in an Amazon CloudWatch Logs log group. Configure an automated export of the log group Send the export to the auditors.
C. Create an Amazon DynamoDB table that the auditors can access. Create an AWS Lambda function that an Amazon EventBridge rule invokes. Configure the EventBridge rule to monitor KMS API calls. Configure the EventBridge rule to filter for all API calls that reference the KMS key ARN. Configure the Lambda function to store the contents of the API calls in the DynamoDB table.
D. Set up Amazon CloudWatch Logs Insights with a custom metric to track KMS key usage. Visualize the metrics by using a CloudWatch dashboard with real-time monitoring. Configure CloudWatch alarms. Use a subscription filter to replicate the data to a separate account for the auditors to review.
Show Answer
Correct Answer: A
Explanation: CloudTrail provides authoritative audit records for KMS API activity, including CreateKey and subsequent key usage. Storing CloudTrail logs in an Amazon S3 bucket with S3 Object Lock provides immutable (WORM) retention, and CloudTrail log file validation provides integrity verification for compliance. Auditors can review the immutable logs directly from S3. The other options rely on mutable stores or monitoring features that do not provide compliance-grade, tamper-evident audit evidence.
Question 2
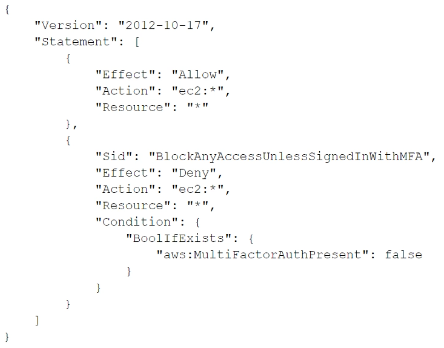
An AWS account administrator created an IAM group and applied the following managed policy to require that each individual user authenticate using multi-factor authentication:
After implementing the policy, the administrator receives reports that users are unable to perform Amazon EC2 commands using the AWS CLI.
What should the administrator do to resolve this problem while still enforcing multi-factor authentication?
A. Change the value of aws:MultiFactorAuthPresent to true.
B. Instruct users to run the aws sts get-session-token CLI command and pass the multi-factor authentication --serial-number and -token-code parameters. Use these resulting values to make API/CLI calls.
C. Implement federated API/CLI access using SAML 2.0, then configure the identity provider to enforce multi-factor authentication.
D. Create a role and enforce multi-factor authentication in the role trust policy. Instruct users to run the sts assume-role CLI command and pass --serial-number and --token-code parameters. Store the resulting values in environment variables. Add sts:AssumeRole to NotAction in the policy.
Show Answer
Correct Answer: B
Explanation: Long-term IAM access keys do not include MFA authentication context, so the policy’s explicit deny blocks the CLI requests. Users should call `sts get-session-token` with their MFA device serial number and token code, then use the returned temporary credentials for AWS CLI/API calls. Those credentials carry MFA context and satisfy the policy condition.
Question 2
A company uses AWS KMS. During an attempt to attach an encrypted Amazon EBS volume to an Amazon EC2 instance, the attachment fails. The company discovers that a customer managed key has become unusable because the key material for the key was deleted. The company needs the data that is on the EBS volume.
A security engineer must recommend a solution to decrypt the EBS volume's encrypted data key. The solution must also attach the volume to the EC2 instance.
Which solution will meet these requirements?
A. Import new key material into the key. Attach the EBS volume.
B. Restore the EBS volume from a snapshot that was taken before the deletion of the key material.
C. Reimport the same key material that originally was imported into the key. Attach the EBS volume.
D. Create a new key. Import new key material. Attach the EBS volume.
Show Answer
Correct Answer: C
Explanation: Reimporting the exact same key material into the original KMS key restores its ability to decrypt the EBS volume’s encrypted data key. New key material or a new KMS key cannot decrypt data encrypted using the original key material, and a snapshot encrypted with that key would remain inaccessible.
Question 3
A security engineer uses Amazon Macie to scan a company’s Amazon S3 buckets for sensitive data. The company has many S3 buckets and many objects stored in the S3 buckets. The security engineer must identify S3 buckets that contain sensitive data and must perform additional scanning on those S3 buckets.
Which solution will meet these requirements with the LEAST administrative overhead?
A. Configure S3 Cross-Region Replication (CRR) on the S3 buckets to replicate the objects to a second AWS Region. Configure Macie in the second Region to scan the replicated objects daily.
B. Create an AWS Lambda function as an S3 event destination for the S3 buckets. Configure the Lambda function to start a Macie scan of an object when the object is uploaded to an S3 bucket.
C. Configure Macie automated discovery to continuously sample data from the S3 buckets. Perform full scans of the S3 buckets where Macie discovers sensitive data.
D. Configure Macie scans to run on the S3 buckets. Aggregate the results of the scans in an Amazon DynamoDB table. Use the DynamoDB table for queries.
Show Answer
Correct Answer: C
Explanation: Macie automated sensitive data discovery continuously samples S3 data and identifies buckets likely to contain sensitive information. The engineer can then run full scans only on those buckets, avoiding the overhead of replicating data, building event-driven automation, or managing a separate results database.
Question 3
A security engineer needs to implement a logging solution that captures detailed information about objects in an Amazon S3 bucket. The solution must include details such as the IAM identity that makes the request and the time the object was accessed. The data must be structured and available in near real time.
Which solution meets these requirements?
A. Enable Amazon S3 server access logging on the S3 bucket. Create a new S3 bucket to store the logs. Analyze the logs from the logging S3 bucket.
B. Enable AWS CloudTrail data event logging. Create a new S3 bucket to store the logs. Analyze the logs from the logging S3 bucket.
C. Configure AWS Config rules to log access to the objects stored in the S3 bucket.
D. Enable Amazon Macie to log access to the objects stored in the S3 bucket.
Show Answer
Correct Answer: B
Explanation: AWS CloudTrail data events record S3 object-level API activity such as GetObject, PutObject, and DeleteObject, including the IAM identity, request time, and other structured event details. These events are delivered in near real time through CloudTrail. S3 server access logging provides access logs but is less suitable for detailed structured auditing of IAM identities and API events. AWS Config tracks resource configuration changes, not object access, and Amazon Macie discovers and classifies sensitive data rather than logging object access.
$19
Get all 87 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.