A company runs critical workloads in an on-premises data center. The company wants to implement an AWS based disaster recovery (DR) solution that will achieve an RTO of less than 1 hour. The company needs to continuously replicate physical and virtual servers. The company must optimize costs for data storage and bandwidth usage. The DR solution must be automated.
Which solution will meet these requirements?
A. Use AWS Backup to directly replicate the on-premises servers to AWS. Enable cross-Region backup copying and data vaulting. Configure recovery points to match the defined RTO. Use AWS Step Functions to automate recovery steps.
B. Configure an AWS Storage Gateway Volume Gateway to use Amazon Elastic Block Store (Amazon EBS) snapshots for recovery. Configure AWS Backup to manage the snapshots. Create automated recovery procedures.
C. Enable AWS Elastic Disaster Recovery. Configure replication agents to continuously replicate each on-premises server. Enable the default staging area subnet configuration.
D. Create an AWS Direct Connect connection between the on-premises data center and AWS. Configure Amazon EventBridge to monitor for failures and to invoke AWS Lambda functions that launch preconfigured Amazon EC2 instances from AMIs in the event of an incident.
Show Answer
Correct Answer: C
Explanation: AWS Elastic Disaster Recovery (AWS DRS) is purpose-built for disaster recovery of physical and virtual on-premises servers. It provides continuous block-level replication, automated failover and recovery orchestration, supports RTOs of minutes (well under 1 hour), and uses a low-cost staging area to optimize storage and bandwidth until recovery is needed. The other options either use services not designed for continuous server replication or require significant custom implementation.
Question 15
A company is using Amazon Made, AWS Firewall Manager. Amazon Inspector, and AWS Shield Advanced in its AWS account. The company wants to receive alerts if a DDoS attack occurs against the account.
Which solution will meet this requirement?
A. Use Macie to detect an active DDoS event. Create Amazon CloudWatch alarms that respond to Macie findings.
B. Use Amazon Inspector to review resources and to invoke Amazon CloudWatch alarms for any resources that are vulnerable to DDoS attacks.
C. Create an Amazon CloudWatch alarm that monitors Firewall Manager metrics for an active DDoS event.
D. Create an Amazon CloudWatch alarm that monitors Shield Advanced metrics for an active DDoS event.
Show Answer
Correct Answer: D
Explanation: AWS Shield Advanced is the AWS service that detects and protects against DDoS attacks. It publishes DDoS-related metrics to Amazon CloudWatch, which can be used to create CloudWatch alarms and notifications (for example, via Amazon SNS) when an active DDoS event is detected. Macie is for sensitive data discovery, Inspector is for vulnerability management, and Firewall Manager is for centrally managing security policies rather than detecting DDoS events itself.
Question 16
HOTSPOT
-
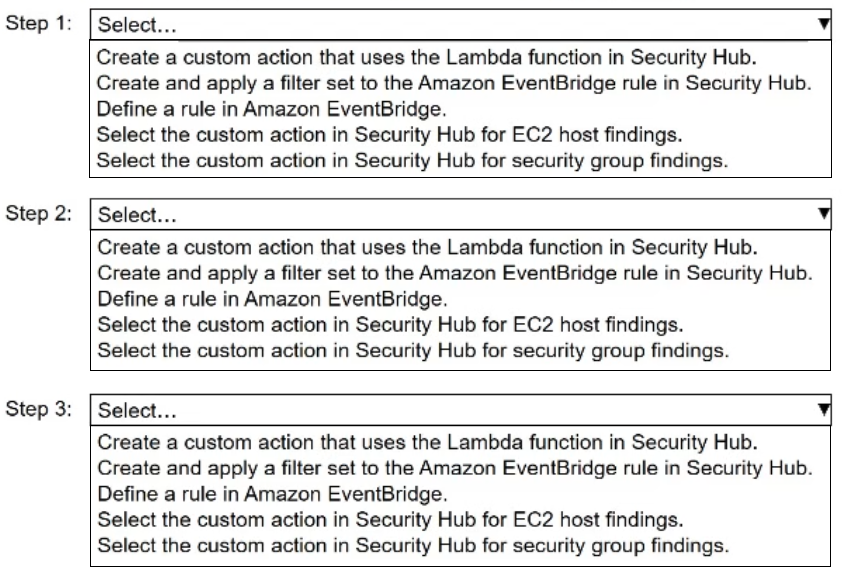
A company is developing an incident response process to quarantine Amazon EC2 hosts that become infected by malware. The company uses an organization in AWS Organizations to manage multiple AWS accounts. The company configures AWS Security Hub in the organization to receive findings from multiple accounts that run across multiple AWS Regions. A security engineer develops an AWS Lambda function to remove all the rules from all security groups for any EC2 instance the company suspects might be infected by malware.
Select and order the correct steps from the following list to deploy and use the Lambda function as a custom action in Security Hub. Select each step one time or not at all. (Select and order THREE.)
• Create a custom action that uses the Lambda function in Security Hub.
• Create and apply a filter set to the Amazon EventBridge rule in Security Hub.
• Define a rule in Amazon EventBridge.
• Select the custom action in Security Hub for EC2 host findings.
• Select the custom action in Security Hub for security group findings.
Show Answer
Correct Answer: Step 1: Create a custom action that uses the Lambda function in Security Hub.
Step 2: Define a rule in Amazon EventBridge.
Step 3: Select the custom action in Security Hub for EC2 host findings.
Explanation: Security Hub custom actions emit EventBridge events. An EventBridge rule matches the custom action event and invokes the Lambda function. Analysts then run the custom action on EC2 host findings to trigger the remediation. Filters on EventBridge are part of the rule's event pattern, not a separate Security Hub deployment step, and security group findings are not the target.
Question 17
A company uses an organization in AWS Organizations to manage multiple AWS accounts. Users access AWS accounts by using IAM users and secret access keys. A security team requires all access to accounts to use temporary security credentials that expire after 60 minutes. Users must use a SAML-based identity provider (IdP) to access the accounts.
Which solution will meet these requirements?
A. Enable access to the AWS Security Token Service (AWS STS). Ensure that users run the get-session-token AWS CLI command with an appropriate duration. Require users to use STS temporary credentials to access AWS accounts.
B. Set up AWS IAM Identity Center and configure an external IdP. Configure permission sets that allow the access that the users require. Configure a session duration limit. Require the users to retrieve SSO credentials by using the AWS CLI. Remove the IAM users from the AWS accounts.
C. Set up AWS Secrets Manager and Amazon Cognito in each AWS account. Configure a Cognito identity pool to use an external IdP and connect to Secrets Manager. Enable managed secret rotation in Secrets Manager. Ensure that the users run the get-secret-value AWS CLI command to access the AWS accounts.
D. Enable AWS IAM Roles Anywhere in the organization management account. Ensure that users install the credential helper tool. Configure IAM roles within the management account with an appropriate session duration. Ensure that the users retrieve temporary credentials from the credential helper tool to access the AWS accounts.
Show Answer
Correct Answer: B
Explanation: AWS IAM Identity Center integrates with an external SAML identity provider, issues temporary AWS STS credentials, supports configurable session durations (such as 60 minutes), and is the recommended approach for multi-account access through AWS Organizations. Removing IAM users ensures access is through federated temporary credentials only.
Question 18
A company maintains both on-premises legacy systems and resources in AWS. The AWS resources include an Amazon DynamoDB table and an Amazon S3 bucket. The on-premises legacy systems need to connect to DynamoDB and Amazon S3 on a regular basis.
The company currently uses a bastion host in a public subnet in a VPC. The company connects to the bastion host by using an SSH private key that the company stores on-premises. The instance profile that is assigned to the bastion host has full access to Amazon S3 and DynamoDB.
A security team issues a new internal policy that requires all bastion hosts to be removed. The policy requires all systems to authenticate by using certificate-based authentication.
Which solution will meet these requirements?
A. Set up an AWS Direct Connect connection and create a VPN connection to a VPC that has access to VPC endpoints for the required services.
B. Set up the on-premises systems to use AWS IAM Roles Anywhere to authenticate.
C. Use AWS Private Certificate Authority to issue SSL certificates to give on-premises systems access to resources on AWS.
D. Create an IAM user that has permission to temporarily assume an IAM role and to use temporarily assumed role credentials to access the required resources.
Show Answer
Correct Answer: B
Explanation: AWS IAM Roles Anywhere is designed to allow workloads running outside AWS to authenticate using X.509 certificates issued by a trusted CA and obtain temporary AWS credentials for IAM roles. This satisfies the requirement to remove bastion hosts and use certificate-based authentication while accessing Amazon S3 and DynamoDB. AWS Private CA alone only issues certificates and does not grant IAM access. Direct Connect/VPN provides network connectivity but not certificate-based IAM authentication. IAM users with assumed roles rely on IAM credentials rather than X.509 certificate authentication.
Question 19
A security engineer needs to build a solution to turn AWS CloudTrail back on in multiple AWS Regions in case it is ever turned off.
What is the MOST efficient way to implement this solution?
A. Use AWS Config with a managed rule to initiate the AWS-EnableCloudTrail remediation.
B. Create an Amazon EventBridge event with a cloudtrail.amazonaws.com event source and a StartLogging event name to invoke an AWS Lambda function to call the StartLogging API.
C. Create an Amazon CloudWatch alarm with a cloudtrail.amazonaws.com event source and a StopLogging event name to invoke an AWS Lambda function to call the StartLogging API.
D. Monitor AWS Trusted Advisor to ensure CloudTrail logging is enabled.
Show Answer
Correct Answer: A
Explanation: AWS Config provides a managed rule to detect when CloudTrail is not enabled and can automatically invoke the AWS-EnableCloudTrail remediation to re-enable logging. This is the most efficient approach because it uses managed detection and auto-remediation without custom code and can be deployed across multiple Regions. EventBridge option B listens for StartLogging rather than StopLogging, C incorrectly uses CloudWatch alarms for CloudTrail API events instead of EventBridge/CloudTrail event matching, and Trusted Advisor does not provide automatic remediation.
Question 20
An ecommerce website was down for 1 hour following a DDoS attack. Users were unable to connect to the website during the attack period. The ecommerce company's security team is worried about future potential attacks and wants to prepare for such events. The company needs to minimize downtime in its response to similar attacks in the future.
Which steps would help achieve this? (Choose two.)
A. Enable Amazon GuardDuty to automatically monitor for malicious activity and block unauthorized access.
B. Subscribe to AWS Shield Advanced and reach out to AWS Support in the event of an attack.
C. Use VPC Flow Logs to monitor network traffic and an AWS Lambda function to automatically block an attacker's IP using security groups.
D. Set up an Amazon EventBridge rule to monitor the AWS CloudTrail events in real time, use AWS Config rules to audit the configuration, and use AWS Systems Manager for remediation.
E. Use AWS WAF to create rules to respond to such attacks.
Show Answer
Correct Answer: B, E
Explanation: AWS Shield Advanced provides enhanced DDoS protection, automatic mitigation capabilities, and access to the AWS DDoS Response Team (DRT), helping reduce downtime during attacks. AWS WAF can filter and block malicious web requests with rate-based and custom rules, mitigating application-layer DDoS attacks in real time. GuardDuty detects threats but does not automatically block DDoS traffic, VPC Flow Logs with Lambda and security groups are not an effective primary DDoS mitigation strategy, and EventBridge/CloudTrail/Config/Systems Manager focus on auditing and remediation rather than real-time DDoS protection.
Question 21
A company runs an application on an Amazon EC2 instance. The application generates invoices and stores them in an Amazon S3 bucket. The instance profile that is attached to the instance has appropriate access to the S3 bucket.
The company needs to share each invoice with multiple clients that do not have AWS credentials. Each client must be able to download only the client's own invoices. Clients must download their invoices within 1 hour of invoice creation. Clients must use only temporary credentials to access the company’s AWS resources.
A security engineer creates a script that runs on the EC2 instance. The script uses the instance profile to generate an S3 presigned URL for the clients. Each presigned URL expires after 1 hour.
Which additional step will meet these requirements?
A. Update the S3 bucket policy to ensure that clients that use presigned URLs have the S3:Get* permission and the S3:List* permission to access S3 objects in the bucket.
B. Add a StringEquals condition to the IAM role policy for the EC2 instance profile. Configure the policy condition to restrict access based on the s3:ResourceTag/ClientId tag of each invoice. Tag each generated invoice with the ID of its corresponding client.
C. Update the script to use AWS Security Token Service (AWS STS) to obtain new credentials each time the script runs by assuming a new role that has S3 GetObject permissions. Use the credentials to generate the presigned URLs.
D. Generate an access key and a secret key for an IAM user that has S3:GetObject permissions on the S3 bucket. Embed the keys into the script. Use the keys to generate the presigned URLs.
Show Answer
Correct Answer: C
Explanation: Presigned URLs are signed with the credentials used to create them. Using temporary AWS STS credentials to assume a role with the required S3 GetObject permission ensures the presigned URLs are backed by temporary credentials, satisfying the requirement that only temporary credentials be used. The URL can then expire after 1 hour. Bucket policy changes are unnecessary for presigned URLs, resource tags do not isolate access once a URL is issued, and embedding long-term IAM user keys violates the temporary credentials requirement.
Question 22
A company has two AWS accounts: Account A and Account B. Each account has a VPC. An application that runs in the VPC in Account A needs to write to an Amazon S3 bucket in Account B. The application in Account A already has permission to write to the S3 bucket in Account B.
The application and the S3 bucket are in the same AWS Region. The company cannot send network traffic over the public internet.
Which solution will meet these requirements?
A. In both accounts, create a transit gateway and VPC attachments in a subnet in each Availability Zone. Update the VPC route tables.
B. Deploy a software VPN appliance in Account A. Create a VPN connection between the software VPN appliance and a virtual private gateway in Account
C. Create a VPC peering connection between the VPC in Account A and the VPC in Account B. Update the VPC route tables, network ACLs, and security groups to allow network traffic between the peered IP ranges.
D. In Account A, create a gateway VPC endpoint for Amazon S3. Update the VPC route table in Account A.
Show Answer
Correct Answer: D
Explanation: A gateway VPC endpoint for Amazon S3 provides private connectivity from the VPC to S3 over the AWS network without traversing the public internet. Because the application already has IAM permission to write to the bucket in the other account, only private network access is needed. Cross-account access to an S3 bucket works through the S3 gateway endpoint as long as bucket and IAM policies allow it. Transit gateways, VPNs, and VPC peering connect VPCs to each other, but S3 is not hosted inside the destination VPC.
Question 23
A company is implementing a new application in a new AWS account. A VPC and subnets have been created for the application. The application has been peered to an existing VPC in another account in the same AWS Region for database access Amazon EC2 instances will regularly be created and terminated in the application VPC, but only some of them will need access to the databases in the peered VPC over TCP port 1521. A security engineer must ensure that only the EC2 instances that need access to the databases can access them through the network.
How can the security engineer implement this solution?
A. Create a new security group in the database VPC and create an inbound rule that allows all traffic from the IP address range of the application VPC. Add a new network ACL rule on the database subnets. Configure the rule to TCP port 1521 from the IP address range of the application VPC. Attach the new security group to the database instances that the application instances need to access.
B. Create a new security group in the application VPC with an inbound rule that allows the IP address range of the database VPC over TCP port 1521. Create a new security group in the database VPC with an inbound rule that allows the IP address range of the application VPC over port 1521. Attach the new security group to the database instances and the application instances that need database access.
C. Create a new security group in the application VPC with no inbound rules. Create a new security group in the database VPC with an inbound rule that allows TCP port 1521 from the new application security group in the application VPAttach the application security group to the application instances that need database access and attach the database security group to the database instances.
D. Create a new security group in the application VPC with an inbound rule that allows the IP address range of the database VPC over TCP port 1521. Add a new network ACL rule on the database subnets. Configure the rule to allow all traffic from the IP address range of the application VPC. Attach the new security group to the application instances that need database access.
Show Answer
Correct Answer: C
Explanation: Use dedicated security groups to identify only the application instances that require database access. Attach the application security group only to those EC2 instances, and configure the database security group to allow inbound TCP port 1521 from the application security group across the same-Region VPC peering connection. This provides instance-level least-privilege access and automatically accommodates frequently created and terminated instances without managing IP addresses.
$19
Get all 87 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.