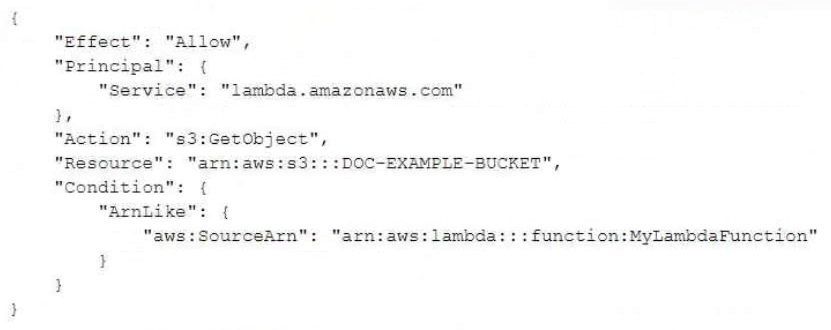
A security engineer is troubleshooting an AWS Lambda function that is named MyLambdaFunction. The function is encountering an error when the function attempts to read the objects in an Amazon S3 bucket that is named DOC-EXAMPLE-BUCKET. The S3 bucket has the following bucket policy:
Which change should the security engineer make to the policy to ensure that the Lambda function can read the bucket objects?
A. Remove the Condition element. Change the Principal element to the following:
B. Change the Action element to the following:
C. Change the Resource element to "arn:aws:s3:::DOC-EXAMPLE- BUCKET/*''.
D. Change the Resource element to "arn:aws:lambda:::function:MyLambdaFunction". Change the Principal element to the following:
Show Answer
Correct Answer: C
Explanation: For `s3:GetObject`, the resource must identify the objects in the bucket, so change it to `arn:aws:s3:::DOC-EXAMPLE-BUCKET/*`. In a real Lambda runtime setup, the function’s execution role must also be authorized to read the objects.
Question 3
A security engineer writes an AWS CloudFormation template for a company. The template deploys a secured Amazon S3 bucket. The company wants to use the S3 bucket as a standardized template for all other S3 buckets. The template needs to be available to all the AWS accounts that are part of a single organization in AWS Organizations. Then, all end users can use the template to deploy new S3 buckets.
Which solution will meet these requirements?
A. Use AWS Service Catalog to create a portfolio. Within the portfolio, create a new product by uploading the CloudFormation template for the secure S3 configuration. Grant access to end users by allowing access to the portfolio.
B. Use AWS Resource Access Manager (AWS RAM) to create a new resource share for the template. Select customer managed permissions and specify which IAM principals are allowed to access the shared resource.
C. Use AWS Resource Access Manager (AWS RAM) to create a new resource share for the template. Select AWS managed permissions for Amazon S3. Grant access to all AWS accounts in the organization.
D. Deploy the S3 bucket by using the template in an AWS account owned by the security engineer. Use AWS Resource Access Manager (AWS RAM) to share the bucket with all the other accounts within the organization for end users to use.
Show Answer
Correct Answer: A
Explanation: AWS Service Catalog lets the security engineer publish the CloudFormation template as a product in a portfolio and grant end users access to launch it. The portfolio can be shared across the AWS Organization, enabling accounts to deploy standardized S3 buckets. AWS RAM shares supported resources, not CloudFormation templates as products.
Question 4
HOTSPOT
-
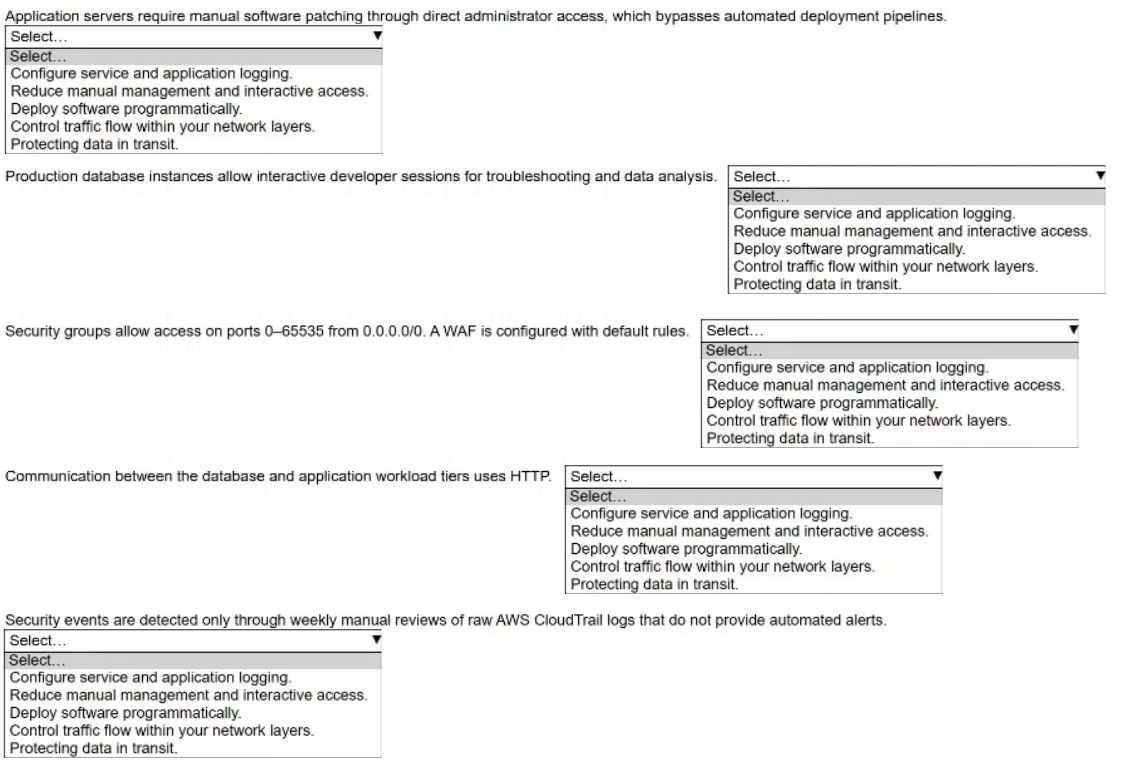
A security engineer is using the AWS Well-Architected Tool to evaluate a multi-tier web application that a company hosts on AWS. During the assessment, the security engineer identifies several resources that violate design principles of the Well-Architected Framework security pillar.
Select the security pillar design principle from the following list that each assessment finding primarily violates. Select each security pillar design principle one time.
• Configure service and application logging
• Reduce manual management and interactive access.
• Deploy software programmatically.
• Control traffic flow within your network layers.
• Protecting data in transit.
Show Answer
Correct Answer: 1. Deploy software programmatically.
2. Reduce manual management and interactive access.
3. Control traffic flow within your network layers.
4. Protecting data in transit.
5. Configure service and application logging.
Explanation: Each finding maps directly to the primary AWS Well-Architected Security Pillar design principle it violates: manual patching bypasses automation, interactive production access should be minimized, overly permissive security groups violate network traffic control, HTTP violates in-transit protection, and manual log review without alerting indicates inadequate logging/monitoring configuration.
Question 4
A security engineer needs to implement a solution to create and control the keys that a company uses for cryptographic operations. The security engineer must create symmetric keys in which the key material is generated and used within a custom key store that is backed by an AWS CloudHSM cluster.
The security engineer will use symmetric and asymmetric data key pairs for local use within applications. The security engineer also must audit the use of the keys.
How can the security engineer meet these requirements?
A. To create the keys, use AWS Key Management Service (AWS KMS) and the custom key stores with the CloudHSM cluster. For auditing, use Amazon Athena.
B. To create the keys, use Amazon S3 and the custom key stores with the CloudHSM cluster. For auditing, use AWS CloudTrail.
C. To create the keys, use AWS Key Management Service (AWS KMS) and the custom key stores with the CloudHSM cluster. For auditing, use Amazon GuardDuty.
D. To create the keys, use AWS Key Management Service (AWS KMS) and the custom key stores with the CloudHSM cluster. For auditing, use AWS CloudTrail.
Show Answer
Correct Answer: D
Explanation: Use AWS KMS with a custom key store backed by the CloudHSM cluster to create and control the symmetric KMS keys. KMS can use those keys to generate encrypted symmetric data keys and asymmetric data key pairs for application use. AWS CloudTrail records KMS API activity, including key-use operations, for auditing.
Question 5
A company is planning to deploy a new log analysis environment. The company needs to implement a solution to analyze logs from multiple AWS services in near real time. The solution must provide the ability to search the logs. The solution also must send alerts to an existing Amazon Simple Notification Service (Amazon SNS) topic when specific logs match detection rules.
Which solution will meet these requirements?
A. Analyze the logs by using Amazon OpenSearch Service. Search the logs from the OpenSearch API. Use OpenSearch Service Security Analytics to match logs with detection rules and to send alerts to the SNS topic.
B. Analyze the logs by using AWS Security Hub. Search the logs from the Findings page in Security Hub. Create custom actions to match logs with detection rules and to send alerts to the SNS topic.
C. Analyze the logs by using Amazon CloudWatch Logs. Use a subscription filter to match logs with detection rules and to send alerts to the SNS topic. Search the logs manually by using CloudWatch Logs Insights.
D. Analyze the logs by using Amazon QuickSight. Search the logs by listing the query results in a dashboard. Run queries to match logs with detection rules and to send alerts to the SNS topic
Show Answer
Correct Answer: A
Explanation: Amazon OpenSearch Service is designed for near real-time log ingestion and search across multiple AWS services. Its Security Analytics capability supports detection rules and can generate alerts that integrate with Amazon SNS. Security Hub is for security findings rather than general log analysis, CloudWatch Logs Insights supports log queries but not this integrated detection/search workflow, and QuickSight is a BI visualization service, not a log analytics and alerting platform.
Question 5
A company runs workloads in the us-east-1 Region. The company has never deployed resources to other AWS Regions and does not have any multi-Region resources. The company needs to replicate its workloads and infrastructure to the us-west-1 Region.
A security engineer must implement a solution that uses AWS Secrets Manager to store secrets in both Regions. The solution must use AWS Key Management Service (AWS KMS) to encrypt the secrets. The solution must minimize latency and must be able to work if only one Region is available.
The security engineer uses Secrets Manager to create the secrets in us-east-1.
What should the security engineer do next to meet the requirements?
A. Encrypt the secrets in us-east-1 by using an AWS managed KMS key. Replicate the secrets to us-west-1. Encrypt the secrets in us-west-1 by using a new AWS managed KMS key in us-west-1.
B. Encrypt the secrets in us-east-1 by using an AWS managed KMS key. Configure resources in us-west-1 to call the Secrets Manager endpoint in us-east-1.
C. Encrypt the secrets in us-east-1 by using a customer managed KMS key. Configure resources in us-west-1 to call the Secrets Manager endpoint in us-east-1.
D. Encrypt the secrets in us-east-1 by using a customer managed KMS key. Replicate the secrets to us-west-1. Encrypt the secrets in us-west-1 by using the customer managed KMS key from us-east-1.
Show Answer
Correct Answer: A
Explanation: Replicate the secret to us-west-1 so workloads can read a local copy with low latency and continue operating if us-east-1 is unavailable. Secrets Manager encrypts the replica with a KMS key in the destination Region; the AWS managed Secrets Manager key is regional, so each Region uses its own key. Options B and C depend on the us-east-1 endpoint, and the us-east-1 KMS key in D cannot directly encrypt secrets in us-west-1.
Question 6
A company uses AWS Organizations to manage an organization that consists of three workload OUs: Production. Development, and Testing. The company uses AWS CloudFormation templates to define and deploy workload infrastructure in AWS accounts that are associated with the OUs. Different SCPs are attached to each workload OU.
The company successfully deployed a CloudFormation stack update to workloads in the Development OU and the Testing OU. When the company uses the same CloudFormation template to deploy the stack update in an account in the Production OU, the update fails. The error message reports insufficient IAM permissions.
What is the FIRST step that a security engineer should take to troubleshoot this issue?
A. Review the AWS CloudTrail logs in the account in the Production OU. Search for any failed API calls from CloudFormation during the deployment attempt.
B. Remove all the SCPs that are attached to the Production OU. Rerun the CloudFormation stack update to determine if the SCPs were preventing the CloudFormation API calls
C. Confirm that the role used by CloudFormation has sufficient permissions to create, update, and delete the resources that are referenced in the CloudFormation template
D. Make all the SCPs that are attached to the Production OU the same as the SCPs that are attached to the Testing OU.
Show Answer
Correct Answer: A
Explanation: The first troubleshooting step is to review CloudTrail for the failed CloudFormation API calls. CloudTrail shows which API operation was denied and whether the denial was caused by IAM permissions, an SCP, or another policy control. This identifies the root cause before making potentially disruptive policy changes. Removing or changing SCPs is not an appropriate first step, and although verifying the CloudFormation execution role is important, the error should first be investigated using the authoritative audit logs.
Question 6
HOTSPOT -
A company is building a web application that needs to authenticate external users across multiple microservices that the company hosts on Amazon Elastic Container Service (Amazon ECS). The solution must use temporary credentials and minimize the management overhead required to maintain user databases.
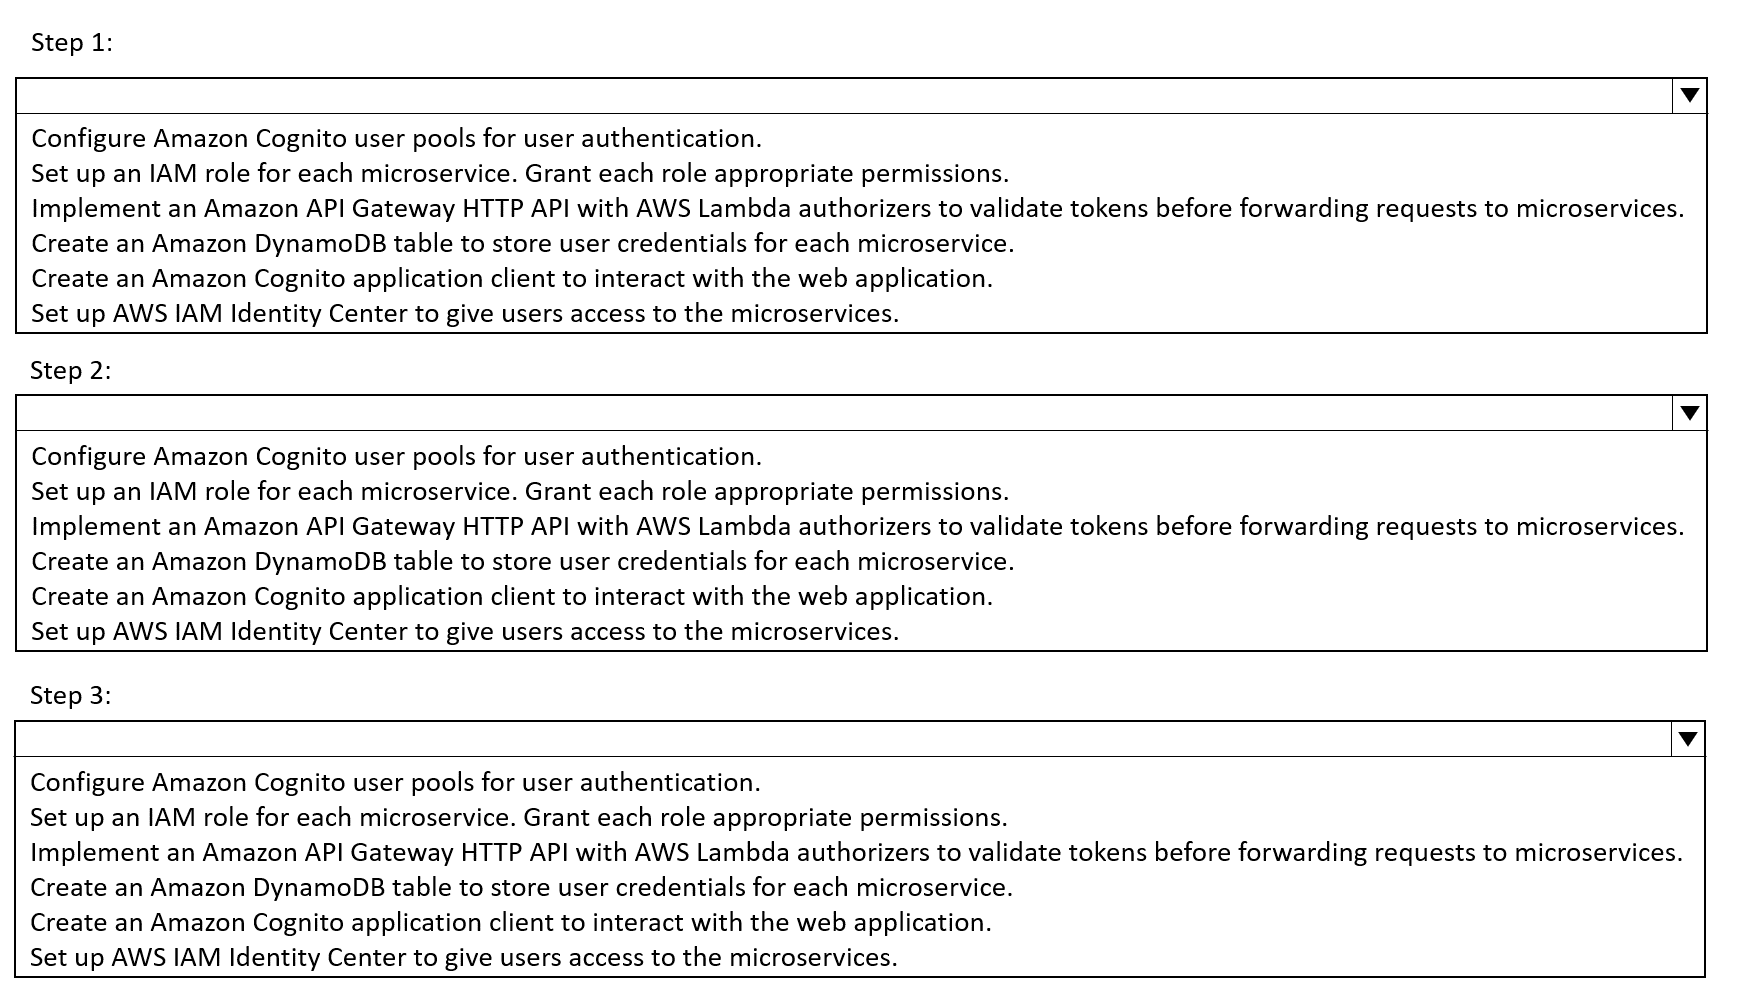
Select and order the correct steps from the following list to implement a secure authentication strategy that meets these requirements. Select each step one time or not at all.
Configure Amazon Cognito user pools for user authentication.
Set up an IAM role for each microservice. Grant each role appropriate permissions.
Implement an Amazon API Gateway HTTP API with AWS Lambda authorizers to validate tokens before forwarding requests to microservices.
Create an Amazon DynamoDB table to store user credentials for each microservice.
Create an Amazon Cognito application client to interact with the web application.
Set up AWS IAM Identity Center to give users access to the microservices.
Show Answer
Correct Answer: Step 1: Configure Amazon Cognito user pools for user authentication.
Step 2: Create an Amazon Cognito application client to interact with the web application.
Step 3: Implement an Amazon API Gateway HTTP API with AWS Lambda authorizers to validate tokens before forwarding requests to microservices.
Explanation: Cognito manages external users and issues short-lived tokens, avoiding a self-managed user database. The application client enables web sign-in, and the authorizer checks tokens before requests reach the ECS microservices.
Question 7
HOTSPOT
-
A company uses an organization in AWS Organizations to manage multiple AWS accounts. A security engineer needs to monitor the security compliance of AWS resources across the organization. The security engineer wants to receive notifications when any AWS resources does not comply with the company's security policies.
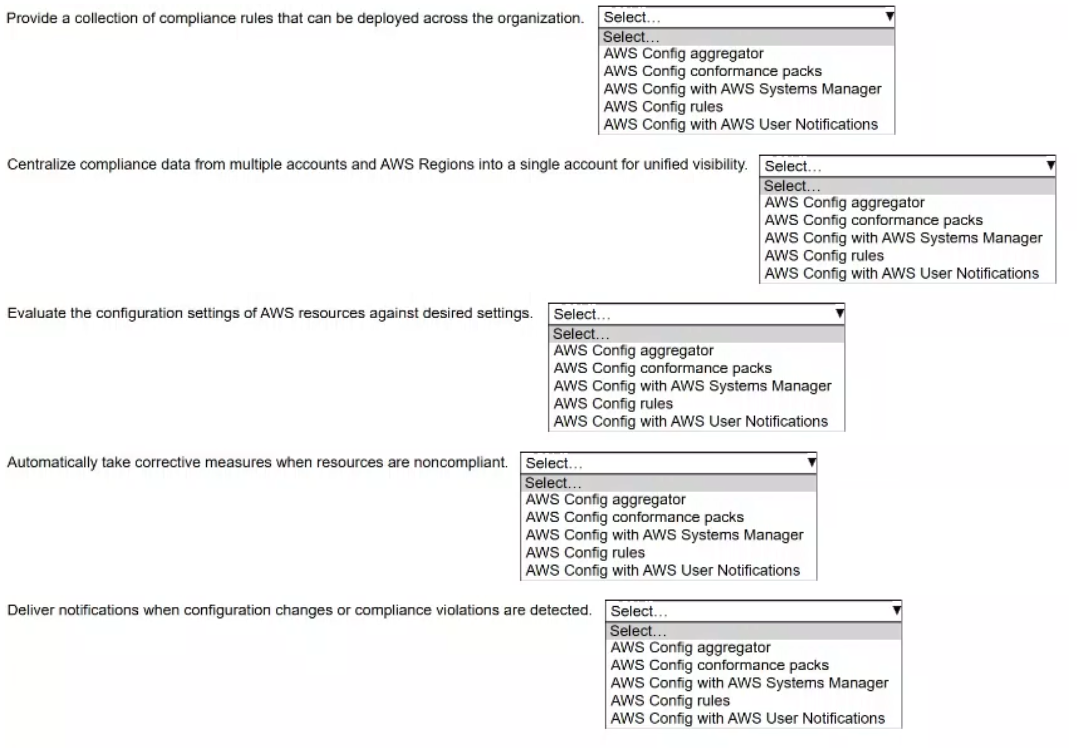
Select the correct AWS Config based solution from the following list to meet each requirement. Select each AWS Config based solution one time.
• AWS Config aggregator
• AWS Config conformance packs
• AWS Config with AWS Systems Manager
• AWS Config rules
• AWS Config with AWS User Notifications
Show Answer
Correct Answer: AWS Config conformance packs
AWS Config aggregator
AWS Config rules
AWS Config with AWS Systems Manager
AWS Config with AWS User Notifications
Explanation: Conformance packs deploy collections of rules organization-wide. Aggregators centralize compliance data across accounts/Regions. Config rules evaluate resource configurations. Systems Manager integrates for auto-remediation. User Notifications delivers alerts for compliance/configuration changes.
Question 7
A company has installed a third-party application that is distributed on several Amazon EC2 instances and on-premises servers. Occasionally, the company's IT team needs to use SSH to connect to each machine to perform software maintenance tasks. Outside these time slots, the machines must be completely isolated from the rest of the network. The company does not want to maintain any SSH keys. Additionally, the company wants to pay only for machine hours when there is an SSH connection.
Which solution will meet these requirements?
A. Create a bastion host with port forwarding to connect to the machines.
B. Set up AWS Systems Manager Session Manager to allow temporary connections.
C. Use AWS CloudShell to create serverless connections.
D. Set up an interface VPC endpoint for each machine for private connection.
Show Answer
Correct Answer: B
Explanation: AWS Systems Manager Session Manager supports EC2 instances and on-premises servers without maintaining SSH keys or opening inbound SSH ports. Machines can remain isolated from inbound network connections except when an authorized session is established, and it avoids the cost of operating a dedicated bastion host. Note that the underlying machines may still incur compute charges while running; Session Manager itself does not require a continuously running access host.
$19
Get all 87 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.