HOTSPOT
-
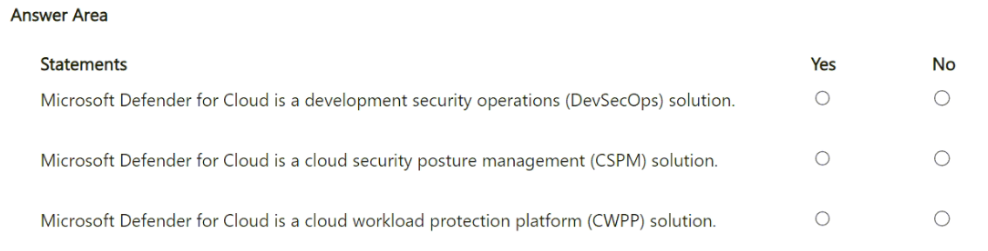
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: Yes
Yes
Yes
Explanation: Microsoft Defender for Cloud combines DevSecOps capabilities, Cloud Security Posture Management (CSPM), and Cloud Workload Protection Platform (CWPP) capabilities according to Microsoft documentation.
Question 35
What is Azure Key Vault used for?
A. to deploy a cloud-based network security service that protects Azure virtual network resources
B. to protect cloud-based applications from cyber threats and vulnerabilities
C. to safeguard cryptographic keys and other secrets used by cloud apps and services
D. to provide secure and seamless RDP/SSH connectivity to Azure virtual machines via TLS from the Azure portal
Show Answer
Correct Answer: C
Explanation: Azure Key Vault is a managed Azure service for securely storing and controlling access to secrets, cryptographic keys, and certificates used by applications and services. The other options describe Azure Firewall/Application Gateway WAF, Microsoft Defender services, or Azure Bastion.
Question 36
You have an Azure subscription that contains a Log Analytics workspace.
You need to onboard Microsoft Sentinel.
What should you do first?
A. Create a hunting query.
B. Correlate alerts into incidents.
C. Connect to your data sources.
D. Create a custom detection rule.
Show Answer
Correct Answer: C
Explanation: The first step in onboarding Microsoft Sentinel to an existing Log Analytics workspace is to connect data sources using built-in data connectors. Sentinel requires ingested security data before you can create analytics rules, correlate alerts into incidents, or perform hunting.
Question 37
HOTSPOT
-
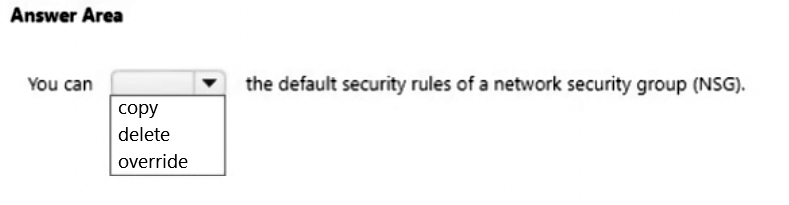
Select the answer that correctly completes the sentence.
Show Answer
Correct Answer: override
Explanation: Azure NSG default security rules cannot be deleted or modified directly, but you can override their effect by creating custom rules with a higher priority (lower priority number).
Question 38
Which Microsoft portal provides information about how Microsoft cloud services comply with regulatory standard, such as International Organization for Standardization (ISO)?
A. the Microsoft 365 admin center
B. Azure Cost Management + Billing
C. Microsoft Service Trust Portal
D. the Microsoft Purview compliance portal
Show Answer
Correct Answer: C
Explanation: The Microsoft Service Trust Portal provides information about Microsoft cloud services' compliance with regulatory standards and certifications, including ISO, SOC, GDPR, and other compliance documentation, audit reports, and trust resources. The Microsoft Purview compliance portal is used to manage an organization's compliance features rather than to access Microsoft's own compliance attestations.
Question 39
HOTSPOT
-
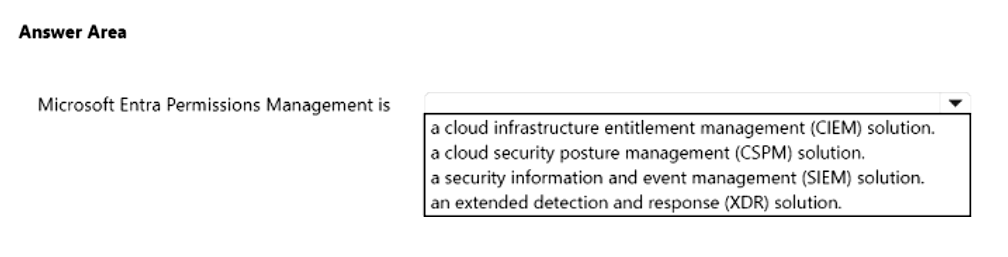
Select the answer that correctly completes the sentence.
Show Answer
Correct Answer: a cloud infrastructure entitlement management (CIEM) solution.
Explanation: Microsoft Entra Permissions Management is Microsoft's CIEM offering, providing visibility and governance of permissions across multi-cloud environments.
Question 41
Which Microsoft Purview solution can be used to identify data leakage?
A. insider risk management
B. Compliance Manager
C. communication compliance
D. eDiscovery
Show Answer
Correct Answer: A
Explanation: Microsoft Purview Insider Risk Management is designed to detect, investigate, and respond to risky insider activities, including potential data leakage and data exfiltration. Compliance Manager assesses compliance posture, Communication Compliance monitors communications for policy violations, and eDiscovery is used to identify and collect content for legal or investigative purposes rather than proactively identifying data leakage.
Question 42
DRAG DROP
-
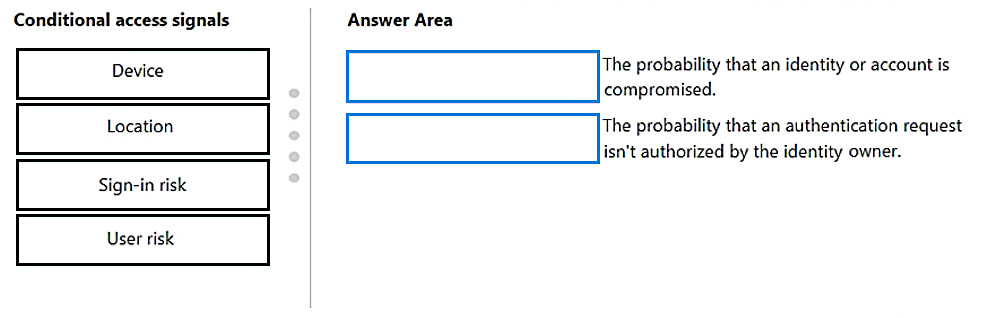
Match the types of Conditional Access signals to the appropriate definitions.
To answer, drag the appropriate Conditional Access signal type from the column on the left to its definition on the right. Each signal type may be used once, more than once, or not at all.
NOTE: Each correct match is worth one point.
Show Answer
Correct Answer: User risk → The probability that an identity or account is compromised.
Sign-in risk → The probability that an authentication request isn't authorized by the identity owner.
Explanation: In Microsoft Entra Conditional Access, User risk measures the likelihood the user account has been compromised, while Sign-in risk measures the likelihood that a specific authentication attempt is not being performed by the legitimate owner.
Question 43
HOTSPOT
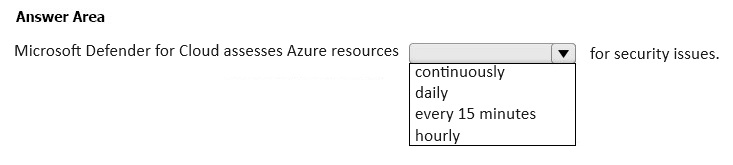
-
Select the answer that correctly completes the sentence.
Show Answer
Correct Answer: continuously
Explanation: Microsoft Defender for Cloud continuously assesses Azure resources for security issues and updates security recommendations as resource states change.
Question 44
When you enable Azure AD Multi-Factor Authentication (MFA), how many factors are required for authentication?
A. 1
B. 2
C. 3
D. 4
Show Answer
Correct Answer: B
Explanation: Multi-Factor Authentication requires two or more verification factors from different categories. Enabling Azure AD (Microsoft Entra ID) MFA adds a second factor to the standard sign-in, so authentication requires two factors.
$19
Get all 235 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.