You have a Microsoft Sentinel workspace.
You need to collect Windows security events from 200 Azure virtual machines that run Windows Server. The solution must meet the following requirements:
Use direct agent-based data collection from each virtual machine.
Use a supported agent for new virtual machine deployments.
Which Microsoft Sentinel connector should you use?
A. Windows Forwarded Events
B. Windows Security Events via AMA
C. Security Events via Legacy Agent
D. Syslog via AMA
E. Azure Resource Graph
Show Answer
Correct Answer: B
Explanation: Use Windows Security Events via AMA. Azure Monitor Agent is supported for new deployments and collects Windows security events directly from each virtual machine using data collection rules.
Question 30
You have an Azure virtual network named VNet1 that contains a subnet named Subnet1.
You create a storage account named storage1.
You need to ensure that access to storage1 can be managed only by a network security group (NSG) linked to Subnet1.
What should you use?
A. an Azure Private link service
B. a service endpoint
C. a private endpoint
D. a user-defined route (UDR)
Show Answer
Correct Answer: C
Explanation: A private endpoint gives storage1 a private IP address in the virtual network. With private endpoint network policies enabled on Subnet1, the NSG linked to that subnet can control traffic to the endpoint. Disable public network access to prevent traffic from bypassing that path.
Question 31
DRAG DROP
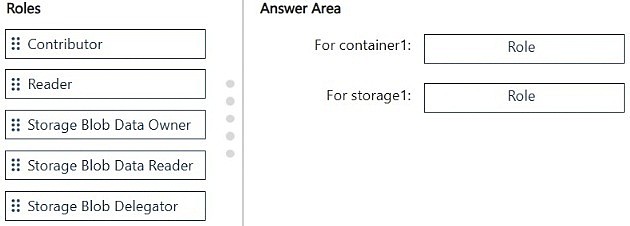
You have an Azure subscription named Sub1 that contains a storage account named storage1. storage1 hosts a blob container named container1.
Sub1 is linked to a Microsoft Entra tenant that contains a security group named Group1.
You need to ensure that Group1 can use the Azure portal to view the blobs in container1. The solution must follow the principle of least privilege.
Which roles should you assign to Group1. To answer, drag the appropriate roles to the correct objects. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: For container1: Storage Blob Data Reader
For storage1: Reader
Explanation: Storage Blob Data Reader grants read access to the blobs. Reader grants the management-plane access needed to navigate the storage account in the Azure portal.
Question 31
HOTSPOT
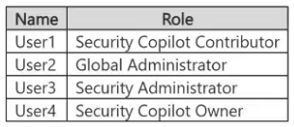
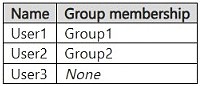
You have a Microsoft Entra tenant that contains the users shown in the following table.
You use Microsoft Security Copilot.
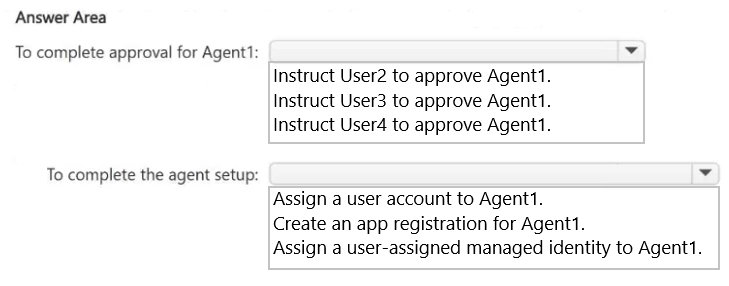
From Microsoft Security Store, User1 attempts to deploy a partner-built agent named Agent1 and reports that the Get agent option is unavailable.
You need to identify whether Agent1 can run in Security Copilot successfully. The solution must follow the principle of least privilege.
How should you complete the deployment? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: To complete approval for Agent1: Instruct User2 to approve Agent1.
To complete the agent setup: Assign a user account to Agent1.
Explanation: Partner-built agent approval requires the Global Administrator role. After approval, Agent1 needs an assigned user account to run in Security Copilot.
Question 32
You have an Azure subscription that contains a virtual network named VNet1.
VNet1 contains an Azure VPN gateway named Gateway1 that is configured for Point-to-Site (P2S) connections.
You have a Microsoft 365 E5 subscription.
You need to configure a VPN authentication method for Gateway1. The solution must enforce Conditional Access policies during VPN sign-ins.
Which authentication method should you configure?
A. a custom IPsec/IKE policy
B. Microsoft Entra authentication
C. certificate authentication
D. forced tunneling
Show Answer
Correct Answer: B
Explanation: Configure Microsoft Entra authentication. Azure VPN Gateway P2S sign-ins using Entra ID can be evaluated against Conditional Access policies. The other options do not provide Conditional Access enforcement.
Question 32
You have an Azure subscription that contains a resource group named RG1.
RG1 contains a Microsoft Security Copilot deployment that is integrated with a Microsoft Sentinel workspace named Workspace1.
Analysts use the Security Copilot standalone experience to retrieve incidents by using the Microsoft Sentinel plugin.
A user named User1 can sign in to Security Copilot but cannot retrieve incidents from Workspace1. You verify that User1 has only the Security Copilot Contributor role.
You need to ensure that User1 can retrieve the incidents. The solution must follow the principle of least privilege and NOT require any configuration changes to Security Copilot.
Which role should you assign to User1?
A. the Security Reader role in Microsoft Entra
B. the Microsoft Sentinel Reader role for Workspace1
C. the Security Copilot Owner role
D. the Security Administrator role in Microsoft Entra
E. the Contributor role in Azure for RG1
Show Answer
Correct Answer: B
Explanation: Assign User1 the Microsoft Sentinel Reader role on Workspace1. The Security Copilot Contributor role permits use of Security Copilot, but the Sentinel plugin accesses workspace data using the signed-in user’s permissions. Sentinel Reader grants the required read access to incidents without broader administrative privileges or Security Copilot configuration changes.
Question 33
You have a virtual network named VNet1 that contains a subnet named Subnet1. Azure App Service is integrated with VNet1. You have an Azure SQL Database logical server named Server1 that contains a database named DB1. Server1 is accessible only by using a public IP address.
You need to ensure that Server does NOT use a public IP address and Azure App Service can still access Server1.
What should you create?
A. a routing table
B. an Azure Private Link service
C. a private endpoint
D. a service endpoint
Show Answer
Correct Answer: C
Explanation: Create a private endpoint for Server1. It assigns the Azure SQL service a private IP address in VNet1, allowing the VNet-integrated App Service to connect privately. You can then disable public network access to the SQL server.
Question 33
DRAG DROP
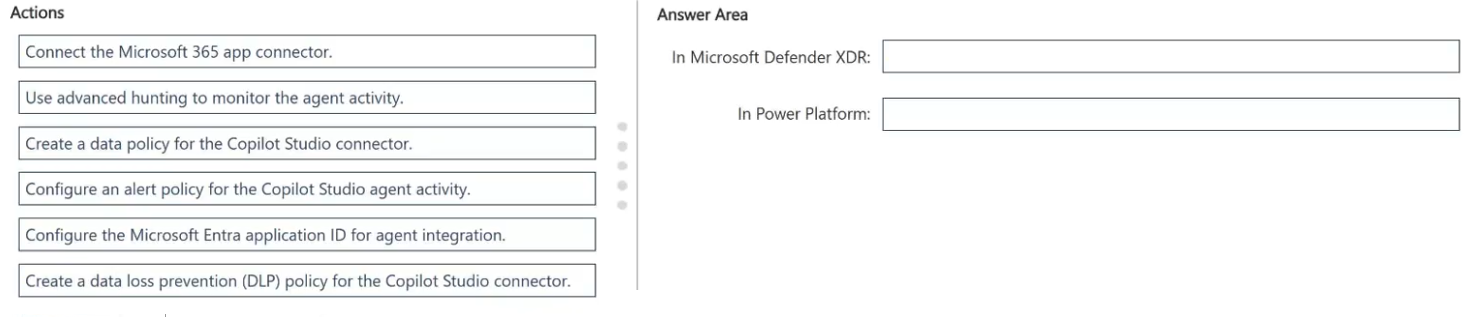
You have a Microsoft Defender XDR environment.
You have a Microsoft Power Platform environment where makers publish custom Microsoft Copilot Studio agents.
You need to enable real-time protection so that suspicious tool invocations are blocked before an agent runs actions, and related alerts appear in the Microsoft Defender portal.
What should you do? To answer, drag the appropriate actions to the correct services. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: In Microsoft Defender XDR: Connect the Microsoft 365 app connector.
In Power Platform: Configure the Microsoft Entra application ID for agent integration.
Explanation: The connector makes agent activity and related alerts available in Defender. The application ID links the agent integration to real-time protection so suspicious tool invocations can be blocked before actions run.
Question 34
HOTSPOT
You have a Microsoft Entra tenant that contains the users shown in the following table.
You have a location named HQ-Trusted that contains the IP address of the corporate network.
The tenant contains a Conditional Access policy named CA1 that has the following settings:
• Assignments:
o Users or agents:
- Include: All users
- Exclude: Group1
• Target resources:
o Resources (formerly cloud apps):
- Include: Office 365
• Conditions:
o Client apps: Not configured
• Access controls:
o Grant:
- Require multifactor authentication
o Grant:
- Require device to be marked as compliant
o For multiple controls:
- Require all the selected controls
The tenant contains a Conditional Access policy named CA2 that has the following settings:
• Assignments:
o Users or agents:
- Include: All users
- Exclude: Group2
• Target resources:
o Resources (formerly cloud apps):
- Include: All resources
• Conditions:
o Locations:
- Configure: Yes
- Include: Any network or location
- Exclude: HQ-Trusted
• Access controls:
o Grant:
- Block access
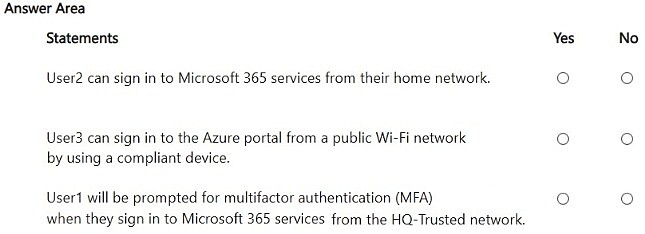
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Show Answer
Correct Answer: User2: Yes
User3: No
User1: No
Explanation: User2 is excluded from the home-network block but must satisfy CA1’s MFA and compliant-device requirements. CA2 blocks User3 on public Wi-Fi, regardless of device compliance. User1 is excluded from CA1, and CA2 does not apply at HQ-Trusted.
Question 34
You have a hybrid environment that contains the following servers:
50 Azure virtual machines that run Windows Server 2019
20 physical, on-premises servers that run Windows Server 2019
All the servers use a third-party antivirus solution that must remain active during a phased security rollout.
You need to onboard all the servers to Microsoft Defender for Endpoint by using a centralized deployment method. The solution must meet the following requirements:
Endpoint detection and response (EDR) capabilities must be enabled.
Antivirus conflicts must be prevented during onboarding.
What should you do on the servers?
A. Set the Microsoft Defender for Endpoint service to Disabled.
B. Disable Microsoft Defender Antivirus real-time protection by using Set-MpPreference.
C. Configure the ForceDefenderPassiveMode registry value.
D. Enable EDR in block mode.
Show Answer
Correct Answer: C
Explanation: Set `ForceDefenderPassiveMode` to 1 on the Windows Server 2019 machines before onboarding. This places Microsoft Defender Antivirus in passive mode so it does not conflict with the active third-party antivirus, while Microsoft Defender for Endpoint’s EDR capabilities remain available.
$19
Get all 130 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.