Professional Cloud Network Engineer Free Practice Questions
This is the free Google Professional Cloud Network Engineer practice question bank —
130 of 251 total questions, each with a full explanation, free to
read with no signup required. Updated 2026-10-13.
Every answer is verified against official Google documentation —
see our methodology.
Question 1
Your company's security team tends to use managed services when possible. You need to build a dashboard to show the number of deny hits that occur against configured firewall rules without increasing operational overhead. What should you do?
A. Configure Firewall Rules Logging. Use Firewall Insights to display the number of hits.
B. Configure Firewall Rules Logging. View the logs in Cloud Logging, and create a custom dashboard in Cloud Monitoring to display the number of hits.
C. Configure a firewall appliance from the Google Cloud Marketplace. Route all traffic through this appliance, and apply the firewall rules at this layer. Use the firewall appliance to display the number of hits.
D. Configure Packet Mirroring on the VPC. Apply a filter with an IP address list of the Denied Firewall rules. Configure an intrusion detection system (IDS) appliance as the receiver to display the number of hits.
Show Answer
Correct Answer: A
Explanation: Enable Firewall Rules Logging and use Firewall Insights to view deny-rule hit counts. It provides a managed way to analyze and display firewall rule activity, avoiding the extra setup and maintenance of a custom Cloud Monitoring dashboard or a separate appliance.
Question 1
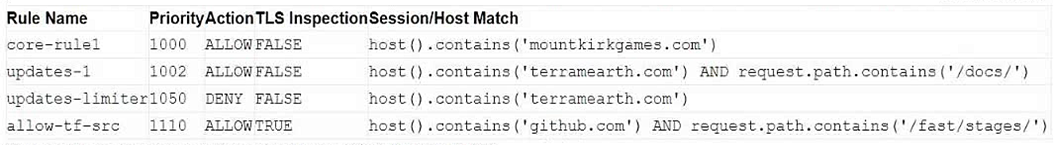
You are reviewing and tuning Secure Web Proxy at your organization, Mount Kirk Games. Users have reported that they are unable to reach the documents they need on the Terram Earth website (https://www.terramearth.com/docs/*). The Secure Web Proxy rules configuration is as follows:
You need to enable access to these documents. What should you do?
A. Delete the updates-limiter rule.
B. Modify the updates-1 rule to perform the TLS inspection.
C. Review Cloud Logging for errors with Cloud NAT. If there are no errors, assign the VM a public IP address.
D. Modify the priority of the updates-limiter rule to 1000.
Show Answer
Correct Answer: B
Explanation: Enable TLS inspection on the updates-1 rule so the Secure Web Proxy can evaluate the HTTPS request’s path and match /docs/. The rule then allows the documents before the lower-priority updates-limiter deny rule is reached.
Question 1
You are designing a highly resilient and secure connection between an on-premises data center and Google Cloud for a financial services company. The company requires 10 Gbps of bandwidth and mandates that all traffic be encrypted end-to-end between their on-premises network and their Google Cloud VPC. You have already provisioned two 10 Gbps Dedicated Interconnect connections. You need to determine an encryption strategy that meets these requirements and provides redundancy.
What should you do?
A. Deploy four HA VPN gateways on each Dedicated Interconnect connection.
B. Deploy two HA VPN gateways on each Dedicated Interconnect connection.
C. Configure MACsec on each of the Dedicated Interconnect connections.
D. Use one Dedicated Interconnect for traffic and an HA VPN over the internet for backup.
Show Answer
Correct Answer: A
Explanation: MACsec encrypts only the physical Interconnect link and does not provide end-to-end encryption into the VPC. An internet HA VPN backup does not satisfy the requirement to use both Dedicated Interconnects for resilient 10 Gbps connectivity. HA VPN over Dedicated Interconnect provides end-to-end IPsec encryption, and to scale to a 10 Gbps attachment while maintaining redundancy, multiple HA VPN gateways/tunnels are required; deploying four HA VPN gateways on each Dedicated Interconnect connection provides the needed tunnel capacity and resilience.
Question 1
Your company acquired a new division. The new division's network team requires complete control over their networking infrastructure. You need to extend your existing Google Cloud network infrastructure, that consists of a single VPC, to allow workloads from all divisions to communicate with each other. You want to avoid incurring extra costs and granting unnecessary permissions to the new division's networking team. What should you do?
A. • Create a new project for the new division's network team. • Create a new VPC within the new project. • Establish a VPC peering between your existing VPC and the new division’s VPC. • Create a new subnet dedicated to the new division's workloads. • Grant roles/compute.networkUser on the new project to the new division’s network team group.
B. • Create a new project for the new division's network team. • Create a new VPC within the new project. • Establish a VPC peering between your existing VPC and the new division’s VPC. • Grant roles/compute.networkAdmin on the newly created project to the new division's network team group.
C. • Ensure that the project hosting the existing network infrastructure is enabled as a host project. • Create a new subnet dedicated to the new division's workloads in the existing VP • Grant roles/compute.networkUser on the newly created subnet to the new division’s network team group.
D. • Create a new project for the new division's network team. • Create a new VPC within the new project. • Establish a VPN connection between your existing VPC and the new division's VPC. • Grant roles/compute.networkAdmin on the newly created project to the new division's network team group.
Show Answer
Correct Answer: B
Explanation: Create a separate project and VPC for the division, then use VPC Network Peering to provide private connectivity with the existing VPC. Granting `roles/compute.networkAdmin` only on the new project lets the division’s team manage its own network resources without giving them control over your existing network. Peering avoids the additional VPN infrastructure costs, although data transfer may still incur charges.
Question 2
You have the following Shared VPC design. VPC Flow Logs is configured for Subnet-1 in the host VPC. You also want to monitor flow logs for Subnet-2. What should you do?
A. Configure a VPC Flow Logs filter for Subnet-2 in the host project VPC.
B. Configure VPC Flow Logs in the service project VPC for Subnet-2.
C. Configure Packet Mirroring in both the host and service project VPCs.
D. Configure a firewall rule to permit Subnet-2 IP addresses outbound in the host project VPC.
Show Answer
Correct Answer: B
Explanation: Subnet-2 is in the VPC shown in the service project, so enable VPC Flow Logs for that subnet in the service project. Flow Logs are configured per subnet; adding a filter to the host project’s VPC does not enable logging for Subnet-2.
Question 2
You are managing a containerized application environment on Google Kubernetes Engine (GKE). You deployed a microservice with a Kubernetes service manifest that defines a named port, http-api, for its main endpoint. You are now configuring an external http(s) load balancer to expose this microservice. You need to ensure the configuration is independent of the actual port number and follows best practices.
What should you do?
A. Create a backend service that uses the GKE node instance group as its backend, and configure the named port http-api in the backend service.
B. Reference the GCE_VM_IP_PORT network endpoint group (NEG) in the backend configuration that was automatically created for your Kubernetes service, and specify http-api named port for traffic.
C. Add an annotation to your Kubernetes service manifest to create a GCE_VM_IP network endpoint group (NEG), and configure the backend service to use this NEG.
D. Add an annotation in your Kubernetes ingress manifest to specify the http-api port number directly, and configure the backend service to use this hardcoded port number.
Show Answer
Correct Answer: B
Explanation: For GKE HTTP(S) load balancing, container-native load balancing uses Network Endpoint Groups (NEGs) that target Pod IPs and ports directly. The backend service can reference the automatically created GCE_VM_IP_PORT NEG, allowing traffic to be directed using the Kubernetes Service's named port rather than depending on a hardcoded port number. This keeps the configuration decoupled from the actual numeric port and follows GKE best practices.
Question 3
You have the networking configuration shown in the diagram. Two VLAN attachments associated with two Dedicated Interconnect connections terminate on the same Cloud Router (mycloudrouter). The Interconnect connections terminate on two separate on-premises routers. You advertise the same prefixes from the Border Gateway Protocol (BGP) sessions associated with each of the VLAN attachments.
You notice an asymmetric traffic flow between the two Interconnect connections. Which of the following actions should you take to troubleshoot the asymmetric traffic flow?
A. From the Google Cloud console, navigate to Cloud Logging to view VPC Flow Logs and review the results.
B. From the Cloud CLI, run gcloud compute –-project PROJECT_ID routers get-status mycloudrouter –-region REGION and review the results.
C. From the Google Cloud console, navigate to the Hybrid Connectivity, select the Cloud Router, and view BGP sessions.
D. From the Cloud CLI, run gcloud compute routers describe mycloudrouter –-region REGION and review the results.
Show Answer
Correct Answer: B
Explanation: Run `gcloud compute routers get-status` to inspect the Cloud Router’s live BGP session status and learned routes, including which paths are selected for the prefixes. `describe` shows the router’s configuration, not its current routing status.
Sources:
https://cloud.google.com/network-connectivity/docs/router/support/troubleshoot-bgp-sessions
https://cloud.google.com/network-connectivity/docs/interconnect/concepts/dedicated-overview
Question 3
Your company utilizes Network Connectivity Center (NCC) to facilitate communication between numerous spoke VPCs. A development team reports that their application instances in app-dev-spoke-vpc are unable to connect to a new database service located in db-dev-spoke-vpc. You need to diagnose this issue using an observability tool and determine the root cause. What should you do?
A. Use Firewall Insights to analyze the firewall rule configuration and modify the appropriate rule.
B. Check each firewall rule in both the app-dev-spoke-vpc and db-dev-spokevpc.
C. Verify that the application instances in app-dev-spoke-vpc connected to Network Connectivity Center are assigned external IP addresses to reach the database service.
D. Use Network Intelligence Center’s Connectivity Tests to perform a reachability analysis between an instance in app-dev-spoke-vpc and the database service in db-dev-spoke-vpc.
Show Answer
Correct Answer: D
Explanation: Connectivity Tests in Network Intelligence Center is the observability tool designed to perform end-to-end reachability analysis across Google Cloud networking, including Network Connectivity Center, routes, firewall rules, and other dependencies. It identifies the point of failure and helps determine the root cause. Firewall Insights focuses specifically on firewall configuration, while manually inspecting firewall rules is not the recommended observability approach, and external IP addresses are not required for communication between spoke VPCs connected through NCC.
Question 4
You have the following firewall ruleset applied to all instances in your Virtual Private Cloud (VPC):
You need to update the firewall rule to add the following rule to the ruleset:
You are using a new user account. You must assign the appropriate identity and Access Management (IAM) user roles to this new user account before updating the firewall rule. The new user account must be able to apply the update and view firewall logs. What should you do?
A. Assign the compute.securityAdmin and logging.viewer rule to the new user account. Apply the new firewall rule with a priority of 50.
B. Assign the compute.securityAdmin and logging.bucketWriter role to the new user account. Apply the new firewall rule with a priority of 150.
C. Assign the compute.orgSecurityPolicyAdmin and logging.viewer role to the new user account. Apply the new firewall rule with a priority of 50.
D. Assign the compute.orgSecurityPolicyAdmin and logging.bucketWriter role to the new user account. Apply the new firewall rule with a priority of 150.
Show Answer
Correct Answer: A
Explanation: Assign `compute.securityAdmin` to let the user manage VPC firewall rules and `logging.viewer` to let them view firewall logs. Use priority 50 so the more-specific `/32` rule is evaluated before the existing `/24` rule at priority 100; lower numeric priorities take precedence.
Question 4
You manage your company's network security and have noticed unusual outbound traffic from a Compute Engine VM that is part of a production subnet. You suspect the VM may be compromised, because it is attempting to communicate with a malicious external IP address. You want to capture detailed metadata for every IP connection to and from this specific VM. including source/destination IP, port, protocol, and the amount of data transferred. What should you do?
A. • Enable VPC Flow Logs on the subnet containing the VM. • Set the sampling rate to 1.0 for maximum detail, and filter the logs in Cloud Logging for the VM's IP address.
B. • Navigate to Network Intelligence Center, and run a new connectivity test for the VM. • Analyze the report to see which configurations are allowing the traffic.
C. • Use Packet Mirroring to create a real-time copy of all network packets from the suspected VM. • Forward the copies to a collector VM for analysis.
D. • Create a new egress firewall rule with a priority of 65535 that allows all outbound traffic. • Enable Firewall Rules Logging on this new rule to capture all connection details.
Show Answer
Correct Answer: A
Explanation: VPC Flow Logs are designed to capture network flow metadata such as source/destination IP addresses, ports, protocol, bytes transferred, and other connection details. Enabling them on the subnet and setting the sampling rate to 1.0 maximizes visibility, after which logs can be filtered for the specific VM. Connectivity Tests analyze reachability rather than recording traffic, Packet Mirroring captures full packet payloads and is intended for deep packet inspection rather than metadata collection, and Firewall Rules Logging only logs firewall rule matches rather than every IP connection.
$19
Get all 251 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.