A penetration tester obtains a regular domain user’s set of credentials. The tester wants to attempt a dictionary attack by creating a custom word list based on the Active Directory password policy.
Which of the following tools should the penetration tester use to retrieve the password policy?
A. Responder
B. CrackMapExec
C. Hydra
D. msfvenom
Show Answer
Correct Answer: B
Explanation: CrackMapExec can enumerate Active Directory information, including the domain password policy, using valid domain credentials. Those policy details (such as minimum length, complexity, and lockout settings) are useful for building a targeted dictionary. Responder captures credentials, Hydra performs online password attacks, and msfvenom generates payloads rather than retrieving AD password policies.
Question 131
HOTSPOT
-
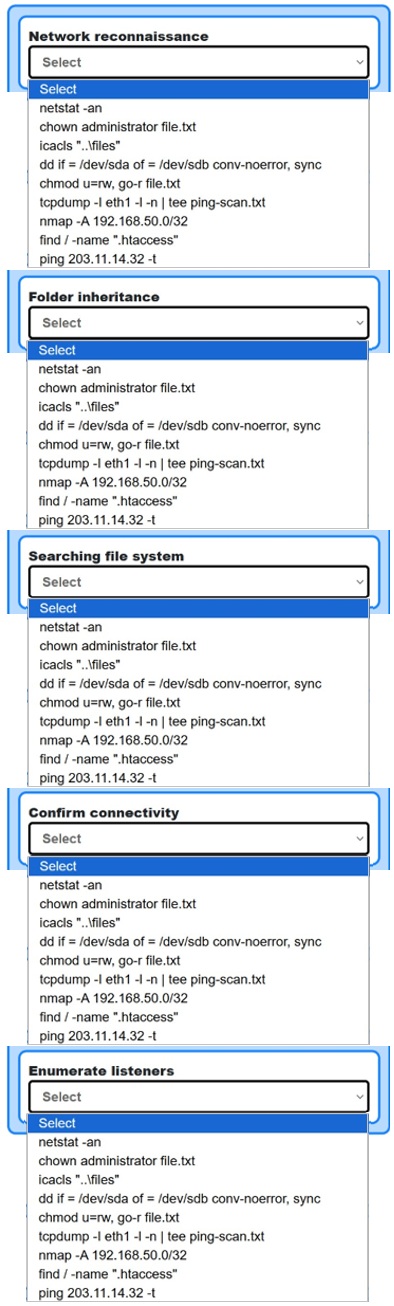
A security analyst is asked to perform various techniques to assess organizational security.
INSTRUCTIONS
-
Select the command that will successfully accomplish each objective.
Commands may only be used once.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Explanation: Use tcpdump to capture reconnaissance traffic, icacls for NTFS inheritance/ACLs, find to locate files, ping to verify reachability, and netstat to list listening/network sockets.
Question 132
HOTSPOT
-
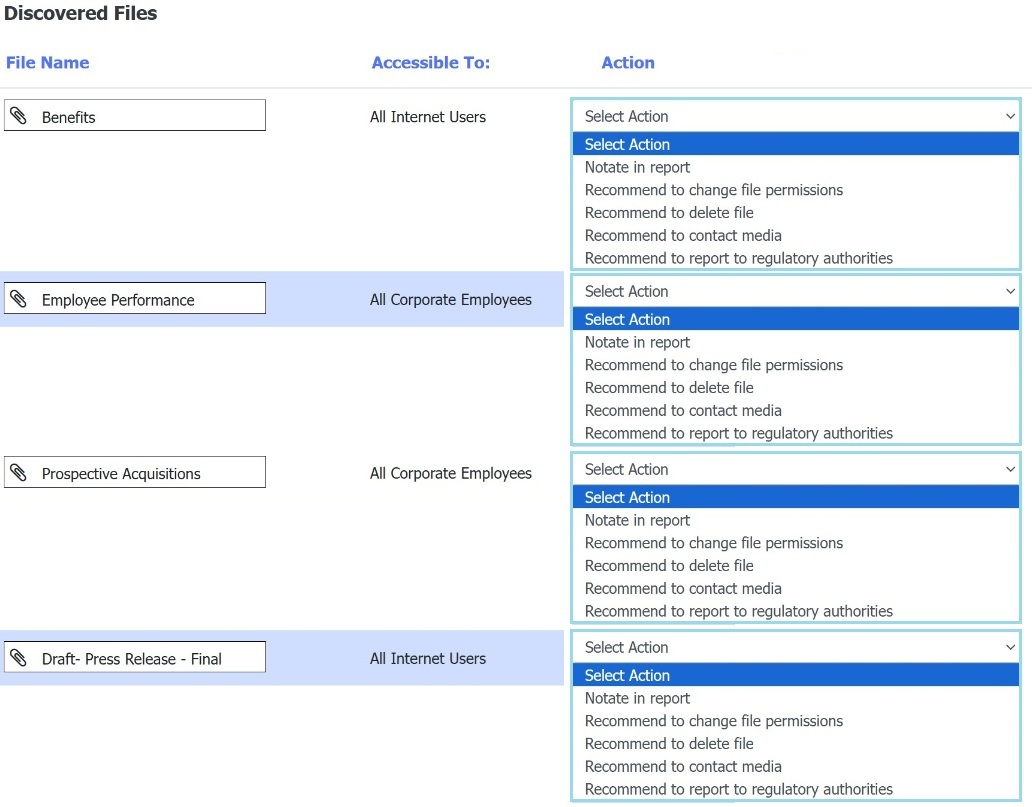
A penetration tester has identified a series of files throughout an assessment.
INSTRUCTIONS
-
Select the most appropriate action the penetration tester should take for each file.
The same action may be selected multiple times.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Show Answer
Correct Answer: Benefits — Recommend to change file permissions
Employee Performance — Recommend to change file permissions
Prospective Acquisitions — Recommend to change file permissions
Draft- Press Release - Final — Notate in report
Explanation: Public or overly broad access to internal business files should be corrected by restricting permissions. A finalized public press release being accessible to internet users is expected and only warrants documentation if discovered during the assessment.
Question 133
A penetration tester is attempting to exfiltrate sensitive data from a client environment without alerting the client’s blue team.
Which of the following exfiltration methods most likely remain undetected?
A. Cloud storage
B. Email
C. Domain Name System
D. Test storage sites
Show Answer
Correct Answer: C
Explanation: DNS is commonly allowed through network defenses and can be abused as a covert channel for data exfiltration using DNS queries. Compared with email, cloud storage, or public test storage sites, DNS traffic has historically been less scrutinized in many environments, making it the most likely option to remain undetected.
Question 136
A penetration tester sets up a C2 server to manage and control payloads deployed in the target network.
Which of the following tools is the most suitable for establishing a robust and stealthy connection?
A. ProxyChains
B. Covenant
C. PsExec
D. sshuttle
Show Answer
Correct Answer: B
Explanation: Covenant is a dedicated command-and-control (C2) framework used by penetration testers to manage implants/payloads, task compromised hosts, and maintain communications. ProxyChains only routes traffic through proxies, PsExec is for remote execution/administration on Windows, and sshuttle creates VPN-like SSH tunnels rather than providing C2 infrastructure.
Question 137
A penetration tester uses the Intruder tool from the Burp Suite Community Edition while assessing a web application. The tester notices the test is taking too long to complete.
Which of the following tools can the tester use to accelerate the test and achieve similar results?
A. TruffleHog
B. Postman
C. Wfuzz
D. WPScan
Show Answer
Correct Answer: C
Explanation: Burp Suite Community Edition intentionally throttles Intruder, making large fuzzing campaigns slow. Wfuzz is a fast command-line web fuzzing tool that provides similar capabilities for parameter, content, and authentication fuzzing, making it a common alternative. TruffleHog scans for secrets, Postman is for API development/testing rather than high-speed fuzzing, and WPScan is specialized for WordPress security.
Question 138
A penetration tester discovers a deprecated directory in which files are accessible to anyone.
Which of the following would most likely assist the penetration tester in finding sensitive information without raising suspicion?
A. Enumerating cached pages available on web pages
B. Looking for externally available services
C. Scanning for exposed ports associated with the domain
D. Searching for vulnerabilities and potential exploits
Show Answer
Correct Answer: A
Explanation: Enumerating cached pages is a passive reconnaissance technique that can reveal sensitive information indexed by search engines or caches without actively interacting with the target system, making it less likely to trigger monitoring. The other options involve active enumeration or vulnerability assessment that is more likely to be detected.
Question 139
A penetration tester gains initial access to a Windows workstation on a client’s network. The tester wants to determine the next target but does not want to install software on the workstation.
Which of the following is the best tool to list potential targets?
A. mmc.exe
B. Netstat
C. Mimikatz
D. explorer.exe
E. CME
Show Answer
Correct Answer: B
Explanation: Netstat is a native Windows command-line utility that requires no additional installation and can reveal active network connections and listening ports, helping identify other hosts the workstation communicates with, such as servers or domain controllers. The other options are either administrative shells (mmc.exe), the Windows file manager (explorer.exe), credential dumping/offensive tooling (Mimikatz), or an external post-exploitation tool (CME) that would typically require introducing software.
Question 140
A tester compromises a shared host that is manually audited every week due to the absence of a SIEM.
Which of the following is the best way to reduce the chances of being detected?
A. Modify files located in the /var/log directory.
B. Use the clear command to remove recent terminal activity.
C. Perform commands under one of the developer accounts.
D. Disable all logging services on the host.
Show Answer
Correct Answer: C
Explanation: The best choice is C. On a shared host with manual weekly log review, operating under an existing legitimate developer account is more likely to blend with expected activity than altering logs or disabling logging, both of which are highly suspicious. Clearing the terminal only affects the local display and does not remove shell history or system logs.
Question 141
A penetration tester is investigating a buffer overflow on the myfile binary. The tester wants to send a payload to help identify the exact offset to inject the memory address to take control of the buffer.
Which of the following would allow the penetration tester to quickly identify the offset?
A. ./myfile < $(printf ‘A%.0s’ {1.1000}
B. echo ‘A’ |head -n 1000 |tr -d ‘\n’ | ./myfile
C. python -c ‘print(“A”*1000)’ > test.txt; cat test.txt >./myfile
D. ./pattern_create.rb 1000 > test.txt; ./myfile < test.txt
Show Answer
Correct Answer: D
Explanation: A cyclic (non-repeating) pattern generated by pattern_create.rb is specifically designed to determine the exact overwrite offset in a buffer overflow. After the program crashes, the overwritten instruction pointer value can be matched back to the unique pattern to calculate the precise offset. Filling the input with only 'A' characters can trigger a crash but cannot identify the exact offset.
$19
Get all 342 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.