A penetration tester needs to quickly transfer an exploit from a Linux system to a Windows 10 system within the network. Which of the following is the best way to accomplish this task?
A. nc -lvp 8080
B. nc -lnvp 443
C. python3 -m http.server 80
D. neat -lvp 8080
Show Answer
Correct Answer: C
Explanation: The quickest and most straightforward method is to start a simple HTTP server on the Linux host with `python3 -m http.server 80`, allowing the Windows 10 system to download the exploit using a browser, PowerShell (`Invoke-WebRequest`), or `curl`. The `nc` listener options create raw TCP listeners rather than an easy file-hosting service, and `neat` is not the appropriate command.
Question 107
A penetration tester gained a foothold within a network. The penetration tester needs to enumerate all users within the domain. Which of the following is the best way to accomplish this task?
A. pwd.exe
B. net.exe
C. sc.ехе
D. msconfig.exe
Show Answer
Correct Answer: B
Explanation: The correct choice is net.exe. In a Windows domain, the built-in net utility can enumerate domain users using commands such as 'net user /domain'. The other options do not enumerate domain user accounts: pwd.exe displays the current directory (or is not a standard Windows enumeration tool), sc.exe manages/services, and msconfig.exe is a system configuration utility.
Question 108
A company's incident response team determines that a breach occurred because a penetration tester left a web shell. Which of the following should the penetration tester have done after the engagement?
A. Enable a host-based firewall on the machine
B. Remove utilized persistence mechanisms on client systems
C. Revert configuration changes made during the engagement
D. Turn off command-and-control infrastructure
Show Answer
Correct Answer: B
Explanation: A web shell is a persistence mechanism left on a target system. After a penetration test, the tester should remove any persistence mechanisms and artifacts they deployed to restore the environment and prevent unintended access. While reverting configuration changes is also good practice, the specific cause of the breach was the leftover web shell, making removal of persistence mechanisms the best answer.
Question 109
Which of the following differentiates MITRE ATT&CK from PTES?
A. MITRE ATT&CK emphasizes real-world adversary behavior patterns, while PTES outlines structured test phases
B. MITRE ATT&CK defines risk scoring models for vulnerabilities, while PTES focuses on defensive controls.
C. MITRE ATT&CK organizes asset inventories, while PTES provides data breach response procedures
D. MITRE ATT&CK provides detailed exploit code samples, while PTES focuses on threat actor profiles
Show Answer
Correct Answer: A
Explanation: MITRE ATT&CK is a knowledge base that catalogs real-world adversary tactics, techniques, and procedures (TTPs) based on observed behavior. PTES (Penetration Testing Execution Standard) defines a structured methodology and phases for conducting penetration tests, from pre-engagement through reporting. The other options incorrectly describe the purpose of either framework.
Question 110
After obtaining a reverse shell, a penetration tester identifies a locally cloned Git repository that contains thousands of files and directories on a Windows machine. The tester suspects there could be sensitive information related to "ProjectX." Which of the following commands should the tester use in a script to identify potential files to produce the best results?
A. gc * | select "ProjectX"
B. dir /R | findstr "ProjectX"
C. Get-ChildItem * | Select-String "ProjectX"
D. gci -Path . -Recurse | Select-String -Pattern "ProjectX"
Show Answer
Correct Answer: D
Explanation: The goal is to search a large directory tree recursively for occurrences of the string "ProjectX." `gci -Path . -Recurse` (alias for `Get-ChildItem`) enumerates files and directories under the current path recursively, and piping to `Select-String -Pattern "ProjectX"` searches file contents for the pattern. The other options are either non-recursive, search directory listings or alternate data streams rather than contents, or misuse cmdlets for this task.
Question 111
A tester compromises a target host and then wants to maintain persistent access. Which of the following is the best way for the attacker to accomplish the objective?
A. Configure and register a service
B. Install and run remote desktop software
C. Set up a script to be run when users log in.
D. Perform a kerberoasting attack on the host
Show Answer
Correct Answer: A
Explanation: Configuring and registering a service is a well-established persistence technique. Services can be configured to start automatically at boot, do not depend on a user logging in, and often run with elevated privileges, making them a reliable method for maintaining long-term access. Running remote desktop software is not inherently persistent or stealthy, a logon script only executes when a user logs in, and kerberoasting is a credential attack rather than a persistence mechanism.
Question 114
A penetration tester identifies an exposed corporate directory containing first and last names and phone numbers for employees. Which of the following attack techniques would be the most effective to pursue if the penetration tester wants to compromise user accounts?
A. Smishing
B. Impersonation
C. Tailgating
D. Whaling
Show Answer
Correct Answer: A
Explanation: Smishing is the most effective choice because the exposed directory provides employees' names and phone numbers, enabling targeted SMS phishing messages that can trick users into revealing credentials or visiting credential-harvesting sites. Impersonation is a broader tactic rather than the best-matched attack vector here, tailgating targets physical access, and whaling focuses on high-profile executives rather than general user accounts.
Question 115
HOTSPOT
-
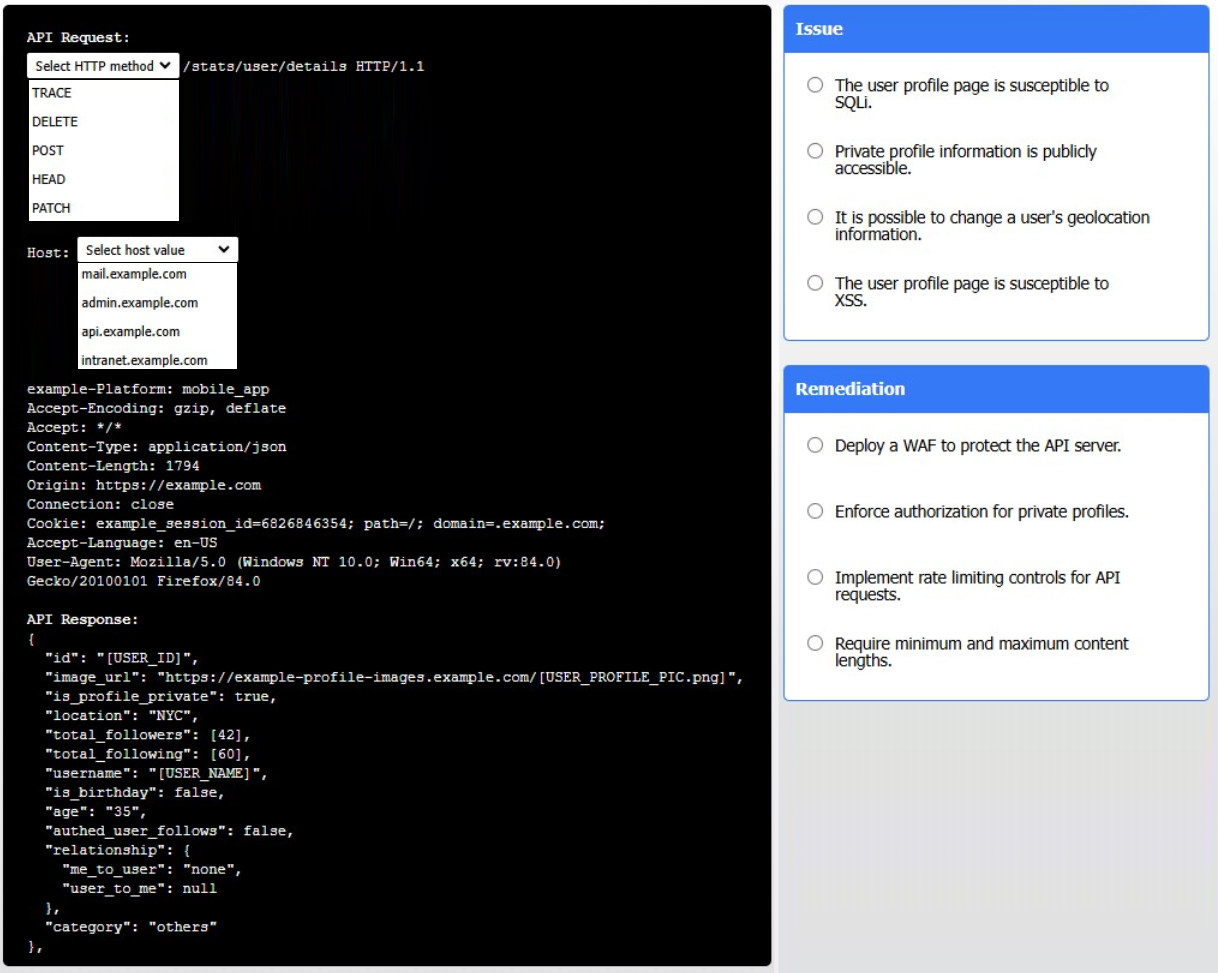
A penetration tester is performing an assessment for an application that allows users to follow other individuals, if those individuals accept.
The request is performed from a newly created account that is not actively following or being followed by any other users and is targeting a private user profile.
INSTRUCTIONS
-
Use the drop-down menus to select the most appropriate code segment for each of the first two lines in the API request.
Then identify the issue within the response and select the appropriate remediation to resolve the vulnerability.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Show Answer
Correct Answer: GET
api.example.com
Issue: Private profile information is publicly accessible.
Remediation: Enforce authorization for private profiles.
Explanation: The endpoint retrieves user profile details, so GET to the API host is appropriate. The response exposes details despite "is_profile_private": true and no follower relationship, indicating missing authorization checks on private profiles.
Question 116
During a wireless penetration assessment for a small business client, a tester attempts to capture wireless packets. However, whenever the tester sets the capture device to monitor mode, it fails to see the client's wireless network, as provided by the scope. Which of the following is the most likely reason for this issue?
A. The clients network uses 6GHz and not 5GHz/2.4GHz
B. The tester misconfigured the capture device
C. The client provided the wrong SSID for the network
D. The tester is not using Aircrack-ng
Show Answer
Correct Answer: A
Explanation: The most likely cause is that the target WLAN operates exclusively on the 6 GHz band (Wi-Fi 6E) while the tester's capture adapter supports monitor mode only for 2.4/5 GHz. In that case, monitor mode can be enabled successfully, but the network will not appear because the hardware cannot receive that band. The other options are less likely: misconfiguration is possible but not the best explanation, an incorrect SSID would not prevent seeing nearby beacon frames, and Aircrack-ng is not required to detect networks in monitor mode.
Question 117
A penetration tester downloads a JAR file that is used in an organization’s production environment. The tester evaluates the contents of the JAR file to identify potentially vulnerable components that can be targeted for exploit. Which of the following describes the tester's activities?
A. SAST
B. SBOM
C. ICS
D. SCA
Show Answer
Correct Answer: D
Explanation: Software Composition Analysis (SCA) examines packaged applications such as JAR files to identify included third-party/open-source components and their versions, then checks them against known vulnerability databases. SAST analyzes source code, SBOM is an inventory of components rather than the analysis activity, and ICS refers to industrial control systems.
$19
Get all 342 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.