This is the free Amazon SOA-C03 practice question bank —
100 of 194 total questions, each with a full explanation, free to
read with no signup required. Updated 2026-10-13.
Every answer is verified against official Amazon documentation —
see our methodology.
Question 1
A company uses AWS Lambda to process files that users upload to an Amazon S3 bucket. When a user uploads a file to the S3 bucket, S3 Event Notifications invokes a Lambda function to process the file.
The company wants to automatically invoke the Lambda function only for flies with a .txt extension that users upload to the S3 bucket.
Which solution will meet these requirements?
A. Configure a Lambda function that is invoked by S3 PUT requests for .txt files in the S3 bucket.
B. Configure a Lambda function that is invoked by S3 GET requests for .txt files in the S3 bucket.
C. Configure an S3 bucket notification to send all object creation events to an Amazon SNS topic. Subscribe the Lambda function to the SNS topic. Apply a filter policy on the SNS topic for .txt file extensions.
D. Modify the existing S3 Event Notifications configuration to send events for .txt file uploads to Amazon CloudWatch Logs to invoke the existing Lambda function.
Show Answer
Correct Answer: A
Explanation: Amazon S3 Event Notifications support filtering by object key name prefix and suffix. Configure the S3 bucket notification for ObjectCreated (PUT) events with a suffix filter of .txt so the Lambda function is invoked only when .txt files are uploaded. GET requests do not trigger upload processing, SNS filter policies do not filter on S3 object key suffix in this way, and CloudWatch Logs cannot be used to invoke Lambda from S3 event notifications.
Question 1
A company has a VPC that contains a public subnet and a private subnet. The company deploys an Amazon EC2 instance that uses an Amazon Linux Amazon Machine Image (AMI) and has the AWS Systems Manager Agent (SSM Agent) installed in the private subnet. The EC2 instance is in a security group that allows only outbound traffic.
A CloudOps engineer needs to give a group of privileged administrators the ability to connect to the instance through SSH without exposing the instance to the internet.
Which solution will meet this requirement?
A. Create an EC2 Instance Connect endpoint in the private subnet. Update the security group to allow inbound SSH traffic. Create an IAM group for privileged administrators. Assign the PowerUserAccess managed policy to the IAM group.
B. Create a Systems Manager endpoint in the private subnet. Update the security group to allow SSH traffic from the private network where the Systems Manager endpoint is connected. Create an IAM group for privileged administrators. Assign the PowerUserAccess managed policy to the IAM group.
C. Create an EC2 Instance Connect endpoint in the public subnet. Update the security group to allow SSH traffic from the private network. Create an IAM group for privileged administrators. Assign the PowerUserAccess managed policy to the IAM group.
D. Create a Systems Manager endpoint in the public subnet. Create an IAM role that has the AmazonSSMManagedInstanceCore permission for the EC2 instance. Create an IAM group for privileged administrators. Assign the AmazonEC2ReadOnlyAccess IAM policy to the IAM group.
Show Answer
Correct Answer: A
Explanation: An EC2 Instance Connect Endpoint provides a private path for administrators to SSH to an instance without assigning it public internet access. Allow inbound SSH on the instance security group from the endpoint’s security group, and grant the administrator group the required EC2 Instance Connect permissions. Systems Manager endpoints alone do not provide the SSH access and permissions described in B or D.
Question 1
A company wants to create an automated solution for all accounts managed by AWS Organizations to detect any security groups that use 0.0.0.0/0 as the source address for inbound traffic. The company also wants to automatically remediate any noncompliant security groups by restricting access to a specific CIDR block that corresponds with the company's intranet.
Which set of actions should the CloudOps engineer take to create a solution?
A. Create an AWS Config rule to detect noncompliant security groups. Set up automatic remediation to change the 0.0.0.0/0 source address to the approved CIDR block.
B. Create an IAM policy to deny the creation of security groups that have 0.0.0.0/0 as the source address. Attach this IAM policy to every user in the company.
C. Create an AWS Lambda function to inspect new and existing security groups. Check for a noncompliant 0.0.0.0/0 source address and change the source address to the approved CIDR block.
D. Create a service control policy (SCP) for the organizational unit (OU) to deny the creation of security groups that have the 0.0.0.0/0 source address. Set up automatic remediation to change the 0.0.0.0/0 source address to the approved CIDR block.
Show Answer
Correct Answer: A
Explanation: AWS Config can evaluate security groups for inbound rules that allow 0.0.0.0/0 and use automatic remediation to replace the source with the company-approved CIDR block. The configuration can be deployed across the organization’s accounts. IAM policies and SCPs can prevent some future changes but do not remediate existing noncompliant rules.
Question 1
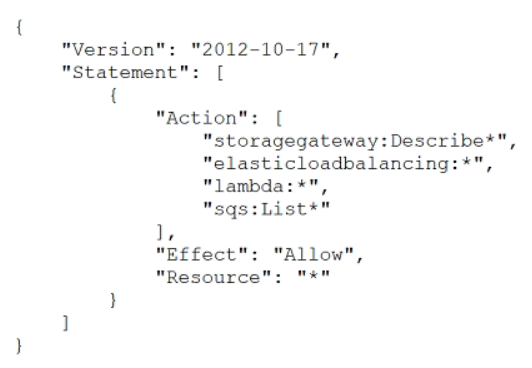
A CloudOps engineer must create an IAM policy for a developer who needs access to specific AWS services. Based on the requirements, the CloudOps engineer creates the following policy:
Which actions does this policy allow? (Choose two.)
A. Create an AWS Storage Gateway.
B. Create an IAM role for an AWS Lambda function.
C. Delete an Amazon SQS queue.
D. Describe AWS load balancers.
E. Invoke an AWS Lambda function.
Show Answer
Correct Answer: D, E
Explanation: The policy allows all `elasticloadbalancing` actions, including describing load balancers, and all `lambda` actions, including invoking a Lambda function. It does not grant `iam:CreateRole`, `sqs:DeleteQueue`, or a Storage Gateway creation action.
Question 2
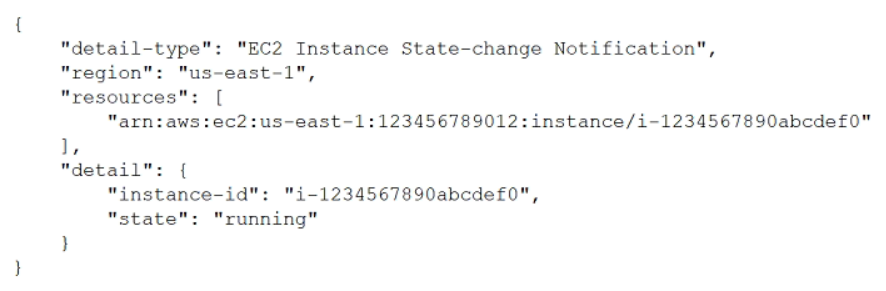
A development team wants to match events on Amazon EventBridge where the state of an Amazon EC2 machine is not "terminated".
An example event is as follows:
Which event pattern should the development team use to find relevant events?
A. {"detail": {"state": ["not equals-ignore-case": "terminated"]}}
B. {"detail": {"state": ["! equals-ignore-case": "terminated"]}}
C. {"detail": {"state": ["equals-ignore-case": "terminated"]}}
D. {"detail": {"state": [{"anything-but": {"equals-ignore-case": "terminated"}}]}}
Show Answer
Correct Answer: D
Explanation: Use `anything-but` to exclude the `terminated` state, with `equals-ignore-case` nested inside it so the comparison is case-insensitive. Option D has the required EventBridge event-pattern structure.
Question 2
An ecommerce company hires a cybersecurity company to audit the ecommerce company's AWS account. The cybersecurity company requests read-only access to the account. The ecommerce company creates an IAM role, adds a trust relationship with the cybersecurity company's AWS account, and adds read-only permissions to the ecommerce company's account.
An employee at the cybersecurity company unsuccessfully tries to assume the read-only role that the ecommerce company created.
A CloudOps engineer at the ecommerce company must resolve the access issue.
Which solution will meet this requirement?
A. Configure multi-factor authentication (MFA).
B. Configure an identity provider by using OpenID Connect (OIDC).
C. Create a policy that allows the sts:AssumeRole action. Add the policy to the cybersecurity employee's role. Ensure that the resource for the policy is the role that the employee needs to assume.
D. Create a policy that allows the sts:SetSourceIdentity action. Add the policy to the cybersecurity employee's role. Ensure that the resource for the policy is in the ecommerce company's account.
Show Answer
Correct Answer: C
Explanation: Cross-account role assumption requires both a trust policy on the target role and an identity-based policy in the source account that permits sts:AssumeRole on the target role. The trust relationship alone is not sufficient. MFA and OIDC are not required for this scenario, and sts:SetSourceIdentity does not grant permission to assume a role.
Question 2
A company is implementing Cross-Region Replication (CRR) for the company’s Amazon S3 buckets. The S3 buckets are in the us-east-1 Region. The company uses server-side encryption with Amazon S3 managed keys (SSE-S3) to secure the data in the buckets.
A CloudOps engineer creates a new AWS account to store backups in S3 buckets. All backup buckets are in the us-west-2 Region. The CloudOps engineer enables versioning on the source buckets and the destination buckets. The CloudOps engineer creates an IAM role in the source account for s3.amazonaws.com. The CloudOps engineer grants the IAM role permissions to perform read actions in the source buckets, replicate actions in the destination buckets, and encrypt actions that use the destination bucket's key. The destination bucket policy allows the IAM role to perform replicate and read actions.
After the replication configuration is complete, the CloudOps engineer notices that objects are not replicating.
What is the likely reason the objects are not replicating?
A. The IAM role and bucket policies must have the ObjectOwnerOverrideToBucketOwner permission.
B. The objects in the source buckets and destination buckets must be encrypted by multi-Region keys.
C. Gateway VPC endpoints for Amazon S3 must be created in the source accounts and the destination account.
D. The destination buckets must use server-side encryption with AWS KMS keys (SSE-KMS).
Show Answer
Correct Answer: A
Explanation: For cross-account replication that transfers replica ownership to the destination account, the replication role and destination bucket policy must allow `s3:ObjectOwnerOverrideToBucketOwner`. SSE-S3 does not require KMS permissions or multi-Region keys, and S3 VPC endpoints are not required for replication. (The ownership-override permission is needed when that ownership transfer is configured.)
Question 2
A company is building a web application on AWS. The company is using Amazon CloudFront with a domain name of www.example.com. All traffic to CloudFront must be encrypted in transit. The company already has provisioned an SSL certificate for www.example.com in AWS Certificate Manager (ACM).
Which combination of steps should a CloudOps engineer take to encrypt the traffic in transit? (Choose two.)
A. For each cache behavior in the CloudFront distribution, modify the Viewer Protocol Policy setting to redirect HTTP to HTTPS.
B. For each cache behavior in the CloudFront distribution, modify the Viewer Protocol Policy setting to allow HTTP and HTTPS.
C. Enter the alternate domain name (CNAME) of www.example.com for the CloudFront distribution. Select the custom SSL certificate.
D. Configure an AWS WAF web ACL for the CloudFront distribution.
E. Configure CloudFront Origin Shield for the CloudFront origin.
Show Answer
Correct Answer: A, C
Explanation: Set each cache behavior to redirect HTTP requests to HTTPS, and configure www.example.com as the distribution’s alternate domain name with the ACM custom SSL certificate. This enables CloudFront to serve the domain over HTTPS and direct viewers to the encrypted connection.
Question 3
A healthcare company uses Amazon SageMaker within a VPC to build machine learning (ML) models that use data that is stored in Amazon S3 buckets. The company wants to ensure that SageMaker accesses the data securely without using public IP addresses.
Which solution will meet this requirement?
A. Create Amazon S3 gateway endpoints. Configure SageMaker to access the S3 buckets by using AWS PrivateLink.
B. Provision a NAT gateway within the same VPC where the company runs SageMaker. Configure SageMaker to access the S3 buckets by using the NAT gateway.
C. Configure an AWS Site-to-Site VPN connection to connect SageMaker to the S3 buckets.
D. Configure AWS Transit Gateway to route traffic from SageMaker to the S3 buckets.
Show Answer
Correct Answer: A
Explanation: Amazon SageMaker running in a VPC can access Amazon S3 privately by using an Amazon S3 VPC gateway endpoint. This keeps traffic on the AWS network without requiring public IP addresses or a NAT gateway. AWS PrivateLink is used for interface VPC endpoints for many AWS services, while S3 private VPC access is provided via the S3 gateway endpoint. Site-to-Site VPN and Transit Gateway are not used for private access from a VPC to S3.
Question 3
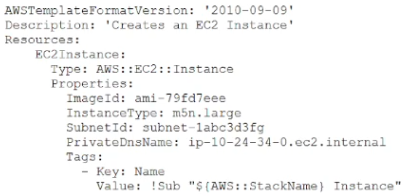
A CloudOps engineer is examining the following AWS CloudFormation template:
Why will the stack creation fail?
A. The Outputs section of the CloudFormation template was omitted.
B. The Parameters section of the CloudFormation template was omitted.
C. The PrivateDnsName cannot be sot from a CloudFormation template.
D. The VPC was not specified in the CloudFormation template.
Show Answer
Correct Answer: C
Explanation: `PrivateDnsName` is not a configurable property of `AWS::EC2::Instance`; AWS assigns the instance’s private DNS name. CloudFormation will reject the unsupported property. Outputs and Parameters are optional, and a VPC can be determined from the specified subnet.
$19
Get all 194 questions with detailed answers and explanations
Instant download HTML + PDF delivered the moment payment clears.
Secure Stripe checkout we never see or store your card details.
7-day refund if files are defective see our refund policy.